Hardware Hacking 101
Introduction to hardware hacking for web and mobile security professionals, covering essential tools, techniques, and protocols like UART, SPI, and JTAG. Hands-on examples and practical insights for beginners.
Back to Basics - Application Security Practices in Smart Contract Auditing
Explore application security practices in smart contract auditing, focusing on Solidity, common vulnerabilities, security tools, and the growing market for blockchain security engineers.
Identifying & Avoiding Android App Protections - Tim Strazzere, LevelUp 2017
Techniques for quickly identifying and bypassing Android app protections to improve bug bounty hunting efficiency and ROI.
MarkDoom- How I Hacked Every Major IDE in 2 Weeks - Matt Austin, LevelUp 2017
Explore web hacking techniques used to exploit major IDEs and desktop applications, revealing high-severity vulnerabilities in popular development tools.

Car Hacking 101 - Alan Mond, LevelUp
Explore car hacking essentials: hardware, software, and penetration testing techniques for automotive systems. Learn about attack surfaces, OBD2 ports, and network basics.
How Does Unicode Affect Our Security?
In-depth exploration of how encoding schemes can lead to IT implementation flaws and security vulnerabilities, with a focus on Unicode's impact on system security.
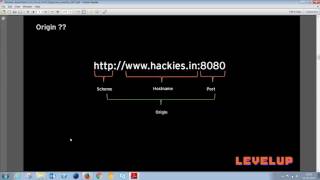
Browser Exploitation for Fun and Profit - Dhiraj Mishra, Bugcrowd's LevelUp 2017
Explore browser vulnerabilities, their root causes, and exploitation techniques. Learn about interesting security flaws discovered during research and gain insights into browser exploitation.
Advanced Android Bug Bounty Skills - Ben Actis, Bugcrowd's LevelUp 2017
Explore advanced Android bug bounty techniques, focusing on IPC vulnerabilities, mobile-specific issues, and leveraging web hacking skills for mobile security testing.
Do You Like Fuzzing? - Abhijeth, Bugcrowd's LevelUp
Explore REST API fuzzing with Fuzzapi, an automated tool for detecting vulnerabilities in web/mobile applications and improving API security.
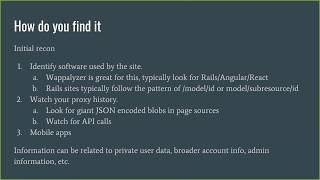
Hidden in Plain Site - Disclosing Information via Your APIs - Peter Yaworski, Bugcrowd's LevelUp 2017
Explore information disclosure vulnerabilities in APIs and HTML sources, focusing on Rails design patterns and front-end frameworks. Learn detection techniques and real-world examples.
Reverse Engineering iOS Mobile Apps
Introduction to iOS mobile app reverse engineering, covering specific tools and techniques. Includes demonstration on a popular app and advanced usage examples.
Breaking Mobile App Protection Mechanisms - Ben Actis, Bugcrowd's LevelUp
Learn to identify and bypass mobile app protections like obfuscation, root detection, and certificate pinning. Discover techniques to reduce "hardened" apps to basic security levels.
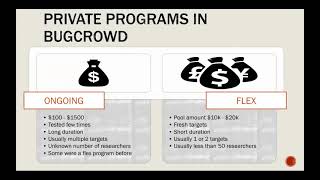
Finding Hidden Gems in Old Bug Bounty Programs - Yappare, Bugcrowd's LevelUp 2017
Discover strategies for uncovering valuable bugs in established bug bounty programs, focusing on unique approaches and methodologies to maximize success in competitive environments.
How to Fail at Bug Bounty Hunting - Caleb Kinney, Bugcrowd's LevelUp 2017
Insights and tips for part-time bug bounty hunters: overcoming challenges, learning from failures, and staying motivated while balancing professional commitments.
Bug Bounty Hunting Methodology - Jason Haddix from Bugcrowd's LevelUp
Comprehensive web hacking methodology covering reconnaissance, scanning, and exploitation techniques for bug bounty hunters and security researchers.
Esoteric Sub-Domain Enumeration Techniques
Explore advanced and unconventional sub-domain enumeration methods, their effectiveness, associated tools, and mitigation strategies for enhanced cybersecurity practices.
The State of Bug Bounties and Future Trends - Casey Ellis AMA
Insights on bug bounty industry trends, future prospects, and expert Q&A with Bugcrowd's CEO Casey Ellis, covering various aspects of cybersecurity and ethical hacking.
Writing Vulnerability Reports That Maximize Your Bounty Payouts
Learn to craft effective vulnerability reports that boost bounty payouts. Discover key strategies for communicating impact, providing proof of concept, and avoiding common mistakes in bug bounty submissions.
H@cktivitycon 2020 - Graphing Out Internal Networks with CVE-2020-13379 - Unauthed Grafana SSRF
Discover and exploit a critical SSRF vulnerability in Grafana, impacting thousands of companies. Learn methodology, see a live demo, and explore reporting and mass-exploitation experiences.
A Starters Guide to Pentesting with OWASP
Learn essential web security concepts, OWASP Top 10 vulnerabilities, and practical pentesting techniques to enhance your cybersecurity skills and protect web applications effectively.
Pentesting vs Bug Bounty - Approaches and Methodologies
Explore the differences between bug bounty hunting and penetration testing methodologies, comparing approaches, impacts, and scoping techniques.