Cyber Awareness and Resiliency
Explore cyber awareness and resilience concepts, including situational awareness, attack trends, NIST frameworks, and federal guidelines for enhanced cybersecurity posture in the digital age.
Cyber Security Incidents: Red Team vs Blue Team Tactics
Learn about Red Team/Blue Team cybersecurity exercises, incident response tactics, and best practices for defending against and simulating attacks. Gain insights from real-world scenarios and NIST framework implementation.
Four Types of Threat Detection in Industrial Security
Explore four threat detection types for industrial security, their derivation, and applications. Learn to identify optimal methods for your organization's ICS and IIoT environments.
Cyber Resiliency in the Power Industry - Strategies and Perspectives
Explore power industry cyber resiliency strategies, challenges, and implementation across IT/OT systems. Learn to incorporate resilience into security programs for better threat preparedness and response.
Starting Your Journey: A Roadmap for ICS/OT Cybersecurity
Explore ICS/OT cybersecurity essentials, from risk identification to program building. Learn strategies to protect critical infrastructure and align your organization's cybersecurity efforts for enhanced safety and reliability.
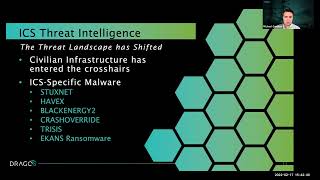
How to Operationalize ICS Threat Intelligence for Defenders
Discover strategies to leverage ICS threat intelligence for enhanced cybersecurity in industrial environments. Learn practical use cases and implementation techniques for effective defense against evolving threats.
NIST Cybersecurity Framework v2.0 Explained
Explore NIST Cybersecurity Framework v2.0 updates, including the new "Govern" function, and learn how to prepare your organization for enhanced cybersecurity management and leadership.
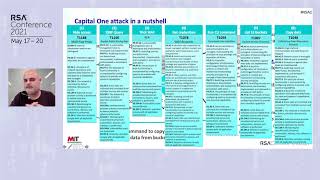
A Case Study of the Capital One Data Breach
Explore the 2019 Capital One data breach, examining attack methods, compliance issues, and corporate culture's impact on cybersecurity posture.
A Wake-Up Call - Information Security for Non-Profits, Foundations, and Charities
Exploring cybersecurity challenges for non-profits, this talk offers strategies to protect organizations, donors, and beneficiaries in the digital age, emphasizing unique sector needs and practical solutions.
Blue Teamin on a Budget of Zero - Kyle Bubp
Learn essential blue team security practices and tools for organizations with limited budgets, covering frameworks, documentation, network mapping, vulnerability scanning, and intrusion detection.
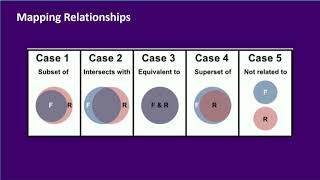
NIST Cybersecurity Framework and PCI DSS
Explore the mapping between NIST Cybersecurity Framework and PCI DSS, understanding similarities, relationships, and benefits for compliance across multiple standards.

Ten Tenets of CISO Success
Discover 10 key strategies for CISO success, including providing business value, gaining stakeholder buy-in, and driving organizational change. Learn to balance technical, operational, and strategic leadership roles.
The Case for a National Cybersecurity Safety Board
Explores the need for a National Cybersecurity Safety Board to investigate and prevent cyber attacks, drawing parallels with the NTSB and addressing critical infrastructure vulnerabilities.
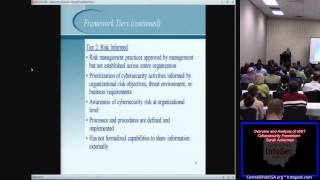
Overview and Analysis of NIST Cybersecurity Framework
Comprehensive analysis of the NIST Cybersecurity Framework, exploring its key components, implementation strategies, and practical applications for enhancing organizational security posture.

Data-Centric Zero Trust Architecture with the NIST Cybersecurity Framework
Master data-centric zero trust architecture using NIST Cybersecurity Framework guidelines, featuring RackTop's BrickStor SP solution for comprehensive data protection and risk management.
NIST Cybersecurity Framework v2.0 - What’s Changing
Explore key updates, community feedback process, and timeline for NIST Cybersecurity Framework 2.0. Learn about expected revisions and NIST's plans for wider adoption in the US and globally.
The Cybersecurity Framework at 10 and Beyond - NIST's Evolution and Impact
Explore the evolution and impact of NIST's Cybersecurity Framework, its global adoption, and upcoming Version 2.0 release with industry experts and NIST leaders.