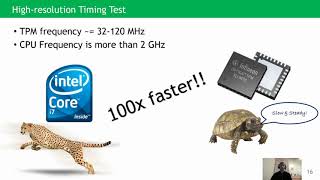
TPM-FAIL - TPM Meetings Timing and Lattice Attacks
Explore TPM vulnerabilities, timing attacks, and lattice-based cryptanalysis. Learn about ECDSA nonce issues and their impact on digital signatures in trusted computing.
Securing TPM Secrets in the Datacenter
Explore TPM security in datacenters, covering UEFI Secure Boot, extended authorizations, and innovative solutions for managing and provisioning TPMs in enterprise environments.
A Simple Protocol for Remote Attestation of System Integrity
Explore a simplified remote attestation protocol for system integrity using TPM keys and IMA Digest Lists. Learn about innovative solutions for secure TLS handshakes and efficient integrity verification.
TPM: History, Updates, and Future Developments
Explore TPM's history, updates, and future developments with Intel's Jarkko Sakkinen. Learn the basic idea and sequence diagram of this crucial technology.
Intel TD Partitioning and vTPM on COCONUT-SVSM
Explore Intel TD Partitioning and vTPM implementation on COCONUT-SVSM, gaining insights into advanced virtualization security techniques.
Keylime: Securing Your Slice of the Cloud
Explore scalable cloud trust attestation with Keylime, leveraging TPM technology for secure identity bootstrapping and system integrity monitoring in untrusted remote infrastructures.
Making Remote Attestation Useful on Linux
Explore TPM remote attestation on Linux, its current limitations, and potential improvements for enhanced security and trust in boot processes.
Towards Measured Boot Out of the Box
Explore measured boot technology, its importance for system security, and innovative approaches to implement it effectively in Linux distributions, overcoming adoption challenges.
Systemd and TPMs: Updates on Disk Encryption, PCR Policy Management, and More
Explore systemd's latest TPM-related features, including disk encryption, PCR policy management, measurement APIs, and event logging.
What Is Needed to Build Trusted Infrastructures
Exploring evolving security models for trusted infrastructure, including tokenization, TPMs, cryptography, and containerization. Discusses open source approaches to modern cybersecurity challenges.
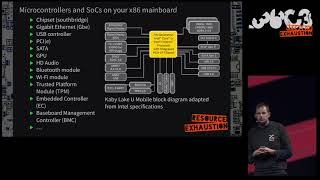
Look at ME! - Intel ME Investigation
Investigación detallada del Intel Management Engine, explorando su funcionamiento, implicaciones de seguridad y desafíos para desarrolladores y investigadores en el análisis de firmware propietario.
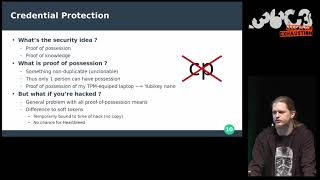
Hacking With a TPM
Explore TPM capabilities for securing credentials, encrypting storage, and detecting BIOS manipulations. Learn practical applications for everyday security using open-source software.
Getting Started with the TPM2 Software Stack - TSS2
Explore the TPM2 Software Stack: APIs, implementation, and community. Learn about recent developments, future directions, and practical applications in platform security.
Using TPMs to Cryptographically Verify Devices at Scale
Explore hardware-backed device security using TPMs, remote attestation, and open-source tools for maintaining trust in geographically diverse machine fleets.
Keylime - An Open Source TPM Project for Remote Trust
Explore Keylime, an open-source project for remote trust using TPM technology. Learn about its architecture, operations, and applications in securing hardware roots of trust and continuous remote attestation.
Parsec - A New Platform Abstraction for Security
Explore Parsec, an open-source platform for standardized security interfaces. Learn about its API, architecture, and integration with hardware-backed security features across platforms.
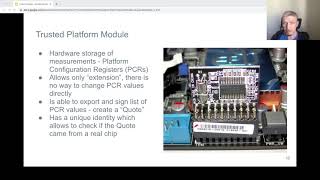
Protecting System Integrity with Trusted Platform Module
Explore system firmware vulnerabilities and learn how Trusted Platform Module (TPM) can safeguard against persistent implants, ensuring secure access to infrastructure secrets.
Remote Timing Attacks on TPMs - AKA TPM-Fail
Uncovers vulnerabilities in Trusted Platform Modules through timing analysis, revealing potential security risks in hardware-based cryptographic systems used across various computing platforms.

TPM Based Attestation - How Can We Use It for Good?
Explore TPM-based attestation for network security, SSH host key trust, and system recovery. Learn about TPM functionality, event logs, and open-source solutions for user protection without compromising privacy.
Kicking it up a Level - Bringing the Trusted Platform Module into QEMU
Explore virtualization of Trusted Platform Modules in qemu, enhancing security for cloud users through remote attestation and verification of untampered Trusted Computing Bases.
VMware Cloud Foundation's Approach to Platform Security - Making Complex Security Tasks Simple
Discover how VMware Cloud Foundation simplifies complex security tasks through features like ESXi Live Patch, Identity Federation, and automated audit tools while maintaining robust platform protection.