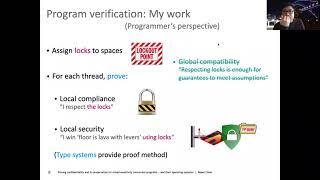
Proving Confidentiality and Its Preservation for Mixed-Sensitivity Concurrent Programs
Explore techniques for proving confidentiality in mixed-sensitivity concurrent programs and its preservation during compilation, using the Cross Domain Desktop Compositor as a case study. Discusses ongoing research on OS-level confidentiality assurance.
angr: Binary Analysis Framework - Demonstration and Analysis
Explore angr, a powerful binary analysis framework, through demos and source code analysis. Learn its capabilities for reverse engineering and vulnerability detection.
Mastering OSS Security Development with Linux Foundation Education
Develop secure open source software skills, from foundational to advanced, with expert-led training and certifications. Gain hands-on experience for real-world OSS security.
Verified Software Security Down to Gates
Explore hardware-software contracts synthesis, security vulnerability detection, and microarchitecture updates for verified software security. Gain insights into cutting-edge approaches for high-assurance computer systems design.
Using the Snyk CLI for Static Code Analysis
Learn to use Snyk CLI for static code analysis in CI/CD pipelines. Covers installation, testing, result filtering, and practical scenarios for integrating security scans into your development workflow.
How to Prepare for CSSLP Exam - CSSLP Exam Tips - Tips to Pass the CSSLP Exam
Expert guidance on CSSLP exam preparation, covering exam parameters, strategies, and key domains. Learn essential tips to excel in this prestigious application security certification.
Stranger Danger - Your Java Attack Surface Just Got Bigger
Explore Java application security in cloud-native environments through live hacking demonstrations. Learn about common threats, vulnerabilities, and misconfigurations, along with actionable remediation strategies and best practices.
Untangle the Secrets of Your JavaScript Dependencies
Explore NodeSecure, an open-source tool for analyzing JavaScript dependencies. Learn to visualize, understand, and secure your project's dependency tree with expert insights and practical demonstrations.
Making Open Source Secure by Design
Discover essential strategies for enhancing open source security with insights from CISA's Section Chief, covering design principles and implementation across critical infrastructure sectors.
Cómo Convencer a tu Jefe de Usar Rust
Descubre estrategias efectivas para persuadir a tu superior sobre los beneficios de implementar Rust en proyectos de desarrollo, mejorando la eficiencia y seguridad del código.
Responsible Disclosure of Security Issues - UbuConLA 2017
Aprende sobre la divulgación ética de vulnerabilidades de seguridad, explorando mejores prácticas y consideraciones importantes para reportar problemas de forma responsable.
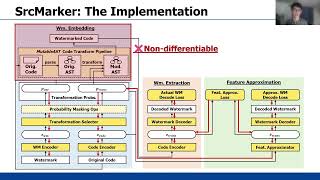
SrcMarker: Dual-Channel Source Code Watermarking via Scalable Code Transformations
Explore dual-channel source code watermarking techniques using scalable code transformations for enhanced software protection and ownership verification.
El código abierto como ventaja competitiva en tecnologías de Ciberseguridad
Explora cómo el software de código abierto fortalece la ciberseguridad, ofreciendo procesos y herramientas para gestionar dependencias, obtener información crítica y detectar violaciones de políticas.
Entendiendo y Confiando en tus Dependencias en Python
Análisis de dependencias en Python: riesgos ocultos, ataques como typosquatting y estrategias para evaluar y confiar en paquetes de terceros. Herramientas y prácticas para realizar controles de seguridad efectivos.
Log4JMX - The Vulnerability that Never Existed
Explore the intriguing case of Log4JMX, a supposed vulnerability that turned out to be non-existent, in this cybersecurity presentation at DefCamp Cluj-Napoca 2024.
Nix zu verstecken! Erstellung und Veröffentlichung von CVEs für Open Source Software
Erfahrungsbericht zur Erstellung und Veröffentlichung von CVEs für Open-Source-Software. Praktische Einblicke in den Prozess, Vorteile und Herausforderungen als CVE Numbering Authority.
DevSecOps Industry Lessons Learned and Future Steps with AI Integration
Gain insights into DevSecOps evolution, AI challenges, and practical steps for organizational maturity while exploring industry-proven lessons and future perspectives for effective implementation.
Securing Software by Construction: From Research to Industry - Philly ETE 2016
Explore techniques for building secure software from the ground up, bridging the gap between academic research and industry practice in cybersecurity, and addressing challenges in commercializing long-term security solutions.
Slow But Steady - Achieving Real Security Within Two Decades
Explore strategies for achieving real security in software systems over two decades, focusing on incremental improvements, formal verification, and well-engineered infrastructure.
Protecting the Stack with Metadata Policies and Tagged Hardware
Explore innovative metadata-tag based stack-protection security policies for tagged architectures, focusing on efficient cacheability and performance in unsafe languages like C.
RetroWrite- Statically Instrumenting COTS Binaries for Fuzzing and Sanitization
Explore static instrumentation of COTS binaries for enhanced fuzzing and sanitization using RetroWrite, a framework for rewriting position-independent code.