
Web App Testing - Enumeration
Learn web app enumeration techniques including subdomain discovery, vulnerability scanning, and using tools like Burp Suite and Nikto to identify potential security weaknesses.

Full Ethical Hacking Course - Beginner Network Penetration Testing
Comprehensive ethical hacking guide covering Linux, Python, OSINT, scanning, enumeration, exploitation, AD attacks, and more. Hands-on approach with practical tools and techniques for network penetration testing.
Zero to Hero Pentesting - Exploitation, Shells, and Some Credential Stuffing
Comprehensive tutorial on exploitation techniques, including reverse shells, credential stuffing, and live hacking demonstrations. Includes Q&A session covering various cybersecurity career topics and personal insights.
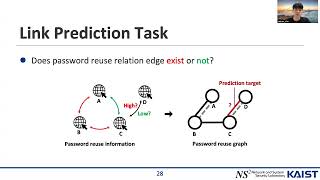
PassREfinder: Credential Stuffing Risk Prediction by Representing Password Reuse - 2024
Explore innovative techniques for predicting credential stuffing risks through password reuse analysis, enhancing cybersecurity measures and user protection.
La lucha contra el auge de la inteligencia artificial - BOT-Apocalypse Now
Estrategias para combatir ataques BOT en la era de la IA, enfocándose en amenazas móviles, reducción de costos WAF y protección contra fraudes, DDoS y abusos de API.

Much Ado About Credential Stuffing - CarolinaCon 2019 Preview
Explore credential stuffing attacks, their impact on cybersecurity, and effective prevention strategies. Learn from real-world examples and expert insights to enhance your digital defense skills.
Securing Third Party Applications at Scale - AppSecCali 2019
Learn best practices for securing third-party applications at scale, including tooling, processes, and manual reviews. Gain insights from Salesforce's experience in reviewing over 4000 AppExchange applications to prevent vulnerabilities.
Understanding the API Attack Vector - How Attackers Exploit Application Communications
Explore attacker techniques for targeting API-driven applications, including code manipulation, mobile vulnerabilities, and advanced attacks. Learn strategies to secure apps in cloud-native environments.
Automation Attacks at Scale - Detecting and Mitigating Distributed Threats
Explore automation attacks plaguing various industries, their detection methodologies, and real-world examples of distributed infrastructure used by attackers to launch and monetize these widely distributed, difficult-to-detect threats.
How to Thwart Malicious Automation and Kick Bot Butt for $0
Learn to defend against malicious bots and automated attacks using free, open-source solutions. Gain insights on threat profiling, defensive tactics, and implementation strategies for effective cybersecurity.
Cracking Active Directory Passwords and MFA Fatigue
Explore techniques for cracking Active Directory passwords and exploiting MFA fatigue vulnerabilities. Learn to strengthen organizational security through robust password policies and MFA implementation.
Tell Me Where You Live and I Will Tell Your Password
Explores factors influencing password quality across countries, revealing literacy levels and internet usage impact. Aims to understand macrosocial protection factors for adapting password lists.
A Cure for Botnets? Fighting Credential Stuffing at Adobe
Explore Adobe's innovative approach to combating credential stuffing attacks and botnets, presented by Senior Computer Scientist Sorin Portase at DefCamp 2022.
Blue Team Fundamentals
Explore effective strategies to counter common cyber attacks, including credential stuffing, phishing, and RCE attempts, with practical takeaways to enhance your organization's security posture.
The State of Credential Stuffing and the Future of Account Takeovers
Explore credential stuffing, account takeovers, and evolving cybersecurity threats. Learn about attack methods, defense strategies, and the future of online fraud prevention.
Top Active Directory Attacks - Understand, then Prevent and Detect
Explore common Active Directory attacks, prevention strategies, and detection methods. Learn to secure enterprise networks against prevalent hacking techniques and enhance cybersecurity practices.
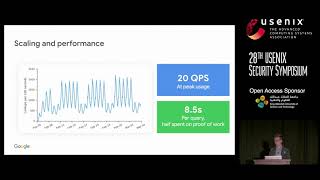
Protecting Accounts from Credential Stuffing with Password Breach Alerting
Explore a privacy-preserving protocol for detecting exposed credentials, its implementation as a cloud service, and its effectiveness in prompting users to update compromised passwords.
MFA, OTP, SMS, U2F, WTF - Multifaktor-Authentifizierung ist sehr gut
Erläutert verschiedene Multifaktor-Authentifizierungsmethoden, ihre Vor- und Nachteile sowie Schutz gegen gängige Angriffe. Demonstriert Technologien und diskutiert neue Konzepte wie Passkeys.
The Future of ATO
Exploring the evolving landscape of Account Takeover (ATO) attacks, focusing on emerging threats, sophisticated techniques, and strategies to protect user accounts in the digital age.
Fight Fraud and Bots with reCAPTCHA Enterprise
Discover advanced bot mitigation and fraud prevention techniques using Google's reCAPTCHA Enterprise, protecting against online attacks while ensuring seamless user interactions.

7 Common Cyber Attacks and How to Prevent Them
Explore seven major cyber attack methods and learn effective defense strategies for authentication systems, from credential stuffing to injection attacks and real-world prevention techniques.