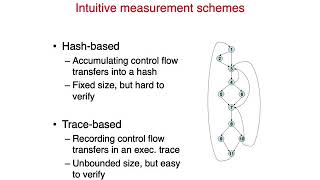
OAT - Attesting Operation Integrity of Embedded Devices
Innovative framework for attesting operation integrity of embedded devices, addressing control-flow hijacks and data-only attacks in IoT systems through lightweight measurement and verification techniques.
Overview and Recent Developments in TPM - Kernel Space Updates
Explore TPM subsystem updates, recent developments, and security measures against hardware attacks in Linux kernel space with Intel engineer Jarkko Sakkinen.
A Simple Protocol for Remote Attestation of System Integrity
Explore a simplified remote attestation protocol for system integrity using TPM keys and IMA Digest Lists. Learn about innovative solutions for secure TLS handshakes and efficient integrity verification.
Verifying the Validity of Crowd-Sourced Results in Open Source Security - The Scorecard GitHub Action and Sigstore
Explore how the Scorecard GitHub Action ensures security in open-source projects, using Sigstore for result integrity and remote attestation in crowd-sourced data validation.
Software Supply Chain Security with Trusted Execution Environment Provisioning Protocol
Explore TEEP protocol for secure software supply chain management, covering its benefits, implementation, and application across various hardware platforms and industries.
Lightweight Remote Attestation over EDHOC for Constrained IoT Devices
Explore efficient remote attestation for IoT devices using EDHOC protocol. Learn about parallel network authentication and integrity verification for constrained environments like RIOT OS.
Is Remote Attestation Relevant for Embedded Devices? - RIOT Summit 2024
Explore remote attestation's relevance for embedded devices, examining latest developments, challenges, and potential benefits in the context of Trusted Execution Environments and RIOT OS.
WASM and Confidential Computing - Securing FaaS Functions
Explore a zero-trust Serverless platform using Knative, WebAssembly, and Trusted Execution Environment to enhance security for sensitive cloud-based applications and data processing.
Zero Trust Architecture for Containers with Kata and Confidential Computing
Dive into advanced container security using Kata and Confidential Computing to implement zero-trust architecture, protect sensitive workloads, and achieve attestable pod integrity in Azure environments.
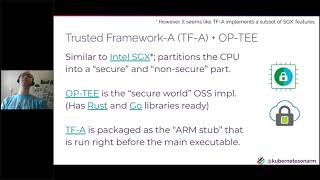
Exploring Modern and Secure Operations of Kubernetes Clusters on the Edge
Explore modern Kubernetes edge deployment security and operations, covering secure boot, OS image download, TPM for remote attestation, deployment options, GitOps management, and edge-cloud data synchronization.
IMA Namespaces for Container Security Enhancement
Enhancing container security with IMA namespaces, integrating with Kubernetes and remote attestation for detecting file changes within containers.
Making Remote Attestation Useful on Linux
Explore TPM remote attestation on Linux, its current limitations, and potential improvements for enhanced security and trust in boot processes.
Updating Linux with TUX: Trust Update for Linux Kernel
Explore TUX, a system for maintaining Linux kernel integrity during updates. Learn about secure boot, TPM, and remote attestation to enhance platform trust and mitigate security threats.
Device Mapper Target Measurements for Remote Attestation Using IMA
Explore remote attestation using IMA, focusing on Device Mapper Target Measurements. Learn about module attributes, see a demo, and discover future ideas in this technical presentation.
What's New in Systemd - DevConf.CZ 2023
Explore systemd's latest features beyond service management, including authenticated boot, disk encryption, and Unified Kernel Images support. Gain insights into current implementations and future possibilities.
Infoflow LSM
Explore Linux security models, integrity policies, and LSM framework implementation with a focus on multilevel security and policy enforcement techniques.
Using TPMs to Cryptographically Verify Devices at Scale
Explore hardware-backed device security using TPMs, remote attestation, and open-source tools for maintaining trust in geographically diverse machine fleets.
C-FLAT - Control-Flow Attestation for Embedded Systems Software
Control-flow attestation for embedded systems: detect runtime attacks, ensure software integrity. Novel approach combines remote attestation with control-flow monitoring for enhanced security in IoT devices.
Town Crier - An Authenticated Data Feed for Smart Contracts
Explore authenticated data feeds for smart contracts using Town Crier, leveraging Intel SGX for secure and confidential data delivery in decentralized environments.
Riverbed - Enforcing User-defined Privacy Constraints in Distributed Web Services
Riverbed: A framework for privacy-respecting web services, allowing users to define data processing constraints. Uses remote attestation and IFC to enforce policies without requiring code modifications.
The Remote Working Security Conundrum - What Is Reasonably Secure Anyway?
Explore challenges and solutions for securing remote work environments, from physical security to application layer, with focus on novel technologies and practical approaches.