
Ethical Hacking in 15 Hours - 2023 Edition - Learn to Hack
Comprehensive ethical hacking training covering advanced techniques like subdomain hunting, vulnerability scanning, exploitation, and buffer overflows. Includes hands-on practice with multiple virtual machines.
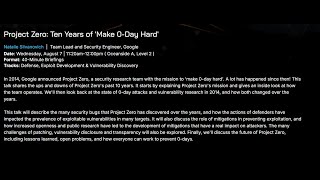
Project Zero: Ten Years of Making Zero-Day Exploits Hard
Explore Project Zero's decade-long mission to combat 0-day vulnerabilities, examining its impact on security research, bug discovery, and the evolving landscape of cyber threats.
Eko2020 Workshops - Antonio Morales Maldonado: Advanced Fuzzing Workshop
Taller práctico de técnicas avanzadas de fuzzing y búsqueda de vulnerabilidades con formato CTF. Orientado a profesionales con conocimientos previos para mejorar habilidades en seguridad informática.
A Journey Finding Pre and Post-Auth D-Link Router Zero-Days
Explora el proceso de descubrimiento y explotación de vulnerabilidades 0-day en routers D-Link, desde obtener acceso al firmware hasta identificar y explotar fallos de seguridad para lograr ejecución remota de código.
Introducción al Reversing - Ingeniería Inversa para Seguridad Informática
Introducción a la Ingeniería Inversa: fundamentos, aplicaciones en seguridad informática y herramientas esenciales. Ideal para principiantes interesados en exploits, análisis de malware y más.
RetroWrite- Statically Instrumenting COTS Binaries for Fuzzing and Sanitization
Explore static instrumentation of COTS binaries for enhanced fuzzing and sanitization using RetroWrite, a framework for rewriting position-independent code.
CacheOut - Leaking Data on Intel CPUs via Cache Evictions
Explore Intel CPU vulnerabilities, focusing on CacheOut attack, its mechanisms, potential targets, and countermeasures for enhanced system security.
Unleashing Mayhem on Binary Code
Explore automated exploit generation for binary programs using hybrid symbolic execution and index-based memory modeling. Learn techniques to find and demonstrate exploitable vulnerabilities efficiently.
LevelUp 0x04 - Introduction to Ethical Hacking and Bug Bounty - Day 1
Explore cutting-edge cybersecurity insights and strategies at this free conference, featuring expert talks and discussions on the latest industry trends and challenges.
iPhone Baseband Research and Reversing - Security Insights and Techniques
Explore iPhone baseband internals, research techniques, and tools for firmware analysis, reversing, and exploitation. Gain insights into Qualcomm baseband architecture and vulnerabilities.
8 Ways to Almost Never Get a Dupe Again in Bug Bounty Hunting
Discover strategies to minimize duplicate bug reports in bug bounty hunting, including developing expertise, exploring unique targets, and leveraging personal strengths.
Read The Bleeping RFC - Understanding Network Protocols for Security
Explore RFC vulnerabilities and their impact on web security with Inti De Ceukelaire. Learn to identify and exploit logic flaws in protocols for more effective bug hunting and penetration testing.
Bug Bounties, Pulse Secure Research, and Hacking the US Department of Defense - Interview with Alyssa Herrera
Insightful discussion on bug bounties, cybersecurity research, and ethical hacking experiences, featuring expert insights from Alyssa Herrera on various high-profile targets.
Back to the Core - Exploring Fundamental Security Concepts
Explore advanced techniques for analyzing and exploiting core system vulnerabilities in this in-depth security presentation from SyScan'15 Singapore.
Responsible Disclosure Preparedness for IoT Security - 2017
Exploring IOT security flaws in garage door systems, from discovery to responsible disclosure. Learn about research techniques and the process of addressing vulnerabilities in connected devices.
Bypassing EMET 4.1 - Exploiting Enhanced Mitigation Experience Toolkit
Learn techniques for bypassing Microsoft's Enhanced Mitigation Experience Toolkit (EMET) with expert insights on exploit development and security vulnerabilities.
Microsoft Vulnerability Research: How to Be a Finder as a Vendor - Notacon 11
Explore Microsoft's approach to vulnerability research, focusing on third-party findings, reporting processes, and lessons learned from case studies. Gain insights into effective vulnerability management.
Empirical Exploitation in Cybersecurity - HD Moore
Explore empirical exploitation techniques with HD Moore, delving into cutting-edge cybersecurity research and practical applications for identifying vulnerabilities.
MarkDoom: How I Hacked Every Major IDE in 2 Weeks
Explore how major IDEs were hacked through embedded browsers, revealing critical security vulnerabilities in desktop applications built with web technologies. Learn about the risks and safeguards in the "Desktop Web" era.
Malicious Use of Microsoft Local Administrator Password Solution
Exploiting vulnerabilities in Microsoft's LAPS to gain unauthorized access to local administrator credentials and maintain presence on compromised systems in post-exploitation scenarios.
NVMe: New Vulnerabilities Made Easy - Exploiting Cloud Storage Protocols
Exploring pre-auth remote vulnerabilities in NVMe implementation, emphasizing the importance of SCA tools in production pipelines and showcasing discoveries in Linux kernel and NVIDIA.