Splunk Fundamentals 1
Learn to navigate Splunk, create reports and dashboards using search commands and Pivot tool. Covers installation, data ingestion, configuration, lookups, alerts, and key commands.
Splunk SIEM Training Tutorials
Comprehensive tutorials on using Splunk for cybersecurity, covering incident response, threat hunting, and investigations across various attack scenarios and platforms.
Threat Detection and Active Response with Wazuh
Explore Wazuh SIEM for detecting and defending against cyber threats. Learn to collect, analyze, and respond to security events for effective blue team operations.
Splunk Security Event Monitoring - Blue Team Series with Hackersploit
Learn to set up and use Splunk for security event monitoring, including installation, configuration, log forwarding, data analysis, and dashboard customization in this comprehensive tutorial.
Splunk Machine Learning
Aprende a utilizar Splunk Machine Learning Toolkit para análisis de datos, detección de anomalías y predicciones con asistentes especializados y actualizaciones de versiones.
Grey's Academy
Live product demos and deep-dives on Splunk for beginners, intermediate users, and experts, covering topics like observability, OpenVino, and industrial data.
Splunk Admin
Comprehensive guide to Splunk administration, covering installation, configuration, scaling, clustering, and advanced features for efficient log management and analysis.
Advanced Threat Hunting With Splunk
Learn advanced threat hunting techniques using Splunk, covering installation, data analysis, search queries, and complex event analysis for enhanced cybersecurity operations.
Building on Microsoft Sentinel Platform
Explore Microsoft Sentinel's latest updates, learn to create codeless connectors, build solution guides, and contribute to the unified SIEM + XDR GitHub repository. Enhance your cloud-native SIEM capabilities for improved data analysis and threat detecti…

Microsoft Sentinel - Modern SIEM with SOAR, Threat Intelligence, and UEBA
Explore Microsoft Sentinel's advanced SIEM capabilities, including SOAR, threat intelligence, and UEBA. Learn about recent updates, integration with Azure Purview, and get tips for implementation and training.

Configure Your Microsoft Sentinel Environment
Configure Microsoft Sentinel for rapid cloud security insights. Learn about components, architecture, installation, and management to meet organizational security requirements.

Introduction to Splunk in Hindi
Comprehensive Hindi tutorial on Splunk basics, covering monitoring concepts, architecture, components, data flow, and installation. Ideal for beginners seeking practical insights into this powerful monitoring tool.
Introduction to Splunk in Hindi
Comprehensive Hindi tutorial on Splunk basics, covering monitoring concepts, architecture, components, data flow, and installation for beginners in software development and data analysis.
Using DevOps Practices to Implement a Full Route-to-Live for SIEM Platforms
Explore DevOps practices for implementing full route-to-live in SIEM platforms. Learn about threat detection, adaptive hunting, and version control for enhanced cybersecurity.
Cyber & Data: Introduction to Splunk
Learn to analyze data with Splunk, covering basics, file analysis, web access logs, and visualizations for effective cybersecurity and data insights.
Cyber & Data - Introduction to Splunk and Machine Learning
Explore Splunk and machine learning techniques for data analysis, including anomaly detection, prediction, clustering, feature extraction, and preprocessing methods.
What's New in SIEM and XDR - Attack Disruption and SOC Empowerment
Explore Microsoft's latest SIEM and XDR innovations for enhanced threat prevention, detection, and response. Learn how integrated tools and cloud-based intelligence can disrupt attacks and empower defenders.
SIEM and XDR: Automating Threat Detection and Response
Explore Microsoft's integrated SIEM+XDR solution for advanced threat detection and automated response, designed to protect environments end-to-end and stay ahead of sophisticated adversaries.
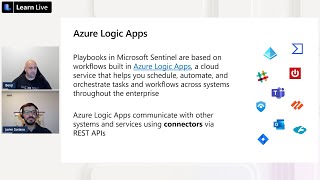
Threat Response with Microsoft Sentinel Playbooks - Learn Live
Explore Microsoft Sentinel's SOAR capabilities and create automated playbooks for efficient security threat response. Hands-on session with live expert guidance and audience interaction.
Threat Models for Exercising SIEM and Incident Response
Explore effective threat modeling techniques to enhance SIEM and incident response capabilities, improving overall cybersecurity preparedness and resilience.
Understanding IBM QRadar - Key Components of IBM QRadar
Comprehensive overview of IBM QRadar's key components, functionality, and importance in cybersecurity. Covers threat detection, incident response, and platform capabilities for effective security intelligence.