Bug Bounty Methodology
Learn comprehensive bug bounty techniques, from reconnaissance to vulnerability discovery, with practical tips for successful ethical hacking and reporting security flaws in web applications.
Back to Basics - Application Security Practices in Smart Contract Auditing
Explore application security practices in smart contract auditing, focusing on Solidity, common vulnerabilities, security tools, and the growing market for blockchain security engineers.
Critical Security Issues and Trends for 2017
Explore critical security trends with industry experts, covering IoT vulnerabilities, crowdsourced testing, AI impacts, and evolving threats to prepare for the cybersecurity landscape of 2017.
Purple Team Strategies for Application Security
Explore purple team strategies for application security, blending red and blue team approaches to enhance vulnerability testing, automation, and security infrastructure integration.
How to Effectively Test Transient Execution Mitigations
Explore transient execution vulnerability testing methods, challenges, and future improvements for effective mitigation in software and hardware systems.
Hackazon: Stop Hacking Like It's 1999
Explore Hackazon, a modern vulnerable web app for testing security skills. Learn about its AJAX interface, RESTful APIs, and configurable vulnerabilities that challenge both automated scanners and manual pentesters.
OWASP Broken Web Applications - Future Developments Beyond Version 1.0
Explore OWASP's virtual machine with 25+ vulnerable web applications for security training and testing. Learn about project features and future developments in web application security.
Security Does Not Need to Be Fun - Ignoring OWASP to Have a Terrible Time
Explore OWASP's free tools and resources for designing and implementing secure web applications, addressing common security challenges in the software development lifecycle.
Azure Vulnerability Testbed (AzGOAT) - Understanding and Hardening Azure Security
Explore Azure security vulnerabilities and defenses with AzGOAT, a lab environment for understanding attack surfaces, designing secure solutions, and minimizing threats in Azure environments.
Hunting for Amazon Cognito Security Misconfigurations
Explore Amazon Cognito security misconfigurations, learn testing techniques for audits and bug bounty hunting, and discover mitigation strategies through a real-world account takeover case study.
Vulnerability Testing, a Case Study
Explore vulnerability testing through a real-world case study, gaining insights into effective security assessment techniques and practical application of testing methodologies.
Compression Bombs Strike Back
Explore data compression risks, HTTP vulnerabilities, and server attack techniques in this comprehensive security analysis of compression-related threats.
Implementing an USB Host Driver Fuzzer
Explore USB host driver fuzzing techniques, covering USB basics, security implications, and practical implementation steps for effective vulnerability discovery.
Beyond OWASP Top 10 by Aaron Hnatiw - Hack in Paris - 2017
Explore 5 dangerous web vulnerabilities beyond OWASP Top 10, covering exploits and mitigations for both developers and pentesters to enhance application security.
FIESTA - An HTTPS Side-Channel Party
Explore HTTPS side-channel vulnerabilities and a new tool, FIESTA, for testing and exploiting these issues. Learn about a novel side-channel affecting major tech companies and its implications for online security.
OWASP IoTGoat Project Overview and Roadmap
Explore IoTGoat, an OWASP project for IoT security testing. Learn about hardware compatibility, vulnerabilities, and hands-on techniques like firmware extraction and password cracking.
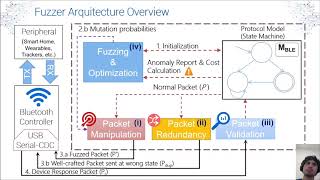
SweynTooth - Unleashing Mayhem over Bluetooth Low Energy
Explores vulnerabilities in Bluetooth Low Energy protocol implementations, presenting a systematic fuzzing framework that discovered 11 new vulnerabilities across various devices and IoT products.
IOT RCE - A Study With Disney
Explore IoT device vulnerabilities using Disney's Circle and Foscam as case studies. Learn novel attack techniques, including SSL bypasses, SSID injection, and cloud routing abuse. Discuss IoT devices' use of offensive tools.
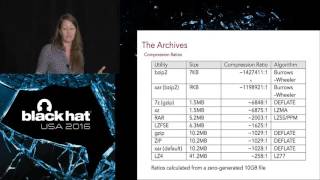
Auditing the Compression Algorithm Weapon Cache
Explore decompression bomb attacks, their impact on applications, and strategies for prevention. Learn about various compression algorithms and their vulnerabilities in this security-focused presentation.
Defeating Machine Learning - Systemic Deficiencies for Detecting Malware
Explore systemic vulnerabilities in machine learning for malware detection, covering sandbox evasion, model problems, and potential solutions for improved cybersecurity.
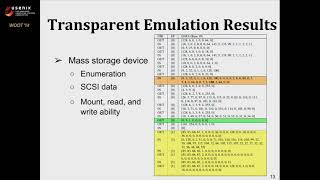
Lowering the USB Fuzzing Barrier by Transparent Two-Way Emulation
Innovative USB testing framework enabling cost-effective, flexible analysis and modification of USB communication. Introduces two-way emulation for enhanced fuzzing and vulnerability detection.