Intrusion Detection with Wazuh - Blue Team Series with Hackersploit
Comprehensive guide to Wazuh for intrusion detection, covering setup, configuration, and key features like agent management, integrity monitoring, and vulnerability assessment for enhanced cybersecurity.
Threat Detection and Active Response with Wazuh
Explore Wazuh SIEM for detecting and defending against cyber threats. Learn to collect, analyze, and respond to security events for effective blue team operations.
Intrusion Detection With Snort
Learn to use custom and community Snort rules for effective intrusion detection. Discover how to capture network traffic, identify malicious activity, and set up logging and notifications for enhanced security.
Intrusion Detection with Suricata - Blue Team Series with Hackersploit
Learn to install, configure, and use Suricata for intrusion detection. Covers IDS, IPS, network security monitoring, custom rules, log analysis, and integration with Wazuh for enhanced Blue Team cybersecurity.
Monitor in Real-Time with OSSEC - See What’s Taking Place in Your Server
Learn to implement OSSEC for real-time server monitoring, including installation, configuration, and practical demonstrations on both Linux and Windows systems. Gain hands-on experience in intrusion detection and log analysis.
Security Instrumentation - The Future of Software Security
Explore security instrumentation as a revolutionary approach to enhance software security, offering dynamic capabilities like intrusion detection, SBOM reporting, and runtime protection without code changes.
StreamAlert: A Serverless Real-time Intrusion Detection Engine
Discover StreamAlert: a serverless, real-time intrusion detection engine that scales effortlessly, allowing security teams to focus on catching attackers with simple and complex rules for any log type.
HoneyPy and HoneyDB: Leveraging Honeypots for Network Security - 2016
Explore honeypots, HoneyPy, and HoneyDB for network security. Learn about low-interaction honeypots, threat detection, and leveraging honeypot data to enhance organizational cybersecurity defenses.
Runtime Analysis of Whole-System Provenance
Explore real-time provenance-based auditing techniques for enhanced system security, overcoming limitations of post-hoc analysis in forensic investigations.
AI and Cybersecurity - The Twain Shall Meet
Explore AI's role in cybersecurity, focusing on advanced persistent threats, intrusion detection systems, and vulnerability analysis using ontologies and reasoning techniques.
Network Attack Traffic and Data Mining - Lab 6
Explore network attack traffic and data mining techniques, including statistics, Nmap, Hydra, and crosscorrelation analysis for enhanced cybersecurity understanding.
Digital Investigator - Intrusion Detection Examples
Explore real-world intrusion detection scenarios, from P2P communications to various scanning techniques, enhancing your digital investigation skills.

A Fire in the Eye: Advanced Network Traffic Analysis Techniques
Explore innovative network traffic detection techniques, focusing on the "Fire in the Eye" project. Learn about challenges, methodologies, and limitations in network security analysis.
Ambush - Catching Intruders at Any Point
Learn advanced techniques for detecting and intercepting network intruders using the Ambush system, enhancing your cybersecurity skills and defensive capabilities.
Ambush - Catching Intruders at Any Point
Learn techniques for detecting and intercepting intruders in network systems, focusing on proactive security measures and advanced monitoring strategies.
4140 Ways Your Alarm System Can Fail
Explore vulnerabilities in alarm systems and learn how they can be compromised, with insights from security experts on improving protection against potential failures.
Enhancing Physical Perimeter Defense Using Software-Defined Radio
Explore innovative physical perimeter defense using software-defined radio to detect potential threats by simulating cell tower signals, enabling early reconnaissance identification and post-breach investigation.
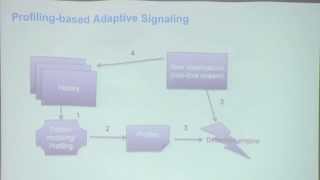
Devil in the Haystack - Application Security Through Statistical Analysis and Machine Learning
Exploring statistical and machine learning techniques for in-app security at Salesforce. Focuses on adaptive, data-driven approaches for detecting and preventing attacks and abuses on the platform.
Attack-Driven Defense: Countering Real-World Attack Behaviors
Explore new network defense techniques from an attacker's perspective, focusing on detecting initial compromise, persistence, and lateral movement. Learn practical methods for effective alerting and traffic analysis.

Security Onion 2 Release Announcement and Live Demo
Discover the latest features and improvements in Security Onion 2 through an in-depth release announcement and live demonstration, showcasing advanced capabilities for network security monitoring and threat detection.
Building a Minimal Security Onion VM with sosetup-minimal
Learn to set up a minimal Security Onion virtual machine with dual NICs, focusing on Evaluation Mode installation and basic configuration for network security monitoring.