Ekoparty Summer Workshops 2021 - Infraestructura Ofensiva para Red Teams y Pentesters
Aprende a desplegar infraestructura ofensiva automatizada y anónima usando herramientas DevOps como Kubernetes y Ansible para ataques de red team y pentesting.
Detecting Sandbox Evasion Techniques in Malware Analysis
Explore malware sandbox evasion techniques and learn how to detect them using the MITRE ATT&CK Framework. Discover innovative approaches to improve analysis systems and stay ahead of cyber threats.
The MITRE ATT&CK Framework: Understanding and Applying Adversarial Tactics - 2018
Explore the Mitre ATT&CK Framework to understand adversary tactics, detect threats, and improve cybersecurity defenses. Learn to map technologies, identify gaps, and enhance prevention strategies across various security roles.
Real-World Implications of the MITRE ATT&CK Framework for IT and OT Environments
Explore MITRE ATT&CK framework's real-world applications in IT and OT environments. Learn to leverage this knowledge base to enhance defensive measures, improve incident response time, and streamline SOC workflows.
MITRE ATT&CK Evaluations for Industrial Control Systems - Dragos Retrospective
Comprehensive analysis of MITRE Engenuity ATT&CK® Evaluations for ICS, covering attack simulation, threat detection, and industrial cybersecurity vendor performance across a 5-day simulated attack scenario.
MITRE ATT&CK for Industrial Control Systems - Demonstration and Analysis
Explore ICS cybersecurity with MITRE ATT&CK framework, featuring a technical demo of an ICS cyber attack from attacker and defender perspectives using Dragos Platform.
Automated Cloud-Native Incident Response with Kubernetes and Service Mesh
Explore automated incident response in cloud-native environments using Kubernetes and service mesh. Learn best practices, tools, and techniques for effective security management and threat mitigation.
MITRE ATT&CK Framework for Offensive and Defensive Operations
Comprehensive exploration of MITRE ATT&CK framework for cybersecurity professionals, covering implementation in offensive and defensive operations to enhance threat intelligence and security strategies.
Red Team Adversary Emulation With Caldera
Explore automated Red Team adversary emulation using MITRE Caldera, a framework built on ATT&CK for simulating attacks and testing organizational security defenses.
Introduction to the MITRE ATT&CK Framework
Comprehensive overview of MITRE ATT&CK framework for cybersecurity professionals, covering its application in red team and blue team operations with practical insights and resources.
Mapping Motives: Analysis of 2,000 Enterprise Cloud Detections - Strengthening Multi-Cloud SOC
Analysis of 2,000 cloud detections reveals enterprise control patterns, gaps, and attacker motives. Learn to strengthen multi-cloud security operations with actionable insights and MITRE ATT&CK framework application.
Kubernetes Risk Assessment - Going One Level Deeper
Explore Kubernetes security risks, dynamic components, and assessment methodologies using MITRE ATT&CK framework to enhance cluster protection and mitigate vulnerabilities.
Don't Boil the Ocean - Using MITRE ATT&CK to Guide Hunting Activity
Learn to use MITRE ATT&CK framework for focused threat hunting, avoiding overwhelming approaches. Discover how to build hypotheses, plan hunts, and operationalize findings for more effective cybersecurity practices.
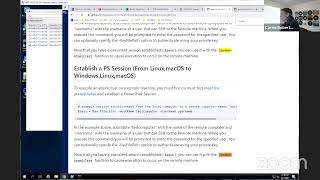
Atomic Red Team Hands-on Getting Started Guide
Hands-on guide for implementing Atomic Red Team, covering setup, execution, and best practices for effective cybersecurity testing and threat emulation.
Does Your SOC Suck?
Panel discussion on optimizing Security Operations Centers (SOCs), covering best practices, challenges, and innovative approaches to enhance cybersecurity monitoring and response capabilities.
Shall We Play a Game?
Develop effective security exercises using MITRE ATT&CK framework. Learn to create, run, and score drills that turn threat intelligence into practiced action for improved incident response.
Making Sense of Unstructured Threat Data
Explore how Natural Language Processing and Word2Vec can organize unstructured cybersecurity intelligence, making it actionable by mapping to frameworks like MITRE ATT&CK.
Automated Adversary Emulation Using Caldera
Explore automated adversary emulation with MITRE Caldera 2.0, focusing on extending its capabilities, improving reporting, and overcoming security controls for enhanced ATT&CK coverage and adoption.
DeTT&CT - Mapping Your Blue Team to MITRE ATT&CK
Explore MITRE ATT&CK framework for blue team mapping, focusing on attack techniques, gap analysis, and event query language to enhance cybersecurity defenses.
ATT&CKing the Status Quo - Improving Threat Intel and Cyber Defense with MITRE ATT&CK
Explore MITRE ATT&CK framework to enhance threat intelligence and cyber defense strategies. Learn implementation tips, detection techniques, and industry examples for improved security posture.
Conceptos de OT para Blue Teamers - Santiago Abastante & Matias Manassero - Ekoparty 2021: BlueSpace
Exploración de conceptos de Tecnología Operativa para equipos de defensa cibernética, abordando arquitecturas, ataques, detección de intrusiones y estrategias de inteligencia de amenazas en entornos industriales.