Security Operations Center SOC Interview Preparation
Prepare for SOC interviews with expert insights on security, risk, threat detection, and profile building. Gain practical knowledge to excel in cybersecurity roles and boost your career prospects.
Unleashing AI-Powered Threat Detection and Response in the SOC
Explore AI-powered threat detection in SOCs, focusing on cloud and hybrid environments. Learn real-world applications and future implications for cybersecurity operations.
AI-Powered Security Operation Center - Myth or Reality
Explore the potential of AI-powered Security Operation Centers (SOCs) in cybersecurity. Gain insights from Vladimir Ghita's DefCamp 2023 presentation on the reality and myths surrounding this innovative approach.
AI for Cybersecurity - Overview of the Field and Promising Future Directions
Explore AI applications in cybersecurity, including threat intelligence and adversarial machine learning. Learn about data sources, limitations, and future directions in this field.
How to Create a One-Man Security Operations Center (SOC)
Learn to establish and operate a one-person Security Operations Center (SOC) with practical tips on workflow creation, tool selection, automation, and incident response strategies.
Operationalizing Threat Intelligence in Industrial Control Systems
Operationalizing threat intelligence in ICS: Learn to consume, digest, and apply intelligence to enhance cybersecurity decisions and improve operations in industrial control systems.
Tomorrow's SOC - Risk Management and Overcoming the IT/OT Divide
Explore the future of industrial SOCs with Splunk and Dragos integration, focusing on OT asset visibility, threat detection, and vulnerability management to bridge the IT/OT divide and enhance risk mitigation.
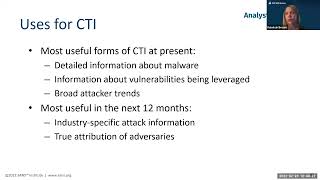
SANS 2022 Cyber Threat Intelligence Survey - Key Findings and Adaptations
Explore shifts in cyber threat intelligence due to workplace changes, its role in ransomware response, and preparation for unpredictable events with severe consequences.
Containerizing Your Security Operations Center
Explore containerizing security operations for improved deployment, maintenance, and collaboration. Learn to build a cloud-based SOC using containers, enhancing visibility and streamlining security workflows.

SOAR, SOC, and Scholars - Developing Security Operations at UofSC
Explore UofSC's innovative approach to security operations, integrating SOAR technology, SOC management, and student involvement for comprehensive cybersecurity development.

Increasing Your Situational Awareness with SOC Dashboards
Enhance security operations with SOC dashboards for improved situational awareness. Learn effective techniques to monitor and respond to threats in real-time.

Essential Elements of Next-Generation SOC and Intelligence-Driven Cybersecurity Strategies - Part 2
Explore best practices for building a comprehensive cybersecurity strategy, focusing on next-generation SOC, threat intelligence utilization, and employee-centric IT programs to enhance organizational security.
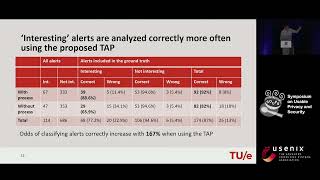
Synthesis and Evaluation of a Network Threat Analysis Process for Tier 1 SOC Investigations
Evaluation of a structured 4-stage threat analysis process for SOC tier-1 analysts, showing improved accuracy and discussing implications for security operations.
Connecting CTI and SOC Teams - MISP42
Explore strategies for bridging the gap between Cyber Threat Intelligence and Security Operations Center teams, enhancing collaboration and threat response capabilities.
Unified SOC - Centralized Security Data with OT Visibility for Intelligence-Driven Investigations
Experts discuss unifying Security Operations Centers by integrating OT cybersecurity, threat intelligence, and advanced technologies for comprehensive visibility and efficient investigations in industrial environments.
The Always-On Purple Team: Automated CI/CD for Detection Engineering
Innovative architecture for automated detection engineering CI/CD pipeline, merging SOC technologies, SIEM/XDR, SOAR, BAS, and ChatGPT. Includes live demo of creating, testing, and deploying detection analytics.
Detection Engineering without Alert Fatigue - Correlating Minor Detections
Explore innovative approaches to balance detection coverage and alert fatigue in SOC operations, leveraging custom platforms and indicator correlation for effective threat hunting and investigation assistance.
Microsoft Sentinel - A Modern Approach to Security Operations
Explore Microsoft Sentinel's AI-powered security operations, featuring live demonstrations of SOC optimization, threat investigation, and advanced response capabilities for modern cybersecurity challenges.
Improving Collaboration and Reducing Risk in Security Operations - Part 2
Explore strategies for enhancing IT-business collaboration and risk management in organizations of all sizes, with insights from security leaders on SOC challenges and solutions.
Decoding Security Operations - A Complete SOC 101 Crash Course
Master Security Operations Center essentials: monitoring, threat detection, incident response. Gain insights to enhance organizational security posture and understand key SOC roles in modern cybersecurity.
War Stories from the SOC - Cybersecurity Incident Response Lessons
Cybersecurity expert shares real-world experiences from Security Operations Center, offering insights into threat detection, incident response, and best practices for defending against cyber attacks.