Intelligence-Driven Security: Enhancing Cyber Defense Strategies - Session 12
Explore intelligence-driven security strategies to combat cyber threats, enhance detection capabilities, and improve incident response efficiency in today's evolving threat landscape.
Confronting the Chinese Cyber Threat - 2018 Aspen Cyber Summit
Explore China's cyber tactics, their impact on U.S. interests, and strategies to address this geopolitical challenge in a discussion with leading cybersecurity experts.
That Was Then - US-China Relations and Asian Security Challenges
Exploring US-China relations, North Korea threats, South China Sea tensions, and cyber espionage. Experts discuss implications of shifting diplomatic dynamics and potential resolutions to key geopolitical challenges.
Bad Company - Nation-States and Organized Crime in Cybersecurity
Explore the evolving landscape of cybercrime, its intersection with nation-states, and the challenges in attribution and response, featuring insights from FBI, DoD, and cybersecurity experts.
A Moment of Reckoning - Understanding the Russian Cyber Attack
Explore the severe 2020 Russian cyber infiltration of US federal agencies and corporations, examining cybersecurity failures, potential risks, and necessary actions moving forward.
Ongoing EvilEye Campaigns Targeting CCP Adversaries
Explore ongoing EvilEye campaigns targeting CCP adversaries, analyzing tactics, targets, and implications for cybersecurity professionals and policymakers.
A Tale of Lazarus and His Family - Hack.lu 2023
Explore the pervasive influence of Lazarus and related threat actors in cybersecurity, uncovering their tactics, techniques, and global impact on digital landscapes.
Wars and Rumors of Wars - Implications for Domestic Critical Infrastructure
Explore the implications of Volt Typhoon's cyber attacks on critical infrastructure and discuss appropriate responses for organizations and individuals facing such threats.
Operation Triangulation: Uncovering a Sophisticated Zero-Click Attack on iPhones
Unveiling a sophisticated zero-click iOS attack chain: discovery, analysis, and implications of Operation Triangulation, a highly advanced spyware targeting researchers' iPhones.
The Sednit Group, Cyber Espionage in Eastern Europe
Explore the Sednit group's cyber espionage tools, recent campaigns, and exploitation techniques targeting Eastern Europe, with a focus on Ukraine-related topics and custom exploit-kits.
The KGB Hack - 30 Years Later
Rückblick auf den KGB-Hack der 1980er Jahre: Dramatischer Vorfall des Hackings, der das öffentliche Bild des CCC prägte. Analyse der Aufdeckung, Folgen und anhaltenden Auswirkungen auf die Wahrnehmung von Hackern.
Stop! Don’t Make That Noob Incident Handling Mistake
Aprenda a evitar erros comuns na resposta a incidentes de segurança cibernética, com foco em preservação de evidências, análise de dados e estratégias eficazes de contenção.
Through the Eyes of the Adversary - How to Build a Threat Intel Program
Learn to build an effective threat intelligence program by understanding adversary perspectives, focusing on key components and serving organizational stakeholders.
Attribution in a World of Cyber Espionage
Explore cyber espionage tactics, security innovations, and false flag operations in the digital realm. Learn about Yarra Engine and its implications for industrial cybersecurity.
Dark Caracal Part II - Where in the World is Caracal?
Uncover Dark Caracal's infrastructure, identities, and operational base. Explore the implications for nation-state malware and future cyber campaigns.
Darkhotel - Lighting the Room
Explore the intriguing Darkhotel cyber espionage campaign, its methods, and its impact on high-profile targets in luxury hotels across Asia.
Activities of the Tick Cyber Espionage Group Over the Last 10 Years
Comprehensive analysis of the Tick cyber espionage group's decade-long activities, focusing on their tactics, malware, and impact on East Asian targets, particularly in Korea and Japan.
The Trails of WINDSHIFT APT
Explore WINDSHIFT APT's unique cyber espionage tactics, including advanced spear phishing, macOS malware, and surveillance techniques. Learn about their focus on specific individuals and hard-to-attribute methods.
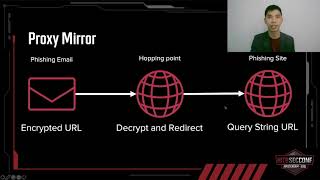
Dissecting Phishing Techniques of CloudDragon APT
Análisis detallado de las sofisticadas técnicas de phishing del grupo APT norcoreano CloudDragon, incluyendo casos reales, métodos para evadir la autenticación de dos factores y propagación a sistemas Android.
Practical Attacks Against MDM Solutions
Explore novel proof-of-concept attack techniques on Android and iOS devices that bypass traditional mobile malware detection and circumvent common Mobile Device Management features.
Blink - The Network Perimeter is Gone
Explores the expanding threat landscape of wireless and mobile devices, highlighting vulnerabilities in IoT and BYOD policies. Demonstrates new attack vectors and proposes updated defense strategies.