
JavaScript for Hackers
Learn JavaScript essentials for ethical hacking with experts @STOKfredrik and @TomNomNomDotCom. Covers Chrome Dev Tools, DOM XSS, debugging, and impact assessment.
Attack Surface Reduction Strategies for Enhanced Security
Explore attack surface reduction strategies with Google Project Zero's Natalie Silvanovich, focusing on innovative techniques to enhance system security and minimize vulnerabilities.
Security@ 2017 - Understanding Hacker Motives
Explore hacker motivations and experiences in bug bounty programs through insights from top hackers and industry experts. Learn about challenges, rewards, and the evolving security landscape.
Security at Government Agencies - Hacking the US Government
Experts discuss hacking US government systems, vulnerability disclosure programs, and cybersecurity challenges in federal agencies. Insights on bug bounties, tech surges, and public-facing systems.
Security and Hacking - Lessons from the MySpace Worm
Explore hacking insights from Samy Kamkar, renowned for the MySpace worm, as he shares his expertise and experiences in cybersecurity at the Security@ Conference.
Breaking the Bank - Security Panel for Financial Services
Experts discuss cybersecurity challenges and strategies in financial services, exploring innovative approaches to protect digital assets and customer data in an evolving threat landscape.
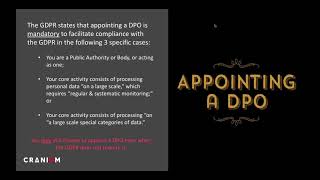
Everything You Need to Know About the Data Protection Officer Role
Explore the Data Protection Officer role, its GDPR requirements, responsibilities, and importance. Learn about qualifications, comparisons with other roles, and practical implementation strategies.
Coordinated Vulnerability Disclosure Guide - AMA with CERT Authors
Insights on coordinated vulnerability disclosure from CERT Guide authors, covering principles, process improvement, and common challenges in cybersecurity reporting and management.
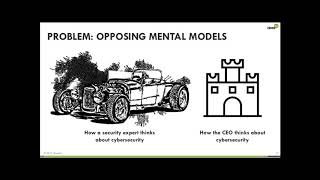
Overcoming Executive Biases in Cybersecurity Investment
Strategies to overcome executive biases and secure more investment in cybersecurity, including new success metrics and industry comparisons.
Some Applications of Contextual Integrity
Explore applications of contextual integrity in data privacy, examining its foundations and real-world implications for protecting personal information.
Stepping-Up - The Census Bureau Sets an Example of How to Be a Good Data Steward in the 21st Century
Explore how the U.S. Census Bureau exemplifies effective data stewardship in the modern era, balancing privacy concerns with the need for accessible public information.
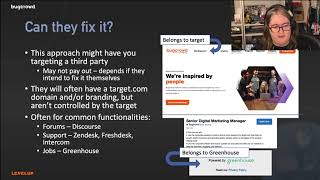
8 Ways to Almost Never Get a Dupe Again in Bug Bounty Hunting
Discover strategies to minimize duplicate bug reports in bug bounty hunting, including developing expertise, exploring unique targets, and leveraging personal strengths.
Hunting IDOR with Z-winK - Part 2
Dive deeper into hunting Insecure Direct Object Reference (IDOR) vulnerabilities for significant rewards. Learn advanced techniques and strategies from expert Z-winK in this follow-up presentation.
How I Hacked 55 Banks and Cryptocurrency Exchanges - LevelUpX Series 3
Alissa Knight reveals tactics used to breach 55 financial institutions, offering insights into vulnerabilities in FinTech apps and APIs. Learn from a veteran hacker's experience in cybersecurity.
Log4Shell Vulnerability - Bugcrowd Security Flash
Explore the critical Log4Shell vulnerability, its impact, and mitigation strategies in this concise security briefing from Bugcrowd's expert.
It's Not a Vulnerability, It's a Feature - Exploiting Built-in Functionality
Explore how offensive security has evolved from CVEs to TTPs, and learn to leverage built-in features for security testing and potential monetization through creating and sharing TTPs.

How to Crush Bug Bounties in the First 12 Months
Comprehensive roadmap for new bug bounty hunters: boost knowledge, improve workflow, and achieve success in the first year. Tips for seasoned hackers included.
Hardware Hacking for the Masses - Version 2
Explore hardware hacking basics, areas, and entry points with hands-on demos. Learn essential concepts and discover resources for further practice in this engaging introduction to breaking and understanding hardware.
Car Hacking Explained for Bug Hunters - Automotive Security Vulnerabilities and Methodologies
Explore automotive security vulnerabilities, from IoT to CAN bus hacking. Learn methodologies, attack surfaces, and bug prioritization for car hacking, covering infotainment systems, APIs, and mobile apps.
Sticking With It: How to Choose a Target and Stay Motivated in Bug Bounty Programs
Learn strategies for selecting bug bounty targets, maintaining motivation during hacking, and deciding when to persist or move on. Gain insights from an experienced researcher on navigating the challenges of bug hunting.
Hackers Don't Wear Black Hoodies, They Wear Capes - Ethical Hacker Rights and Trust
Explore ethical hacking rights, challenges, and the importance of trust in infosec. Learn why community collaboration is crucial for encouraging ethical hacking and protecting vulnerabilities.