Adversary Emulation with Caldera - Red Team Series
Comprehensive guide on using Caldera for adversary emulation in red team operations, covering MITRE ATT&CK framework, configuration, agent deployment, and creating adversary profiles for cybersecurity testing.
Attack-Driven Defense: Countering Real-World Attack Behaviors
Explore new network defense techniques from an attacker's perspective, focusing on detecting initial compromise, persistence, and lateral movement. Learn practical methods for effective alerting and traffic analysis.
Becoming a Dark Knight - Adversary Emulation Demonstration for ATT&CK Evaluations
Explore adversary emulation techniques using real-world APT scenarios to improve cybersecurity defenses and industry standards through MITRE ATT&CK Evaluations.
Scarlet OT: Adversary Emulation for Industrial Control Systems - HITB 2023
Explore Scarlet OT, an open-source tool for ICS security testing. Learn about OT adversary emulation, protocol support, and real-world applications in industrial environments.
Red Team Adversary Emulation With Caldera
Explore automated Red Team adversary emulation using MITRE Caldera, a framework built on ATT&CK for simulating attacks and testing organizational security defenses.
Scarlet OT - Adversary Emulation for Operational Technology
Herramienta de emulación de adversarios OT de código abierto que combina ataques IT y OT, reproduce acciones de malware ICS y soporta múltiples protocolos para pruebas de seguridad industrial eficientes.
Introduction to Software Defined Radio for Offensive and Defensive Operations
Overview of Software Defined Radio for security professionals, covering basics to advanced tactics for adversary emulation. Learn quick SDR operations and explore offensive and defensive applications.
Red Team Frameworks and Methodologies
Explore industry-standard frameworks and methodologies for planning and executing successful Red Team operations, enhancing your cybersecurity skills and knowledge.
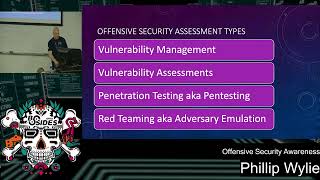
Offensive Security Awareness: Understanding Assessment Types and Methodologies
Demystify offensive security techniques, tools, and assessment types. Gain insights into vulnerability management strategies and learn to choose the right approach for your organization's security needs.
Synergizing Threat-Informed Defense
Explore threat-informed defense strategies for cloud environments, covering defensive measures, cyber threat intelligence, and testing methodologies to enhance cybersecurity effectiveness.
Purple Teaming and Adversary Emulation in the Cloud with Stratus Red Team
Explore cloud-native adversary emulation with Stratus Red Team. Learn to identify and reproduce malicious activities in AWS and Kubernetes, enhancing threat detection capabilities for cloud environments.
Cloud Native Application Threat Modeling and Adversary Emulation - Techniques and Tools
Explore threat modeling and adversary emulation techniques for cloud-native applications, including methodologies, tools, and strategies to identify and mitigate security risks in dynamic cloud environments.
Cloud Native Application Threat Modeling and Adversary Emulation
Explore cloud native application security through threat modeling and adversary emulation techniques, enhancing your ability to identify and mitigate potential vulnerabilities.
Don't Boil the Ocean - Using MITRE ATT&CK to Guide Hunting Activity
Learn to use MITRE ATT&CK framework for focused threat hunting, avoiding overwhelming approaches. Discover how to build hypotheses, plan hunts, and operationalize findings for more effective cybersecurity practices.
Atomic Red Team Hands-on Getting Started Guide
Hands-on guide for implementing Atomic Red Team, covering setup, execution, and best practices for effective cybersecurity testing and threat emulation.
Adversary Emulation on Windows - DefCamp - 2021
Explore advanced adversary emulation techniques for Windows systems, focusing on penetration testing, red teaming, and the MITRE framework to enhance cybersecurity defenses.
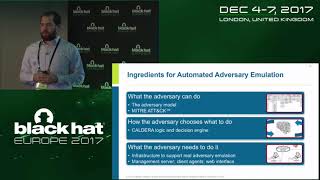
CALDERA - Automating Adversary Emulation
Automate adversary emulation for network security using CALDERA. Replicate realistic post-compromise techniques, leveraging benign system functionality to enhance defensive strategies.
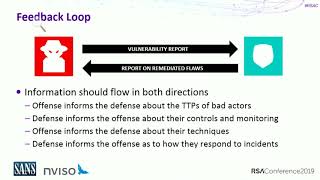
Live Adversary Simulation - Red and Blue Team Tactics
Explore live adversary simulation techniques, enhancing communication between red and blue teams for effective cybersecurity. Learn to perform threat simulations, map APT phases, and implement purple teaming strategies.
Test or Be Tested - Adversary Emulation with Atomic Red Team
Explore adversary emulation using Atomic Red Team to validate EDR tools. Learn about the project's growth, framework, and workflow for creating and contributing tests for ATT&CK techniques.
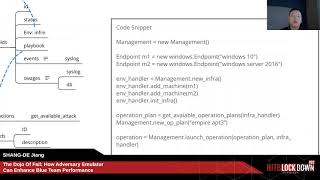
How Adversary Emulation Can Enhance Blue Team Performance
Explore adversary emulation to enhance blue team performance, addressing cybersecurity expert shortages and evolving attack methods. Learn to design attack playbooks and test security products effectively.
Hands-On Purple Team Exercises
Hands-on workshop on purple team exercises, combining red and blue team roles. Practice adversary emulation, threat detection, and defense improvement in a simulated environment.