Security Audits for Machine Learning Attacks
Explore common machine learning security attacks and learn effective remediation strategies to protect your models from harmful outcomes and data exposure. Enhance your organization's security practices.
Key Takeaways from Instructure's Bug Bounty Program
Discover insights from Instructure's Bug Bounty program, including their innovative approach to security audits, crowdsourced penetration testing, and key lessons learned for enhancing cybersecurity practices.
Information Security Third-Party Assessments - The Big Joke
Explore third-party security assessments in InfoSec, uncovering common pitfalls and best practices for effective evaluation and risk management in this insightful Bsides Chicago presentation.
Rust-VMM: A Security Journey
Explore rust-vmm's security journey, covering components, audits, development practices, and fuzzing techniques for virtualization and Virtio components.
Developing Secure Open Source Software - Mentorship Session
Explore best practices for developing secure open source software with expert guidance on risk mitigation, vulnerability management, and collaborative security measures.
Managing Audits for Critical Open Source Projects
Learn how OSTIF manages security audits for critical open source projects, connecting experts with maintainers to improve overall security posture and patch vulnerabilities.
Presenting the OSTIF Independent Security Audit Impact Report
Explore OSTIF's 2022 security improvements to critical open source projects, funded by OpenSSF. Learn about the initiative's background and key outcomes.
Improving Posture of Critical OSS Projects with Security Audits
Explore effective security audits for open source projects, including top vulnerabilities, lessons learned, and common mistakes to avoid. Enhance your OSS security posture.
Security Posture Assessment and Improvements for Open Source Projects
Explore essential security practices for open source projects, including fuzzing, SBOM, and SSDLC. Learn to assess vulnerabilities and maintain robust security postures through real-world examples.
Unlocking Startup Success: The Vitality of Security Assessments and How to Master Them
Discover essential security assessment strategies for startups. Learn to establish robust security controls, navigate audits, and build a strong security posture to protect innovative ideas and ensure market success.
Security TAG Closing - Highlights and Future Work
Wrap-up of Cloud Native Security Con, highlighting Security TAG's work, future plans, and ways to get involved. Covers whitepapers, assessments, audits, and ecosystem insights.
A Look Under the Hood of CNCF Security Audits
Insights into CNCF security audits: process, expectations, outcomes, and common vulnerabilities. Explores experiences from auditing six major projects and the value of audit reports for contributors and researchers.
Root Canal Static Analysis Audit of Zephyr
Comprehensive static analysis audit of Zephyr's code quality, revealing deeper security vulnerabilities beyond standard linters. Insights on advanced bug detection and fixing processes for critical open-source projects.
SIG Security Update: We Lift Together - Improving Kubernetes Security
Explore Kubernetes security updates, community-building approaches, and collaborative efforts in improving project and user security. Learn about tooling, audits, and documentation initiatives.
Exploring Hacker Operating Systems - Ubuntu
Explore Ubuntu as a hacking OS: learn to harden the system, install hacking tools, and understand Linux forks. Gain insights on Ubuntu's advantages and practical installation in virtual environments.
Kubernetes Security Response Committee: Introduction and Deep Dive
Explore the Kubernetes Security Response Committee's role, vulnerability lifecycle, and key findings from the 2022 security audit. Learn about reporting processes and community impact.
KubeEdge: From Fixed Location to Movable Edge - Latest Updates and Future
Explore KubeEdge's latest advancements in edge computing, including new industry adoptions, scalability improvements, and community updates. Learn about its expanding capabilities and future roadmap.
Kubernetes SIG Security Update - Security Through Transparency
Explore Kubernetes SIG Security's efforts in documentation, tooling, and third-party audits to enhance transparency and security. Learn about ongoing projects and opportunities for involvement.
Let's Chat About SOC 2s, Baby
Comprehensive overview of SOC 2 audits, covering types, principles, criteria, and implementation strategies. Explores the audit process, scope, and reporting, offering insights for organizations seeking compliance.
Swiss Cybervoting Pitfalls
Análisis crítico del sistema de voto electrónico suizo, sus desafíos técnicos y no técnicos, y las controversias surgidas durante las pruebas de intrusión pública desde la perspectiva de un investigador de seguridad.
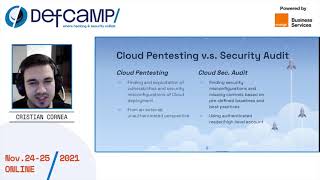
Offensive and Defensive Sides of Cloud Security - DefCamp - 2021
Explore offensive and defensive cloud security strategies, including risks, audits, penetration testing, and real-world attack scenarios in this comprehensive DefCamp presentation.