Red Team 101 - Introduction to Red Team Exercises
Aprende sobre ejercicios de Red Team: actividades, frameworks y caso práctico en vivo. Descubre cómo los atacantes operan, evaden y persisten en sistemas comprometidos.
Decentralized C2 Using LogDrop - Exploiting Web Server Misconfigurations
Descubre LogDrop, una técnica innovadora para establecer canales de comando y control aprovechando errores de configuración en servidores web. Aprende sobre ciberseguridad y nuevas estrategias de Red Team.
Bypassing Endpoint Controls Using Office Macros - Techniques and Defenses
Explore techniques for bypassing endpoint controls using Office macros, including crafting malicious documents, establishing C&C channels, and evading detection through advanced attack methods.

CommandGPT: Using ChatGPT for C2 and Post-Exploitation - Lecture 13
Explore CommandGPT's potential in offensive security, leveraging AI for dynamic code generation in command and control frameworks and simulating ransomware techniques.
ClickOnce Exploitation: One-Click Network Foothold - AppSec California 2016
Explore ClickOnce deployment vulnerabilities and learn a new methodology for establishing network footholds through minimal user interaction and phishing techniques.
DIY Command and Control for Fun and No Profit
Hands-on exploration of Command & Control botnets, providing insight into cybercriminal operations. Includes live malware demonstration for a realistic glimpse into this dark corner of the internet.
Improving Cyber Resilience Through Micro Attack Simulations
Innovative Micro Attack Simulations approach for validating specific security controls, enhancing cyber resilience through targeted assessments of technical and non-technical aspects, demonstrated with a ransomware attack case study.
Very Unusual Case of C2 Over DNS from Certain Firewalls
Explore an unusual case of C2 over DNS from specific firewalls, presented by Piotr Głaska at DefCamp Cluj-Napoca 2024. Gain insights into this unique cybersecurity scenario and its implications.
Rolling out the C2 - Modern Red Team Infrastructure in 2024
Explore modern red team infrastructure setup using Azure Cloud, Tailscale VPN, GitLab, and containerization. Learn to deploy secure C2 systems for effective penetration testing and security assessments.
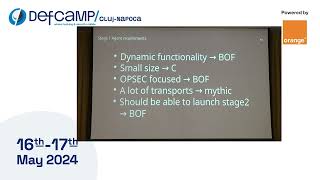
Stage 1 C2 in 3 Days - DefCamp Cluj-Napoca 2024
Explore rapid C2 infrastructure setup for penetration testing in this DefCamp presentation. Learn efficient techniques for Stage 1 Command and Control deployment within tight timeframes.
Windows Agentless C2 - Abusing the MDM Client Stack
Unveils innovative research on exploiting Windows MDM stack for agentless C2 systems. Explores vulnerabilities, custom C2 server creation, and remote device control techniques, inspiring new defensive strategies.
The Art of Compromising Command and Control Servers - A Web Application Vulnerabilities Perspective
Dive into techniques for exploiting command and control server vulnerabilities, uncovering infrastructure weaknesses, and exposing threat actors through common web application security flaws.
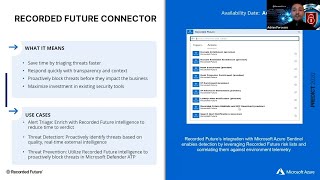
Leverage Recorded Future Playbooks to Automatically Integrate Threat Intelligence with Microsoft Azure
Automate threat intelligence integration in Microsoft Azure using Recorded Future Playbooks for enhanced detection, enrichment, and prevention in Sentinel and Defender ATP.
Abusing Cloud Apps 101 - Command and Control
Explore techniques for exploiting cloud applications as command and control infrastructure, focusing on security vulnerabilities and defensive strategies.
Reinvestigating PowerShell Attacks
Explore the evolution of PowerShell attacks, offensive techniques, and defensive strategies since 2014, including insights on Desired State Configuration for covert persistence and command and control.
So You Think You Can Secure Your Cloud - Red Team Engagements in GCP
Comprehensive guide to adversary simulations in GCP, covering initial access, persistence, privilege escalation, C2 using Google products, and data exfiltration techniques.
Circumventing the Guardians - How the Security Features in State-of-the-Art TLS Inspection Solutions Can Be Exploited for Covert Data Exfiltration
Unveiling a stealthy data exfiltration method that bypasses TLS inspection security solutions. Learn about SNIcat and how it circumvents perimeter defenses, with insights on mitigation and detection strategies.
DSCompromised - A Windows DSC Attack Framework
Explore a PowerShell toolkit leveraging Windows Desired State Configuration for command-and-control, malware persistence, and automatic re-infection. Learn attack techniques and defensive strategies.
Game of Chromes - Owning the Web with Zombie Chrome Extensions
Explore how malicious Chrome extensions can create botnets, distribute themselves, and exploit vulnerabilities. Learn about attack patterns, extension capabilities, and security measures.
Honey I Stole Your C2 Server - A Dive into Attacker Infrastructure
Explore attacker infrastructure through a Mandiant investigation, covering Metasploit indicators, command and control, encoding, and insights into attacker techniques and tools.
Weaponizing Splunk - Using Blue Teams for Evil
Explore how attackers can exploit Splunk for malicious purposes, including data extraction and command control, in this eye-opening cybersecurity presentation.