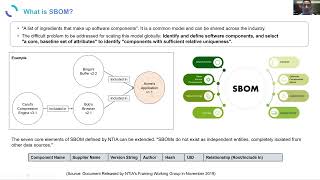
From SBOM to Trusted Software Supply Chain - How Far Are We?
Explore advancements in software supply chain security, from SBOM to vulnerability management and attack prevention, with insights on future directions and emerging technologies.
Where Is the GUAC? - Understanding Artifact Composition in Software Supply Chains
Explore GUAC: a tool for comprehensive software supply chain analysis, integrating metadata to identify vulnerabilities, assess trust, and enhance security through GraphQL-powered insights.
How Do You Know You're Done After a Security Fix - Leveraging SBOM Data
Explore approaches for leveraging SBOM data to improve automation and confidence in safety analysis after applying vulnerability fixes in systems with safety considerations.
Software Bill of Materials (SBOM) in Kubernetes - Best Practices and Approaches
Explore SBOM implementation in Kubernetes, comparing approaches and best practices. Learn how Paketo Buildpacks embeds SBOMs in application images using Syft, enhancing software supply chain security.
SBOM is Coming - Why You Should Care and How You Can Help
Explore the importance of Software Bill of Materials (SBOM) in cloud-native ecosystems, its impact on security, and how you can contribute to its implementation and adoption.
SBOM: The Rest of the Story - Understanding Software Bill of Materials
Experts discuss Software Bill of Materials (SBOM), addressing misconceptions, sharing challenges, and exploring implementation strategies for enhanced software supply chain security.
Leveraging SBOMs to Automate Packaging, Transfer, and Reporting of Dependencies Between Secure Environments
Explore innovative uses of Software Bill of Materials (SBOMs) for secure asset transfer, dependency management, and cloud-native infrastructure deployments using CycloneDX and open-source tools.
Bringing Service Security to a New Level - An Introduction to SaaSBOMs
Explore SaaSBOMs: enhancing service transparency, addressing complexities in generation, and discussing future developments for improved software supply chain security and legal compliance.
Hyades - Dependency Track for Enterprise Supply Chain Security with SBOM
Enhance enterprise supply chain security using Dependency Track with SBOM in Hyades, a powerful tool for managing software dependencies.
Practical SBOM Management with Zephyr and SPDX
Learn to identify, assess, and manage software components in Zephyr applications using SBOM standards and tools. Enhance security practices and respond effectively to vulnerabilities in embedded systems.
Manage Open Source, Security and SBOMs for Software Projects and Organizations
Learn to effectively manage open source, enhance security, and implement SBOMs for software projects and organizations.
Infusing Security Into the Application Development Process
Explore integrating security into software development, covering topics like SBOMs, vulnerability scanning, and supply chain security. Learn practical strategies for secure coding practices.
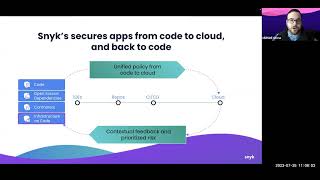
Integrations 101
Comprehensive guide to Snyk integrations, covering IDE setup, CLI usage, Git onboarding, Jira integration, and reporting. Ideal for new users and administrators seeking to enhance security in their development pipeline.
DBOM and SBOM - New Options for Better Supply Chain Cybersecurity
Explore new approaches to supply chain cybersecurity using Digital and Software Bill of Materials. Learn how these tools can enhance risk management and component traceability in complex global supply chains.
How Software Transparency Can Help Save the World
Explore software transparency through SBOMs, enhancing vulnerability management and supply chain visibility. Learn how this approach can revolutionize cybersecurity and software development practices.
Transparency in the Software Supply Chain - Making SBOM a Reality
Explore the concept of Software Bill of Materials (SBOM) and its potential to enhance transparency in the software supply chain, discussing benefits, challenges, and implementation strategies.
How I Learned to Stop Worrying and Love the SBOM
Explore the potential of Software Bill of Materials (SBOM) to revolutionize information security, addressing industry resistance and highlighting its benefits for transparency and enterprise value.
SBOM - Screw It, We'll Do It Live!
Exploring Software Bill of Materials (SBOM) concept, its potential impact on software supply chain transparency, and its crucial role in enhancing healthcare sector security. Insights on implementation and overcoming reluctance.
A Radiography of a SBOM Vulnerability Scanner
Explore Software Bill of Materials (SBOM) for enhanced cybersecurity. Learn about SBOM tools, formats, and integration in DevSecOps pipelines. Practical examples using Syft, Grype, and bomber for vulnerability scanning.
Scaling Software Supply Chain Source Security in Large Enterprises
Explore strategies for securing diverse software supply chains in large enterprises, including open-source, vendor, SaaS, and hardware. Learn to operationalize SBOMs for enhanced security and risk management.
SBOM is Here - Making Progress - Not Excuses
Explore the progress and implementation of Software Bill of Materials (SBOM) in cybersecurity, discussing challenges, opportunities, and practical strategies for effective adoption and utilization.