Burp Suite - Basic Concepts for Web Pentesting
Learn essential web pentesting techniques using Burp Suite, covering parameter passing, code injection, XSS, LFI/RFI attacks, and SQL injection for effective security testing of web applications.
Security at Government Agencies - Hacking the US Government
Experts discuss hacking US government systems, vulnerability disclosure programs, and cybersecurity challenges in federal agencies. Insights on bug bounties, tech surges, and public-facing systems.
Attack Surface and Security Implications of eSIM Technology
Explore the security vulnerabilities and potential risks associated with eSIM technology in mobile phones and desktop devices, raising awareness about offensive operations and post-compromise scenarios.
Embedded Threats: A Deep Dive into the Attack Surface and Security Implications of eSIM Technology
Explore the attack surface and security implications of eSIM technology through a comprehensive deep dive into embedded threats.
Comparing Risks: Why Asset Management Is Broken and How to Fix It
Explore innovative approaches to asset management in cybersecurity, focusing on risk comparison, vulnerability prioritization, and effective remediation strategies for improved security outcomes.
Cloud Native Application Threat Modeling and Adversary Emulation - Techniques and Tools
Explore threat modeling and adversary emulation techniques for cloud-native applications, including methodologies, tools, and strategies to identify and mitigate security risks in dynamic cloud environments.
Three Surprising Kubernetes Networking Features and How to Defend Against Them
Explore surprising Kubernetes networking vulnerabilities and learn effective defense strategies to protect your clusters from potential attacks and compromises.
Day in the Life of a Base Image - The Evolution of Vulnerabilities in Popular Containers
Explore the evolution of vulnerabilities in popular container images, understand security challenges, and learn practical steps to manage and prevent issues in your development process.
What We Learned Dissecting the World's Most Popular Containers
Explore insights from analyzing popular containers, covering size, complexity, package landscape, and security vulnerabilities to enhance container management and optimization strategies.
OWASP IoT Top 10 - Understanding Security Issues in Internet of Things
Explore key security vulnerabilities in IoT technologies and learn strategies to build, deploy, and assess IoT systems more securely with insights from the OWASP Internet of Things Project.
Subverting Your Server Through Its BMC - The HPE iLO4 Case
Exploración profunda de la seguridad de HP iLO4, incluyendo análisis del firmware, vulnerabilidades y una nueva técnica de explotación para comprometer el sistema operativo del servidor host a través de DMA.
Old New Things - An Examination of the Philips TriMedia Architecture
Explore the Philips TriMedia architecture, examining its history, features, and potential vulnerabilities through firmware analysis and hardware exploration.
Simplifying Threat Modeling
Simplified approach to threat modeling: identify attack surfaces, visualize users as threats, illuminate assets and trust boundaries, postulate attacks, evaluate impact, and mitigate risks.
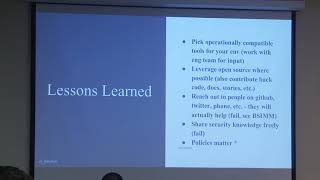
Building an AppSec Program from the Ground Up - An Honest Retrospective
Learn from a 2-year journey building an AppSec program, covering successes, failures, goal-setting, and execution. Gain insights on static analysis, threat modeling, metrics, and more for effective security implementation.
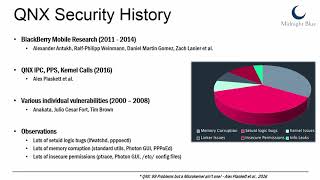
Analyzing & Breaking QNX Exploit Mitigations and PRNGs for Embedded Systems
Dissection of QNX's security features, including exploit mitigations and random number generators, for embedded systems in automotive, industrial, defense, and medical sectors.
Rawr - Rapid Assessment of Web Resources
Explore rapid web resource assessment techniques, including crawling, scanning, and fuzzing, to enhance cybersecurity and identify potential vulnerabilities in web applications.
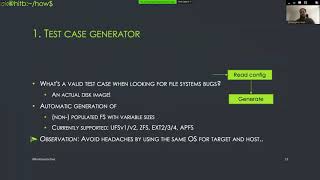
Fuzzing File System Implementations to Uncover Security Bugs
Explore file system vulnerability research through fuzzing techniques on BSD systems. Learn to identify attack surfaces, automate testing, and uncover security bugs in kernel implementations.
Subverting Sysmon - Application of a Formalized Security Product Evasion Methodology
Explore methodologies for subverting Sysmon, a security monitoring tool, through data collector strategies and configuration analysis to enhance adversarial techniques against enterprise defenses.
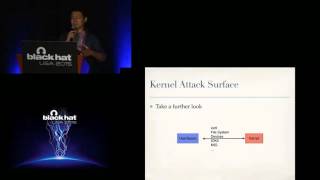
Review and Exploit Neglected Attack Surfaces in iOS 8
Explores overlooked iOS 8 vulnerabilities through fuzzing and code auditing, revealing system daemon crashes and memory corruption errors triggerable via XPC, plus an iOS kernel 0day.
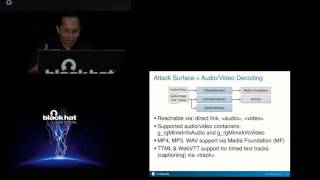
Understanding the Attack Surface and Attack Resilience of Project Spartan's New EdgeHTML Rendering Engine
Explore EdgeHTML's attack surface, compare it with MSHTML, and analyze exploit mitigations in Windows 10's new rendering engine for enhanced web security understanding.
DOG of WAR - Attack Box Design
Explore attack box design strategies and techniques for penetration testing and security assessments in this comprehensive presentation by Scott Blake.