
Microsoft Sentinel - Modern SIEM with SOAR, Threat Intelligence, and UEBA
Explore Microsoft Sentinel's advanced SIEM capabilities, including SOAR, threat intelligence, and UEBA. Learn about recent updates, integration with Azure Purview, and get tips for implementation and training.
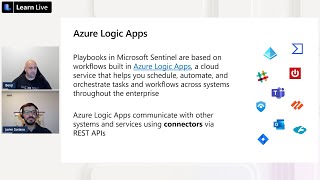
Threat Response with Microsoft Sentinel Playbooks - Learn Live
Explore Microsoft Sentinel's SOAR capabilities and create automated playbooks for efficient security threat response. Hands-on session with live expert guidance and audience interaction.
Automated Incident Response - Streamlining Processes and Enhancing Efficiency
Explore innovative Slack-based tools for streamlining incident response processes, reducing overhead, and enhancing efficiency through automation and integration with critical cloud-based systems.
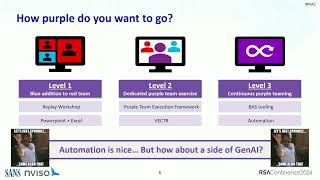
The Always-On Purple Team: Automated CI/CD for Detection Engineering
Innovative architecture for automated detection engineering CI/CD pipeline, merging SOC technologies, SIEM/XDR, SOAR, BAS, and ChatGPT. Includes live demo of creating, testing, and deploying detection analytics.
SOAR with Postee - Automated Incident Response for Cloud Native Risks
Automate incident response for cloud-native risks using Postee, enhancing security operations and streamlining threat management in modern infrastructures.
Automated Security Incident Response with Swimlane - Building Effective Response Systems
Discover how to build automated security response systems that reduce breach impact, minimize human error, and combat team fatigue in round-the-clock security operations management.

Black Hat Europe 2023
Black Hat Europe 2023

Black Hat Asia 2025
Black Hat Asia 2025

Black Hat Europe 2022
Black Hat Europe 2022