Attractive Directory and Deceptive Attacks in Organizational Environments
Exploración de ataques maliciosos en organizaciones: Pass-The-Hash, Mimikatz y DCSync. Análisis de configuraciones erróneas, propuestas de mitigación y reflexión sobre ciberseguridad en Argentina.
Phishing in Organizations: Findings from a Large-Scale and Long-Term Study
Explore findings from an extensive, long-term study on organizational phishing, covering vulnerability patterns, training effectiveness, and reporting mechanisms.
Social Engineering Metrics: Using Data Science for Valuable Reporting
Innovative approach to social engineering metrics using data science, focusing on meaningful measurements that reflect an organization's security posture and culture beyond traditional click rates.
Leveraging Social Engineering in Physical Security Assessment - 2017
Explore techniques for leveraging social engineering in physical security assessments, enhancing your ability to identify vulnerabilities and strengthen organizational defenses.
Realizing Software Security Maturity - The Growing Pains and Gains
Explore the challenges and opportunities of implementing a comprehensive application security program using the Software Assurance Maturity Model (SAMM) to guide success beyond basic OWASP Top 10 compliance.
Assessing Software Security Initiative Maturity: OpenSAMM and BSIMM Comparison - 2019
Explore OpenSAMM and BSIMM methodologies for evaluating software security maturity, comparing their features and learning best practices for implementation.
Thinking Outside the Bunker - Security as a Practice, Not a Target
Explore innovative approaches to cybersecurity, shifting focus from target-based to practice-oriented strategies for more effective and proactive protection.
Using Propaganda Techniques to Instill a Culture of Security
Learn effective security awareness techniques using propaganda methods, from historical examples to practical implementation strategies for cultural change in organizations.
Focusing on the Fool - Building an Awareness and Training Program
Discover strategies for creating effective security awareness programs that target human vulnerabilities and foster a culture of cybersecurity within organizations.

Cyber Threat Intelligence - Analysis and Mitigation Strategies
Explore Cyber Threat Intelligence: analyze data, identify threats, and develop proactive strategies to mitigate cyber-attacks. Learn to enhance organizational security through actionable insights.
OWASP SAMM2 - Your Dynamic Software Security Journey
Explore OWASP SAMM2's dynamic approach to software security, enhancing your development practices and strengthening application defenses throughout the lifecycle.
Growing Security Champions: Scaling SDL Through Development Partnerships
Scaling application security through Security Champions: strategies for selection, training, and empowering developers to handle security activities within their teams, improving overall security posture.
Security Selfie: Sizing Up Your AppSec Program with New Metrics
Discover innovative metrics to evaluate and enhance your application security program's effectiveness, presented by Facebook's Security Engineering Manager.
A Warrior's Journey - Building a Global AppSec Program
Discover strategies for establishing a robust global application security program, drawing insights from real-world experiences and best practices in the field.
Creating a Security Policy Framework That Works
Learn to develop an effective security policy framework, covering governance, compliance, and change management for robust organizational cybersecurity.
OWASP Software Assurance Maturity Model - SAMM
Explore OWASP's Software Assurance Maturity Model (SAMM), a framework for improving software security practices across organizations, presented by expert Bart De Win.
OWASP Top 10 Maturity Categories for Security Champions
Learn to become an effective Security Champion using OWASP's Top 10 Maturity Categories. Explore key responsibilities, maturity models, and strategies for improving organizational security posture.
Blinded by the Weakest Link - A New Perspective on Human Risk in Cybersecurity
Explore a new perspective on human risk in cybersecurity, challenging the "weakest link" mindset and offering innovative strategies to enhance security decision-making and behavior.
Threat Modeling In and For Your Organization
Comprehensive guide to implementing threat modeling practices within organizations, enhancing security strategies and fostering a proactive approach to identifying potential vulnerabilities.
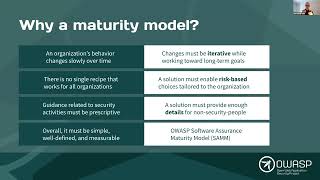
OWASP SAMM Project - Introduction to Software Assurance Maturity Model
Explore the OWASP SAMM framework for software assurance, learning key strategies to integrate security practices throughout the software development lifecycle.
Storytelling Techniques for Application Security - Beyond Penetration Testing
Explore interview-based research and consultancy techniques for enhancing application security maturity, fostering security champions, and building quality-minded teams.