In-Toto: Protecting Software Supply Chain in Cloud Native and Confidential Containers
探讨In-toto项目如何保护软件供应链完整性,以及在Confidential Containers等云原生应用中的应用,展示其在提供可信元数据和验证供应链步骤方面的优势。
CoCo-AS: First Confidential Computing Attestation Solution of CNCF
探索CNCF首个保密计算认证解决方案CoCo-AS,了解其技术架构、部署形式及如何利用Arm CCA实现TEE硬件平台的实际应用,助力云原生保密计算的发展。
STM32マイコン・セキュリティ - STM32H5でセキュア・マネージャをはじめよう
STM32H5マイコンの「STM32Trust TEEセキュア・マネージャ」を紹介。IoTセキュリティ強化に貢献する業界初の信頼できる実行環境の概念と評価方法を解説。
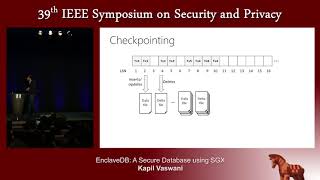
EnclaveDB: A Secure Database Using SGX
Explore EnclaveDB, a secure database engine using Intel SGX to protect sensitive data from malicious administrators and compromised systems, offering confidentiality, integrity, and freshness guarantees.
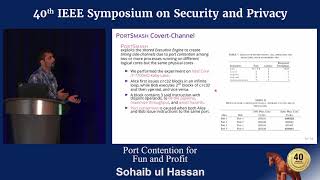
Port Contention for Fun and Profit
Explore SMT execution engine sharing as a side-channel leakage source, targeting ports to create a high-resolution timing side-channel for attacks on various architectures and applications.
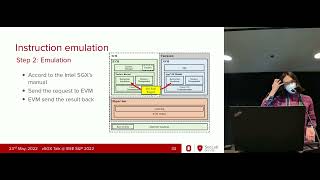
vSGX: Virtualizing SGX Enclaves on AMD SEV
Explore virtualizing Intel SGX enclaves on AMD SEV, addressing vendor lock-in and enabling software-defined trusted execution environments. Learn design goals, challenges, and performance implications.
Plundervolt - Software-Based Fault Injection Attacks against Intel SGX
Explore software-based fault injection attacks on Intel SGX, focusing on the Plundervolt technique that exploits voltage scaling interfaces to compromise enclave computations and cryptographic algorithms.
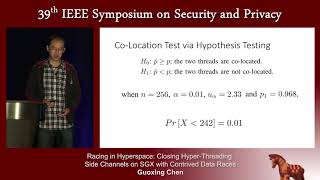
Racing in Hyperspace - Closing Hyper-Threading Side Channels on SGX
Explore techniques to mitigate Hyper-Threading side-channel vulnerabilities in Intel SGX enclaves using HYPERRACE, an LLVM-based tool that creates shadow threads and verifies physical-core co-location.
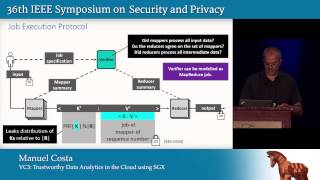
Trustworthy Data Analytics in the Cloud Using SGX
Explore trustworthy cloud-based data analytics using SGX technology. Learn about VC3, a system enabling secure MapReduce computations while preserving confidentiality and integrity of code and data.
LLC Cache Attacks: Applicability and Countermeasures
Exploring Last Level Cache attacks, their applicability across various scenarios, and potential countermeasures to enhance system security and protect user privacy.
Trusted Execution Environments Meet the Blockchain
Explore trusted execution environments, blockchain integration, and innovative solutions like TEEChain for secure, efficient payment channels and large-scale consensus mechanisms.
Abstracting TEE Silicon Implementations with Shims
Explore TEE silicon abstraction using shims, covering Anarchs, WebAssembly, runtime portability, and trusted computing. Learn deployment strategies and how to contribute to this innovative technology.
OP-TEE: Using TrustZone to Protect Our Own Secrets
Explore TrustZone technology for securing sensitive data in ARM CPUs, its potential applications, and the open-source OP-TEE implementation for Linux, with insights on current limitations and future possibilities.
Zephyr and Trusted Execution Environments for Microcontrollers
Explore Zephyr's implementation of trusted execution environments for ARM microcontrollers, covering hardware requirements, security configurations, and multi-core support.
Leaky Processors - Stealing Your Secrets With Foreshadow
Explore the Foreshadow vulnerability in modern processors and its implications for data security. Learn about potential exploits and mitigation strategies.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, covering use cases, prototypes, and CBOR expressions for secure execution environments.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, focusing on secure provisioning techniques for trusted execution environments in embedded systems.
A Leap in Automotive Security through Unikernel-based De-aggregation
Explore unikernel-based de-aggregation for enhanced automotive security, focusing on COQOS Hypervisor, Unikraft architecture, and TEE virtualization case study.
State of Intel SGX in Linux
Comprehensive overview of Intel SGX support in Linux, covering kernel interface, features, and confidential computing run-times. Explores the maturing SGX ecosystem and its status as a mainline kernel technology.
Introducing IO Devices into Trusted Execution Environments
Explore security and software changes for IO support in trusted execution environments, focusing on confidential computing and hardware-based TEEs like Intel SGX and TDX.
Secure and Dynamic Hardware Partitioning Management on Heterogeneous SoC
Explore dynamic hardware partitioning for heterogeneous SoCs, addressing security and performance challenges in complex IoT/edge systems with multiple OSs and TEEs.