Splunk SIEM Training Tutorials
Comprehensive tutorials on using Splunk for cybersecurity, covering incident response, threat hunting, and investigations across various attack scenarios and platforms.
Hunting the Adversary - Applying Cyber Threat Intelligence
Learn techniques for applying cyber threat intelligence and hunting adversaries in digital environments with expert John Bambenek.
Stanford Seminar - The Current State of Cybersecurity
Explore the current state of cybersecurity, including protection strategies, real-world cases, and defense mechanisms against advanced threats, phishing, and data breaches.
Analyzing Blind Eagle APT Group Using Marine Combat Profiling Techniques
Análisis del grupo APT-C-36 utilizando metodología "left of bang" y técnicas de perfilamiento de combate para obtener ventaja táctica en ciberseguridad.
Estrategias de Detección de Cyber-Amenazas
Explora estrategias avanzadas para detectar ciberamenazas modernas, analizando objetivos, métodos y herramientas de adversarios en ataques como Loaders, Trojans, Info Stealers y Ransomware.
You're Under Cyber-Attack - Now What?
Experts discuss cyber-attack response strategies, focusing on information sharing, risk management, and preparedness. Key topics include critical infrastructure protection, cyber insurance, and handling advanced persistent threats.

Attacking Information Mismanagement in SDN-Datastores
Explore vulnerabilities in Network Management Datastore Architecture, focusing on SDN infrastructures. Learn about semantic gaps, fuzzing techniques, and mitigation strategies for DoS and misconfiguration attacks.
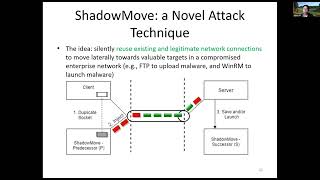
ShadowMove - A Stealthy Lateral Movement Strategy
Explore a stealthy lateral movement strategy for cybersecurity, focusing on the novel ShadowMove technique, its architecture, implementation, and potential impact on network security.
AI and Cybersecurity - The Twain Shall Meet
Explore AI's role in cybersecurity, focusing on advanced persistent threats, intrusion detection systems, and vulnerability analysis using ontologies and reasoning techniques.
Advanced Breaches of 2013 vs Behavioral Detection - GrrCON 2014
Explore advanced breach detection techniques, comparing signature-based and behavioral methods. Learn about NetFlow, metadata analysis, and real-world case studies from 2013 attacks.
2FA-Enabled Fraud: Dissecting Operation High Roller - Lecture 3.1.1
Dissecting Operation High Roller: Insights into sophisticated 2FA-enabled fraud techniques and their implications for cybersecurity professionals.
Weakest in the Herd - Securing End-of-Life Software
Explore strategies for identifying, assessing, and securing end-of-life software, including risk factors, potential threats, and mitigation techniques to enhance overall system security.
Fighting Next-Generation Adversaries with Shared Threat Intelligence
Exploring advanced threat intelligence sharing techniques to combat sophisticated cyber adversaries and prevent breaches through collaborative, anonymized data exchange.
Myths and Realities of Attribution Manipulation in Cybersecurity
Explore the complexities of cyber attack attribution, including copycats and false flags. Learn about the challenges in identifying malicious actors and the future of threat intelligence.
Effectiveness in Simplicity - The Taskmasters APT
Explore the Taskmasters APT's effectiveness through simplicity in this concise presentation by Elmar Nabigaev, focusing on key insights and practical applications.
Quantitatively Comparing APTs with MISP - MISP Summit 2018
Explore quantitative methods for comparing Advanced Persistent Threats using MISP, enhancing threat intelligence analysis and cybersecurity strategies.
Becoming a Dark Knight - Adversary Emulation Demonstration for ATT&CK Evaluations
Explore adversary emulation techniques using real-world APT scenarios to improve cybersecurity defenses and industry standards through MITRE ATT&CK Evaluations.
Ongoing EvilEye Campaigns Targeting CCP Adversaries
Explore ongoing EvilEye campaigns targeting CCP adversaries, analyzing tactics, targets, and implications for cybersecurity professionals and policymakers.
Lazarus Group's Undercover Operations in South Korea 2022-2023
Detailed analysis of Lazarus Group's recent cyber campaigns in South Korea, covering infiltration methods, lateral movement techniques, and data exfiltration strategies used by this sophisticated threat actor.
A Tale of Lazarus and His Family - Hack.lu 2023
Explore the pervasive influence of Lazarus and related threat actors in cybersecurity, uncovering their tactics, techniques, and global impact on digital landscapes.
The Dark Side of EDR - Repurposing EDR as an Offensive Tool
Explore innovative attack vector transforming EDR into stealthy malware. Learn to bypass security features, exfiltrate data, and establish persistent control, focusing on Palo Alto Networks Cortex XDR.