Securing the Supply Chain: A Practical Guide to SLSA Compliance from Build to Runtime
Dive into SLSA compliance for supply chain security using CNCF tools. Explore GitHub Actions, Cosign, Kyverno, in-toto, and Kubescape to secure software from build to runtime in Kubernetes ecosystems.
Secure Supply Chain in Kubernetes
Implementação de pipelines seguros e aplicações confiáveis para Kubernetes usando ferramentas open-source como OPA e Cosign para verificações e assinaturas em uma cadeia de suprimentos de software segura.
In-Toto: Protecting Software Supply Chain in Cloud Native and Confidential Containers
探讨In-toto项目如何保护软件供应链完整性,以及在Confidential Containers等云原生应用中的应用,展示其在提供可信元数据和验证供应链步骤方面的优势。
Kicking Security Chain Attacks to the Curb with Kyverno and Notary in GitOps
使用Kyverno和Notary等CNCF项目建立容器镜像信任,验证资源,并在GitOps中实施以提高软件供应链安全性。展示如何应对现代Kubernetes部署中的安全挑战。
Security Threat Model Analysis and Protection Practice in Edge Computing Scenarios
Analyze security threats in edge computing, explore KubeEdge's audit process, and learn protection practices for cloud-native environments. Gain insights on improving security in multi-cloud and hybrid scenarios.
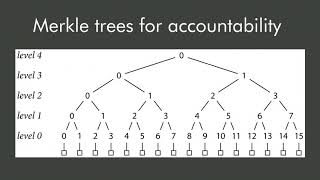
Securing the Software Supply Chain - Go Checksum Database
Exploring Go's checksum database design to secure software supply chains, addressing vulnerabilities in third-party dependencies and enhancing ecosystem integrity.
We're Not Doomed! How to Successfully Manage Software Supply Chain Security
Discover strategies to enhance DevSecOps and protect against software supply chain attacks using real-world examples and the OSCAR framework. Learn to assess and improve your organization's security practices.
Policy Compliance with Sigstore - From Signing Software to Validating the Whole Software Supply Chain
Explore sigstore for software signing and verification, and learn how to implement policy compliance in cloud-native software build and deployment processes using automation and tools.
Dependency Hijacking Vulnerability in Microsoft Teams - Supply Chain Security Gaps
Explore real-world dependency hijacking in Microsoft Teams, understanding software supply chain vulnerabilities and learning strategies to protect infrastructure, SDLC, and code.
How to Secure Your Software Supply Chain on Windows Server
Explore challenges and solutions for securing software supply chains on Windows Server, focusing on Mirantis Container Runtime's role in providing enterprise-grade security for container workflows and Kubernetes nodes.
Software Bill of Materials (S-BoM) - Reducing Risk in Third-Party Components
Explore best practices for managing third-party component risks using software bill-of-materials (S-BoM). Learn to create S-BoMs, identify vulnerabilities, and automate security responses in polyglot environments.
SBOM SmackDown - Conquering Software Supply Chain Risks with OWASP CycloneDX
Explore Software Bill of Materials (SBOM) and learn how OWASP CycloneDX standard enhances software supply chain transparency, enabling better risk-based decisions and compliance with government mandates.
Analyzing Google's SLSA Framework for Securing Software Supply Chains
Explore Google's SLSA framework for securing software supply chains, covering key areas, controls, and additional considerations beyond the framework's scope.
OWASP Dependency Track - Software Composition Analysis and Vulnerability Management
Explore OWASP Dependency Track: manage software components, analyze vulnerabilities, and enhance security with features like Software Bill of Materials, policy engine, and dependency graphs.
Measure and Improve Software Supply Chain Assurance with OWASP SCVS
Learn to assess and enhance software supply chain security using OWASP's Software Component Verification Standard (SCVS), improving overall cybersecurity posture.
Threat Modeling the CI/CD Pipeline to Improve Software Supply Chain Security
Explore threat modeling for CI/CD pipelines to enhance software supply chain security, covering key vulnerabilities, data flow analysis, and mitigation strategies.
Software Supply Chain Security
Explore software supply chain security with expert Vandana Verma, covering key concepts, best practices, and strategies to protect your development pipeline from vulnerabilities and attacks.
Benchmarking the Security of Your Software Supply Chain
Learn to assess and enhance the security of your software supply chain through benchmarking techniques, improving overall cybersecurity posture and reducing vulnerabilities.
Real World Security - Software Supply Chain
Explore software supply chain security through a case study on misconfigured registries, threat modeling, and best practices for securing the build-ship-run pipeline.
Implementing a Supply Chain Approach to Build and Deploy Secure Applications - AppSecEU 2016
Explore implementing a supply chain approach to build and deploy secure software, focusing on trust, standardization, and automation in the software delivery pipeline.
Introduction to the Newest Addition to the OWASP Top 10 - A9 Guidelines
Experts discuss the new OWASP A9 guideline on insecure open source libraries, offering insights on component usage, best practices, and real-world challenges in mitigating risks in agile development.