Project Cerberus: Hardware Root of Trust for Cloud Security
Explore hardware-enforced secure boot and measured boot with Project Cerberus, a cryptographic microcontroller enhancing firmware security for cloud platforms and data centers.
Secure Boot from A to Z - Building a Complete Chain-of-Trust
Comprehensive guide to implementing Secure Boot on embedded systems, covering encryption, signatures, bootloaders, and filesystem security with practical examples and real-world applications.
Zephyr and Trusted Execution Environments for Microcontrollers
Explore Zephyr's implementation of trusted execution environments for ARM microcontrollers, covering hardware requirements, security configurations, and multi-core support.
Protected Execution Facility: Enhancing Security for Virtual Machines
Explore IBM's Protected Execution Facility for enhanced security in cloud computing. Learn about secure virtual machines, architecture modifications, and safeguards against compromised components in Power Architecture servers.
Implementing UEFI-based Secure Boot and OTA Updates for Embedded ARM Devices
Explore secure boot implementation and OTA updates for embedded ARM devices using UEFI, covering challenges, solutions, and practical integration techniques for robust system security.
Implementing Secure Boot and Disk Encryption on Tegra Platforms
Secure boot and disk encryption implementation on Tegra platforms: lessons learned, challenges faced, and solutions developed for a robust and future-proof system using vendor tools and custom OS builds.
From a Security Expert's Diary: DOs and DON'Ts When Choosing Software for Embedded Products
Practical advice on selecting software for embedded products, covering distribution choices, module selection, support assessment, update systems, and security considerations.
Will it Boot? The Case for Platform Standards in Embedded Systems
Explore embedded Linux ecosystems, UEFI, and platform standards for bootable systems. Learn about architecture, security, and certification in embedded development.
Secure Bootloaders and Secure Software Update Support in CIP - Civil Infrastructure Platform
Explore secure bootloaders and software updates in CIP, focusing on implementation, IEC-62443 compliance, and the collaborative efforts of CIP workgroups to enhance industrial software security.
Dynamic Key Managed PowerPC Guest Secure Boot
Learn about dynamic key secure boot for Power LPARs, addressing static key limitations and exploring new mechanisms for enhanced boot-level security on PowerPC systems.
Secure Boot - What Is It and Do I Need It?
Explore secure boot in IoT: its components, use cases, threats it prevents, and implementation status. Learn key elements for supporting secure boot in connected devices.
Design and Implementation of a Security Architecture for Critical Infrastructure Industrial Control Systems
Comprehensive security architecture for critical infrastructure, addressing nation-state cyber threats. Covers hardware roots of trust, secure boot, and integrity measures across various systems and networks.
Boot to Cloud Security Considerations for IoT Systems
Comprehensive guide to designing secure IoT systems, covering boot processes, data flow, authentication, and cloud connectivity. Offers best practices for embedded developers using open-source software and standards.
Maintaining a Community BSP Layer: Updating Meta-Tegra Through Major Changes
Explore strategies for maintaining the meta-tegra BSP layer amid major SDK and OpenEmbedded changes, covering bootloader updates, trusted OS transitions, and support for future Jetson platforms.

Securing TPM Secrets with TXT and Kernel Signatures
Explore securing TPM2 NVRAM data using Intel TXT and tboot extensions for kernel signature verification, enhancing protection while maintaining usability during kernel updates.
Secure Boot and Over-the-Air Updates - Challenges and Solutions
Explore secure boot and over-the-air update challenges in embedded systems, focusing on implementation complexities and best practices for robust, tamper-resistant solutions.
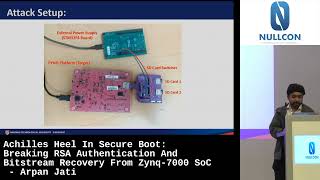
Breaking RSA Authentication and Bitstream Recovery From Zynq-7000 SoC
Uncovers critical vulnerability in Zynq-7000 SoC's secure boot, allowing RSA authentication bypass. Explores implications for embedded device security and trusted computing.
Secure Boot Vulnerabilities and Private Key Leaks - Implications and Solutions
Explore recent security breaches, their implications, and learn how to protect yourself online using two-factor authentication and tools like YubiKey.
Booting with Caution: Dissecting Secure Boot's Third-Party Attack Surface
Dissect Secure Boot's third-party attack surface, exploring vulnerabilities and potential exploits in boot processes.
Is Remote Attestation Relevant for Embedded Devices? - RIOT Summit 2024
Explore remote attestation's relevance for embedded devices, examining latest developments, challenges, and potential benefits in the context of Trusted Execution Environments and RIOT OS.
The Cyber Resilience Act: Navigating Its Impact on Yocto-Based Products
Explore the Cyber Resilience Act's impact on Yocto-based products, covering key provisions, security compliance, challenges, and best practices for building secure embedded systems.