Revitalizing Product Security Through Bug Bounty Programs - Zephyr Health Case Study
Discover how implementing a private bug bounty program transformed Zephyr Health's development culture, motivating teams to prioritize security and leverage crowdsourced expertise.
What You Missed During Black Hat and DEFCON - Security Conference Highlights
Explore key highlights from Black Hat and DEFCON, including car hacking, Android security, policy changes, and malware analysis, as presented by Bugcrowd's VP of Operations.
Critical Vulnerabilities and Bug Bounty Programs
Explore critical vulnerabilities uncovered through bug bounty programs, their impact, and strategies for effective vulnerability management and disclosure in cybersecurity.
Barracuda Bug Bounty Program Evolution - From Inception to Bugcrowd Platform
Explore Barracuda's bug bounty program evolution, from its 2010 inception to current Bugcrowd platform, covering impact, metrics, and rewards for security researchers.
5 Tips for a Successful Bug Bounty Program
Discover key strategies for implementing an effective bug bounty program, including common pitfalls to avoid and expert insights for maximizing benefits and security outcomes.
How the Crowd Outperforms Traditional Security Testing
Explore how crowdsourced security testing outperforms traditional methods, with insights on implementation, benefits, and real-world examples from successful bug bounty programs.
The Art and Value of Bug Bounties
Explore cybersecurity trends, bug bounty myths, and the future of ethical hacking with experts Keren Elazari and Casey Ellis in this informative webinar on the value of crowdsourced security.
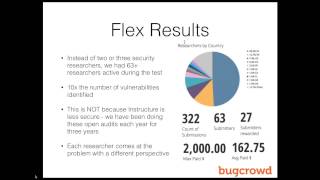
Key Takeaways from Instructure's Bug Bounty Program
Discover insights from Instructure's Bug Bounty program, including their innovative approach to security audits, crowdsourced penetration testing, and key lessons learned for enhancing cybersecurity practices.
How DevOps Becomes DevOpsSec - Chris Raethke, Bugcrowd Webinar
Explore how DevOps evolves into DevOpsSec, integrating security into development processes. Learn strategies for effective implementation and team collaboration.
Finding Bugs with Burp Plugins and Bug Bounty 101
Learn to create automated testing plugins for Burp and explore bug bounty programs. Gain insights on finding vulnerabilities, tips for success, and valuable resources for cybersecurity enthusiasts.
What Is Bug Bounty?
Explore bug bounty basics, including potential earnings, required skills, and benefits for companies. Learn how to get started and what to expect in this comprehensive introduction.
XML External Entity Injection
Learn to identify, exploit, and mitigate XML External Entity (XXE) vulnerabilities. Gain practical skills to enhance application security and protect against data disclosure and system impacts.
Profiling the Attacker - Using Offender Profiling in SOC Environments by James Stevenson
Explore techniques for profiling cyber attackers, including asset classification, attack analysis, and motive discernment, to enhance security operations and threat intelligence.
Fuzzing XSS Sanitizers for Fun and Profit - Tom Anthony
Explore XSS sanitizer fuzzing techniques with Tom Anthony, from his hacking past to current cybersecurity insights. Learn about innovative approaches to discovering vulnerabilities in web applications.
Why Humans Suck at Calculating Risk and How It Affects Security - Masha Sedova
Explore human biases in risk assessment and their impact on cybersecurity decision-making. Learn effective strategies for addressing vulnerabilities and improving organizational security posture.
Bugcrowd University - Broken Access Control Testing
Learn white hat hacking techniques for identifying and exploiting broken access control vulnerabilities, including IDOR, path traversal, and logic flaws, to enhance your bug bounty hunting skills.
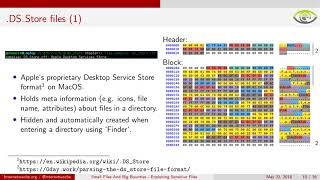
Small Files and Big Bounties - Exploiting Sensitive Files
Explore techniques for exploiting sensitive files to uncover vulnerabilities and earn bounties. Learn from Internetwache team's expertise in identifying and leveraging small but critical files.
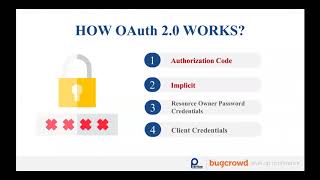
Hacking OAuth 2.0 for Fun and Profit
Discover high-impact vulnerabilities in OAuth 2.0 integrations. Learn attack techniques, methodologies, and case studies for token stealing, code stealing, CSRF, and token impersonation.
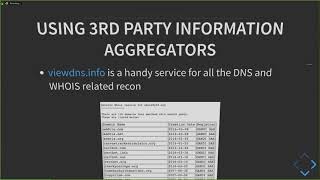
Practical Recon Techniques for Bug Hunters & Pen Testers
Discover effective reconnaissance strategies for identifying vulnerabilities and enhancing security assessments in this informative session led by expert Bharath.
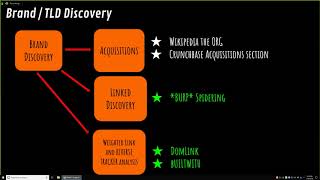
Bug Bounty Hunter Methodology V3
Comprehensive guide to modern bug bounty hunting techniques, covering recon, automation, and vulnerability discovery for web and mobile applications.
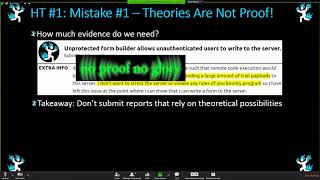
Trickle Down PwnOnomics
Learn how to succeed in bug bounty hunting, from zero experience to consistent earnings, with practical tips and strategies for effective vulnerability discovery and reporting.