Hunting the Adversary - Applying Cyber Threat Intelligence
Learn techniques for applying cyber threat intelligence and hunting adversaries in digital environments with expert John Bambenek.
TTP-based Threat Hunting with Security Analytics and Falco Alerts
Explore attacker techniques and defender strategies using Unguard. Learn to conduct reconnaissance, gain access, and achieve persistence. Discover how to detect compromises with Dynatrace and Falco for real-time monitoring and forensic analysis.
Dynatrace Security Investigator App - Sneak Peek and Demo
Explore Dynatrace's Security Investigator App for faster, evidence-driven security investigations and threat hunting. Learn its unique approach, branch-based analysis, and see a live demo.
Advanced Threat Hunting With Splunk
Learn advanced threat hunting techniques using Splunk, covering installation, data analysis, search queries, and complex event analysis for enhanced cybersecurity operations.
Starting with Velociraptor Incident Response
Learn to set up and use Velociraptor IR for endpoint monitoring, threat hunting, and digital forensics. Covers installation, configuration, client management, hunts, artifacts, and key features.
Quick and Dirty Cloud Incident Response Tactics - Santi Abastante
Tácticas rápidas de respuesta a incidentes en la nube: demostración práctica de detección y mitigación de amenazas en AWS utilizando herramientas nativas, basado en escenarios reales de ataques.
Introdução ao Cyber Threat Intelligence
Explore os fundamentos e desafios da inteligência de ameaças cibernéticas com especialistas renomados. Aprenda sobre CTI, segurança de aplicativos e sua relevância no cenário atual de cibersegurança.
NetFlow? Where We're Going, We Don't Need NetFlow - Enhancing Threat Hunting and Blue Team Operations
Innovative approach to log analysis for enhanced threat hunting and blue team operations, focusing on outbound network traffic visibility without relying on NetFlow.
Threat Hunting in the O365 Ecosystem - David Stubley, 7Elements
Explore threat hunting techniques in Office 365, focusing on audit logs, login patterns, and data exfiltration. Learn from a real-world compromise case study.

Achieving PEAK Performance: Introducing the PEAK Threat Hunting Framework
Discover PEAK, a new threat hunting framework enabling diverse techniques like exploratory data analysis and machine learning to uncover elusive threats and elevate your security program.
Industrial Control Systems Cybersecurity - 2020 Year in Review and Threat Landscape
Explore key findings from 2020's ICS cybersecurity landscape, including new threat groups, vulnerabilities, and insights from threat hunts and incident response engagements.
5 Considerations for ICS Incident Response
Explore key considerations for effective ICS incident response, including preparation, decision-making, shutdown criteria, root cause analysis, and engaging IR teams for safe and efficient recovery.
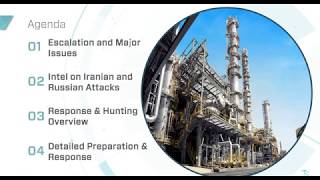
Rising Cyber Escalation: US, Iran, Russia ICS Threats and Response
Explore rising cyber tensions between US, Iran, and Russia, with insights on threat intelligence, defense strategies, and response planning for industrial control systems and critical infrastructure.
Lessons Learned from Threat Hunting and Responding to Industrial Intrusions
Insights from industrial cybersecurity experts on threat hunting and incident response, highlighting key findings from the 2018 ICS Year in Review report.
Six Steps to Effective ICS Threat Hunting
Learn effective ICS threat hunting with a 6-step model, real-world scenarios, and expert insights. Explore environment vs threat hunting, intel feeds, and practical approaches to enhance industrial cybersecurity.

Security Onion 2 Release Announcement and Live Demo
Discover the latest features and improvements in Security Onion 2 through an in-depth release announcement and live demonstration, showcasing advanced capabilities for network security monitoring and threat detection.
Security Onion Hybrid Hunter Beta 2 - New Hunt Interface Overview
Explore Security Onion's new Hunt interface in Hybrid Hunter Beta 2, enhancing threat detection and investigation capabilities for enterprise security teams.

Hunting Malware with Suricata Metadata - Security Onion Conference 2021
Explore advanced threat hunting techniques using Suricata metadata, focusing on malware detection, incident response, and proactive network security strategies.
KillTheHashes - 30 Million Malware DNA Profiling Exercise - Hack.lu 2016
Explore malware profiling techniques and tools for identifying unique digital fingerprints, enabling early detection and categorization of new threats through characteristic family analysis.
Visualizing MISP and ATT&CK Data in Maltego
Explore techniques for visualizing threat intelligence data from MISP and ATT&CK frameworks using Maltego, enhancing cybersecurity analysis and decision-making.
Let Me YARA That For You
Explore advanced YARA rule creation techniques for malware detection and analysis, enhancing your cybersecurity skills and threat hunting capabilities.