Getting to Know the Exploit Prediction Scoring System (EPSS)
Explore the Exploit Prediction Scoring System (EPSS), a data-driven approach to estimating real-world vulnerability exploitation likelihood.
KIM: Chaos in the Medical Telematics Infrastructure - Security Analysis
Analyse der Sicherheit von KIM, dem E-Mail-System im deutschen Gesundheitswesen. Aufdeckung von Schwachstellen in Schlüsselausgabe, Software und Nutzerfreundlichkeit trotz theoretisch sicherer Kryptographie.
Bumpy Roads - Exploring Security Vulnerabilities in Regional Carsharing Systems
Entdecke Schwachstellen und unsichere Software eines regionalen Carsharing-Anbieters. Tauche ein in ein Korallenriff voller Sicherheitslücken und lerne über Web-Applikationen, deren Schwachstellen und unsicheres Design.
Adriel Desautels at BDF 2015 - The Secretive Zero Day Exploit Market
Explore the secretive zero-day exploit market, its misunderstandings, dual-purpose nature, and real-world applications in intelligence and law enforcement. Gain insights from a former broker on market realities and regulatory challenges.
Predicting Vulnerability Exploitation - How to Assess Cybersecurity Risks
Predicting vulnerability exploitation using data from 10 million hosts. Explores factors influencing hacker decisions and presents models to assess exploitation risk, aiding in cybersecurity and risk management.
Our Time in a Product Review Cabal - Uncovering Malware and Vulnerabilities in Free Products
Explore the journey of a product review group, uncovering vulnerabilities in free tech products and learning to detect and mitigate security issues in various smart devices.
Fighting Advanced Threats at Their Software Roots - Scaling Software Security
Exploring strategies to scale software security beyond developers, addressing vulnerabilities at their roots, and transforming the software ecosystem to combat advanced threats effectively.
From Facepalm to Brain Bender - Advanced Web Security Challenges
Explore web security challenges, from basic vulnerabilities to complex exploits, with insights from industry experts on detection, prevention, and mitigation strategies.

Video Game Security - Hacking Techniques and Protection Mechanisms
Explore video game hacking techniques, from business risks to memory manipulation, covering client-side and network-based attacks, with insights applicable to various software industries.
The Software, Not the Human, Is the Weakest Link
Explore how software vulnerabilities, not human error, are the primary security risk in modern systems. Learn to shift focus from blaming users to improving code security.
EU's Efforts to Secure Open Source Software
Explore EU's approach to securing open source software, comparing it with US strategies and examining Ireland's role in addressing OSS supply chain threats.
Open Source Supply Chain Threat Landscape - A Moving Target
Explore the evolving landscape of open source supply chain threats, their impacts, and strategies for implementing developer-first security to counter sophisticated attacks.
Global Software Vulnerability Standard Birds of a Feather Discussion
Explore the Global Software Vulnerability Standard (GSVS) in this Linux Foundation discussion, addressing key aspects of software security and vulnerability management.
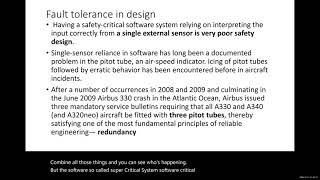
Insecure, Unsafe, and Lying Software
Explore the critical issues of insecure, unsafe, and deceptive software with insights from Eduardo Fernandez of Florida Atlantic University, addressing key cybersecurity challenges.
OpenSSL After Heartbleed - Lessons Learned and Project Improvements
Explore OpenSSL's transformation post-Heartbleed: enhanced team, transparency, development processes, and project vitality. Learn about security improvements and future plans.
New Phones, Software and Chips - New Bugs?
Explore cutting-edge vulnerabilities in modern smartphones, examining software and hardware innovations that introduce new security challenges.
5 AppSec Stories and What We Can Learn From Them
Explore real-world application security incidents and extract valuable lessons to enhance your cybersecurity practices and prevent similar vulnerabilities in your own systems.
Why Is There No Free Software Vulnerability Database?
Explore the need for a free software vulnerability database, its challenges, and potential solutions. Learn about Package URL, data models, and future plans for improved cybersecurity.
Supply Chain Shenanigans - Evil npm and Shady NuGet
Explore npm and NuGet supply chain vulnerabilities, uncovering potential threats and security risks in package management ecosystems for software developers and cybersecurity professionals.
Future Open Source LLM Kill Chains - Security Risks and Mitigation Strategies
Explore potential security risks in open-source AI ecosystems, focusing on LLM vulnerabilities and kill chains. Learn mitigation strategies to protect against sophisticated adversaries in the evolving AI landscape.
Misconception About the Security of Open Source Software - Study Case: Ubuntu Linux and LibreOffice
Explore common misconceptions about open-source software security, focusing on Ubuntu Linux and LibreOffice as case studies.