Penetration Testing Bootcamp
Learn the basics of Penetration Testing and get introduced to Web Application penetration testing with this course that is a part of the open source cybersecurity training initiative.

Burp Suite Essentials
Learn to intercept, scan, and test web applications using Burp Suite's powerful features, including Proxy, Repeater, Scanner, and WebSocket testing capabilities.
Bugbounty Hunting
Comprehensive guide to bug bounty hunting, covering tools, techniques, and vulnerabilities for ethical hacking and cybersecurity enthusiasts.

CompTIA PenTest+ Full Course - PT0-002
Comprehensive penetration testing training covering planning, reconnaissance, vulnerability analysis, exploitation techniques, and reporting, with hands-on labs using industry-standard tools and frameworks.
Mastering Nessus Scans - A Guide to Host Discovery, Basic Network Scan and Web Application Tests
Discover essential Nessus scanning techniques for network security, including host discovery, basic network scans, and web application tests. Learn step-by-step instructions and best practices.
Ethical Hacking - Learn to Hack
Comprehensive ethical hacking training covering networking, Linux, Python, reconnaissance, vulnerability scanning, exploitation, and hands-on practice with multiple target systems.

Web App Testing - Enumeration
Learn web app enumeration techniques including subdomain discovery, vulnerability scanning, and using tools like Burp Suite and Nikto to identify potential security weaknesses.

Zero to Hero Pentesting - Scanning Tools and Tactics
Comprehensive tutorial on penetration testing tools and techniques, covering Nmap, Nessus, Metasploit, and BurpSuite. Includes practical demonstrations, Q&A session, and industry insights for aspiring cybersecurity professionals.
Metasploit Framework Training for Beginners
Learn automated penetration testing, Windows privilege escalation, antivirus testing, vulnerability scanning, and firewall evasion using Metasploit Framework and related tools.
Red Team Recon Techniques - Red Team Series
Comprehensive guide on red team reconnaissance techniques, covering passive and active methods for gathering intelligence on target systems, networks, and organizations.
Burp Suite Tutorials
Comprehensive Telugu tutorials on Burp Suite, covering setup, key features, and web application security testing techniques for aspiring ethical hackers and penetration testers.
Metasploit Arabic Course
دورة شاملة باللغة العربية لتعلم استخدام Metasploit، أداة قوية لاختبار الاختراق واكتشاف الثغرات الأمنية في الأنظمة والشبكات.
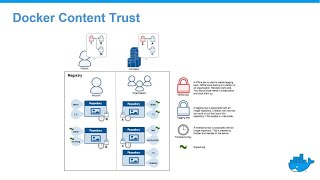
Creating a Secure CI/CD Pipeline with Docker
Erfahren Sie, wie Docker Enterprise eine sichere Software-Entwicklungs-Pipeline mit Content Trust und Vulnerability Scan unterstützt, inklusive einer Live-Demonstration der Implementierung.
La sécurité - Un pilier de la plateforme Docker Enterprise
Découvrez les composants de sécurité intégrés de Docker Enterprise : contrôles d'accès, zones sécurisées, registre fiable, scan de vulnérabilités et politiques de conformité pour vos applications conteneurisées.
Focused on Security Measures in Kubernetes Environment
Explore Kubernetes security measures, including shared responsibility, network control, encryption, secret management, and vulnerability checks across the container lifecycle.
Container Image Security Best Practices
Explore best practices for securing container images, enhancing your cloud-native application's safety and reliability in production environments.
Securing Container Supply Chain in CI/CD with Notary Project, ORAS and Harbor
探讨如何利用Harbor、Notary Project和ORAS等开源技术来保障CI/CD流程中容器镜像和OCI工件的安全性和完整性,确保只部署可信、无漏洞且符合策略的容器。
Implementando Aplicativos em um Ambiente Seguro com Terraform, Trivy e Postee
Aprenda a implementar aplicativos de forma segura usando Terraform para automação de infraestrutura e ferramentas como Trivy e Postee para identificar e corrigir vulnerabilidades em contêineres.
Ferramentas AST e Arquiteturas MAD e Monolítica na Segurança de Aplicações Modernas
Explore ferramentas de segurança para arquiteturas modernas e monolíticas. Aprenda a integrar sistemas de detecção, firewalls e scanners no desenvolvimento, garantindo conformidade e mitigando riscos.
Hacker-Powered Security in Agile Software Development - Webinar
Explore hacker-powered security in agile software development, covering open source risks, bug bounty benefits, and integrating security into continuous delivery workflows.
Automating App Security Tests in Development with Docker
Learn to automate application security testing using Docker. Explore tools like ZAProxy, nikto, and SQLmap for continuous attack simulation in the software development lifecycle, with live demonstrations.