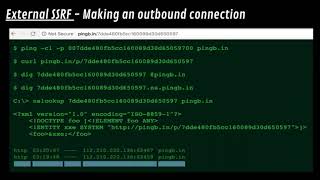
Server Side Request Forgery
Learn to identify, exploit, and mitigate Server-Side Request Forgery vulnerabilities. Covers external and internal SSRF, bypassing blacklists, and includes practical demonstrations and real-world examples.
Car Hacking: A College Student's Perspective - LevelUp 0x04
Explore car hacking techniques, tools, and targets from a student's perspective. Learn about initial access, hardware hacking, and canvas basics for automotive security.
LevelUp 0x04 - Blueprint for Becoming a Penetration Tester
Blueprint for aspiring pen testers: expert insights, career tips, and actionable steps to enter the field of ethical hacking and penetration testing.
Bug Hunting as a Team: Challenges and Insights - LevelUp 0x04
Insights on collaborative bug hunting: organizing teams, sharing information, splitting bounties, and overcoming challenges in the evolving field of cybersecurity.
OWASP Amass - Discovering Internet Exposure and Network Mapping - LevelUp 0x04
Discover internet-facing assets and enhance network visibility using OWASP Amass. Learn subdomain enumeration techniques and tools for improved cybersecurity and asset management.
LevelUp 0x04 - The Infinite Game of Hacking and Future of Crowdsourced Security
Explore the 'infinite game' of hacking and the future of crowdsourced security with Bugcrowd's CEO Ashish Gupta in this insightful welcome address for LevelUp 0x04.
LevelUp 0x04: Advanced Bug Bounty Techniques - Day 2
Explore advanced bug bounty techniques and strategies with industry experts in this comprehensive cybersecurity event focused on enhancing hacking skills and knowledge.
LevelUp 0x04 - Introduction to Ethical Hacking and Bug Bounty - Day 1
Explore cutting-edge cybersecurity insights and strategies at this free conference, featuring expert talks and discussions on the latest industry trends and challenges.
Reducing the Cost of Free Speech - The Law and You
Explore legal strategies to protect free speech and reduce associated costs with insights from EFF's Nate Cardozo. Learn about rights, risks, and practical approaches for digital activists and security researchers.
iPhone Baseband Research and Reversing - Security Insights and Techniques
Explore iPhone baseband internals, research techniques, and tools for firmware analysis, reversing, and exploitation. Gain insights into Qualcomm baseband architecture and vulnerabilities.
IoT Security - Attacker's Perspective on Common Vulnerabilities
Explore IoT vulnerabilities from an attacker's perspective, covering famous exploits, OWASP IoT Top10, and practical attack methodologies. Gain insights for both security professionals and IoT developers.
From IVI to CAR in a Box - Building and Testing Automotive Systems
Explore building a simulated car system, from in-vehicle infotainment to a complete "Car in a Box" setup, with insights on ECU integration and safety precautions.
What You Reap, Is What You Sow by Chris Roberts
Explore cybersecurity challenges, industry failures, and potential solutions in an evolving technological landscape. Gain insights on improving security practices and addressing emerging threats.
Behind the Curtain - Safe Harbor and Department of Defense
Explore legal protections, risks, and trends in vulnerability disclosure with DoD experts. Learn about safe harbor policies, submission processes, and the evolving landscape of bug bounty programs.
From CTF to CVE by Joe Gray
Explore the journey from Capture The Flag challenges to real-world vulnerability discovery, emphasizing skill application, persistence, and responsible disclosure in cybersecurity research.
What's in My Hacking Tool Box? by Richard Rushing
Explore a seasoned hacker's toolkit and methodology for penetration testing, covering various domains including malware analysis, mobile app exploitation, and API security.
Bad API, HAPI Hackers!
Explore API hacking methodology, from information gathering to privilege escalation. Learn techniques for testing vulnerabilities, automating processes, and uncovering critical security flaws in web applications.
API Security 101 by Sadako
Explore API security fundamentals, common vulnerabilities, and real-world examples. Learn testing methodologies, fuzzing techniques, and gain insights from notable bug discoveries in this beginner-friendly introduction.
Finding Bugs with Binary Ninja by Jordan Wiens
Explore bug-finding plugins for Binary Ninja and learn techniques to extend them for discovering various bug classes in this informative demonstration.
Social Engineering 101 by Matteo Cagnazzo
Discover techniques for gathering company information through OSINT and social engineering. Learn how non-technical methods can complement technical security assessments in bug hunting.
Serverless Top 10 Vulnerabilities by Tal Melamed
Explore serverless security vulnerabilities, their impact, and prevention techniques. Learn how traditional threats evolve in serverless environments and discover best practices for securing cloud-native applications.