Privacy and Access Control for Outsourced Personal Records
Cryptographic system GORAM protects outsourced data secrecy, integrity, and access control while ensuring anonymity and unlinkability, addressing cloud storage security concerns for sensitive applications.
Cracking-Resistant Password Vaults Using Natural Language Encoders
Innovative password vault security using natural language encoders to generate plausible decoys, resisting offline cracking and forcing online attacks. Implements NoCrack system for enhanced protection.
A Shared Cache Attack That Works Across Cores and Defies VM Sandboxing and Its Application to AES
Explore a novel cross-core cache attack that bypasses VM sandboxing, exploiting shared L3 cache vulnerabilities to compromise AES encryption in cloud computing environments.
Readactor: Practical Code Randomization Resilient to Memory Disclosure
Explore practical code randomization techniques resilient to memory disclosure attacks, enhancing software security against return-oriented programming and other code-reuse threats.
Leave Me Alone - App-Level Protection against Runtime Information Gathering on Android
Explores app-level protection against runtime information gathering on Android, proposing App Guardian to pause suspicious background processes and thwart malicious monitoring attempts without system modifications.
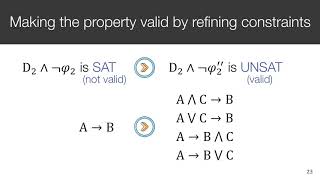
Transys - Leveraging Common Security Properties Across Hardware Designs
Explore hardware security validation techniques and learn how to leverage common security properties across different designs using Transys, improving efficiency in vulnerability detection.
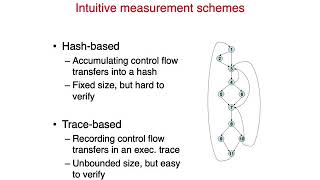
OAT - Attesting Operation Integrity of Embedded Devices
Innovative framework for attesting operation integrity of embedded devices, addressing control-flow hijacks and data-only attacks in IoT systems through lightweight measurement and verification techniques.
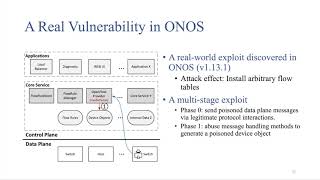
Unexpected Data Dependency Creation and Chaining - A New Attack to SDN
Explores a novel attack on Software-Defined Networking, demonstrating unexpected data dependencies and their chaining effects. Covers attack mechanics, impacts, and potential countermeasures.
Plundervolt - Software-Based Fault Injection Attacks against Intel SGX
Explore software-based fault injection attacks on Intel SGX, focusing on the Plundervolt technique that exploits voltage scaling interfaces to compromise enclave computations and cryptographic algorithms.
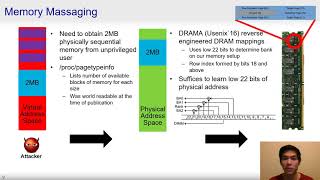
RAMBleed - Reading Bits in Memory Without Accessing Them
Explores RAMBleed, a novel Rowhammer-based side-channel attack that can read sensitive data from DRAM without accessing it, demonstrating security implications for confidentiality even with ECC memory.
The Many Kinds of Creepware Used for Interpersonal Attacks
Explores the landscape of "creepware" apps used for interpersonal attacks, introducing CreepRank algorithm to identify such apps. Discusses various types and implications for cybersecurity and personal safety.
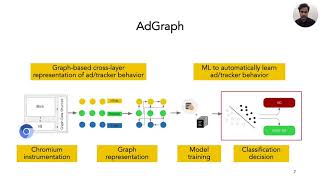
AdGraph: A Graph-Based Approach to Ad and Tracker Blocking
Innovative graph-based machine learning approach for detecting online ads and trackers, offering improved accuracy and performance compared to traditional filter list methods.
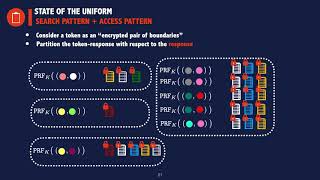
The State of the Uniform - Attacks on Encrypted Databases Beyond the Uniform Query Distribution
Explores novel value reconstruction attacks on encrypted databases, leveraging search-pattern leakage to succeed without prior knowledge of query or data distribution for range and k-NN queries.
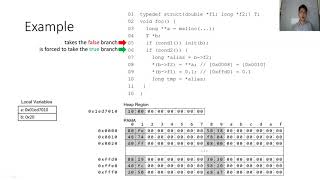
PMP - Cost-Effective Forced Execution with Probabilistic Memory Pre-planning
Explores a cost-effective forced execution technique for malware analysis, using probabilistic memory pre-planning to expose hidden behaviors and overcome self-protection mechanisms.
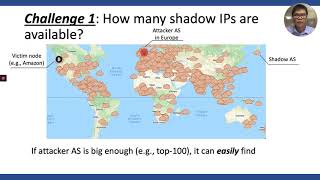
A Stealthier Partitioning Attack Against Bitcoin Peer-to-Peer Network
Explores a stealthy partitioning attack on Bitcoin's P2P network, exploiting network topology to influence node connections without routing manipulation, posing risks for cryptocurrency security.
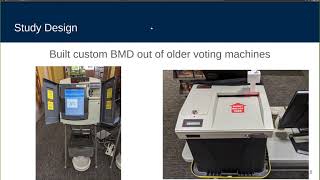
Can Voters Detect Malicious Manipulation of Ballot Marking Devices?
Explores voter detection of ballot marking device manipulation, examining review rates and effectiveness of interventions to improve verification in electronic voting systems.
Formal Modelling and Proof in the CHERI Design and Implementation Process
Explore rigorous engineering methods for developing secure processor architecture, focusing on CHERI's hardware capabilities for fine-grained memory protection and secure compartmentalization.
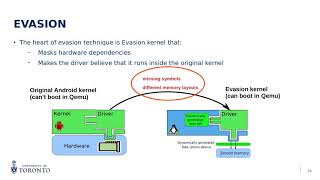
Ex-Vivo Dynamic Analysis Framework for Android Device Drivers
Framework for off-device analysis of Android drivers, enabling efficient vulnerability detection without hardware emulation. Evades dependencies, initializes drivers ex-vivo, and scales with commodity CPUs for improved security research.
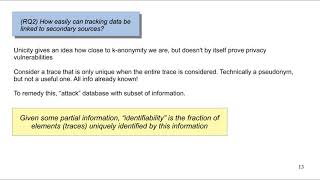
Browsing Unicity - On the Limits of Anonymizing Web Tracking Data
Explores limits of anonymizing web tracking data, revealing vulnerabilities in current methods and challenges in protecting user privacy while maintaining data utility for audience measurement.
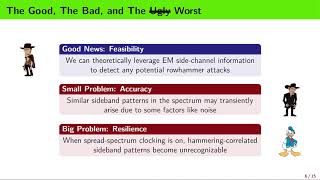
Leveraging EM Side-Channel Information to Detect Rowhammer Attacks
Explore a novel approach to detect rowhammer attacks using electromagnetic signals, overcoming challenges like spread-spectrum clocking for effective and robust defense without system performance overhead.
RetroWrite- Statically Instrumenting COTS Binaries for Fuzzing and Sanitization
Explore static instrumentation of COTS binaries for enhanced fuzzing and sanitization using RetroWrite, a framework for rewriting position-independent code.