Exploiting Android's Hardened Memory Allocator - Security Analysis and Exploitation Techniques
Discover techniques for exploiting Scudo, Android's memory allocator, through an analysis of security measures and demonstration of new exploitation methods for gaining arbitrary memory write access.
On the Effectiveness of Control-Flow Integrity in Practice - A Systematic Overview
Explore the real-world effectiveness of Control-Flow Integrity protection across Android and Windows systems, revealing critical gaps between research advances and actual deployment in practice.
3D Printer Firmware Attacks on Fused Filament Fabrication - A Systematic Analysis
Explore firmware attack vulnerabilities in 3D printing systems, examining classification methods, attack vectors, and security implications for fused filament fabrication processes.
Privacy Issues with WhatsApp E2EE in Multi-device Settings - Security Analysis
Uncover critical privacy vulnerabilities in WhatsApp's multi-device implementation, exploring how device setup information leaks affect user security and the broader implications for E2EE messaging platforms.
RIPencapsulation: Defeating IP Encapsulation on TI MSP Devices
Uncover critical security vulnerabilities in TI MSP devices' IP Encapsulation, exploring attack methods that compromise proprietary code and confidential data in IoT Trusted Execution Environments.
Not Quite Write: On the Effectiveness of Store-Only Bounds Checking
Explore the security limitations of store-only bounds checking in C/C++ code, examining bypass vulnerabilities and potential defenses for compiler-based memory safety enforcement.
Breaking Espressif's ESP32 V3: Program Counter Control with Computed Values Using Fault Injection
Discover how researchers bypassed ESP32 V3's security features through fault injection attacks, exposing vulnerabilities in Secure Boot and Flash Encryption systems with electromagnetic glitching techniques.
Achilles Heel in Secure Boot: Breaking RSA Authentication and Bitstream Recovery from Zynq-7000 SoC
Uncover critical security vulnerabilities in Zynq-7000 SoC's secure boot implementation, exploring RSA authentication bypass and practical 'Starbleed' attacks for bitstream recovery.
Amplifying Threats: The Role of Multi-Sender Coordination in SMS-Timing-Based Location Inference Attacks
Explore how multiple SMS senders can enhance location inference attacks through timing side channels, revealing improved accuracy and potential security vulnerabilities in mobile networks.
A Comprehensive Study on the Security of Arm Cortex-M Systems
Delve into a systematic analysis of Arm Cortex-M systems' security features, examining hardware limitations, software vulnerabilities, and protection mechanisms across 1,797 real-world firmware implementations.
Unleash the Power of Unreal Engine for Industrial Applications Using PLM Data
Discover how to integrate Unreal Engine with PLM systems for industrial design, featuring demos of CAD data workflows, runtime applications, and modular plugin architecture for engineering solutions.

C++'s Next Decade - The Future of Programming Language Evolution
Explore C++'s future trajectory with insights into compile-time reflection, memory safety improvements, and language simplification efforts that promise to revolutionize development practices over the next decade.
Setting Up an HTTP/3 Reverse Proxy with MITMProxy
Learn how to set up and configure an HTTP/3 reverse proxy using mitmproxy v11, covering certificate setup, ALT-SVC headers, and connection testing for modern web protocols.
Software Supply Chain Security: Understanding and Mitigating Package Ecosystem Attacks
Explore real-world software supply chain attacks, security vulnerabilities, and defense strategies through npm and NuGet examples, learning to protect projects from malicious package threats.
Application Security in the Age of AI - Understanding Modern SSDLC and AI-Enhanced Security
Explore modern application security practices enhanced by AI, covering SSDLC implementation, threat modeling, secure coding, and runtime security for comprehensive software protection.
Balancing Innovation with Responsibility - Ethics in Cloud Native Development
Explore ethical considerations in cloud native development, focusing on data privacy, environmental sustainability, and social responsibility while driving technological innovation.
Building Authorization at Scale with SpiceDB on Amazon EKS
Discover how to implement scalable authorization systems using SpiceDB within Amazon EKS environments, focusing on cloud-native security and access control mechanisms.
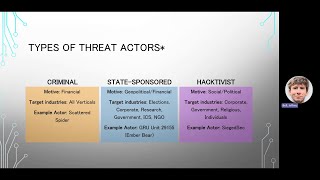
Repercussions from the Absence of Threat Actor Taxonomy - Understanding Naming Fragmentation in Cybersecurity
Explore the challenges of fragmented threat actor naming conventions and discover how MITRE ATT&CK's framework can help standardize cybersecurity threat research and tracking.
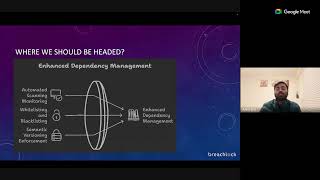
Strengthening Supply Chain Security - A DevSecOps Perspective
Explore modern supply chain security challenges and solutions through DevSecOps principles, focusing on emerging threats, operational complexities, and practical defensive strategies for today's digital landscape.
Monitoring the 2024 US Election with Maltego Monitor - Detecting Disinformation and Protecting Democratic Integrity
Discover how to detect disinformation campaigns and protect election integrity using Maltego Monitor's investigation platform for tracking false narratives and potential threats during the 2024 US elections.
Secure Flask Applications with OAuth Multi-Provider Authentication
Master OAuth authentication implementation in Flask applications with GitHub and Google provider integrations for enhanced security and streamlined user access management.