Chains of Trust in Confidential Computing
Explore Confidential Computing technologies, chains of trust, and attestation techniques for protecting data in use across various scenarios, from VMs to clusters.
Confidential Computing: Building Secure Clusters in the Cloud
Explore Confidential Computing for secure cloud workloads, including fundamentals, challenges, and deployment of confidential clusters in Azure/GCP.
Home Automation Crash Course - 2024
Explore Home Assistant's architecture, ecosystem, and capabilities for building secure, privacy-focused local home automation systems.
Data Security and Storage Hardening in Rook and Ceph
Explore Rook and Ceph's security model, examining hardening options for various threat profiles. Learn about encryption, access controls, and containerization benefits for robust data protection.
A Guide to Responsible Data Collection in Open Source
Explore best practices for ethical and effective usage data collection in open source projects, covering community, security, privacy, compliance, and governance aspects.
Learn About Linux, Containers, and Networking Through Self-Hosting
Explore self-hosting to gain hands-on experience with Linux, containers, and server operations. Set up personal cloud services for photo, music, and video sharing while maintaining data control.
APIs Without Borders - Exploring the World of Locationless API Management
Explore locationless API management for enhanced security and control across multiple clouds and clusters, leveraging Layer 7 service networks without public internet exposure.
Confidential Computing - The Minimum Developers Should Know
Explore Confidential Computing essentials: technologies, importance, and ecosystem. Learn about FHE, SMPC, TEEs, and more. Gain insights into industry collaborations and community engagement.
SpiceDB: Open Source, Hyperscale Authorization
Explore ReBAC and SpiceDB for robust, scalable authorization in cloud-native architectures. Learn to address OWASP's top security risk and implement Google-inspired solutions.
Post-Quantum Cryptography at Google
Explore Google's approach to post-quantum cryptography and its implementation strategies in this insightful talk by Sophie Schmieg at PQCrypto 2023.
Investigating Post-Quantum Cryptography: Building a PQC Decision Tree for Developers
Explore a decision tree for post-quantum cryptography, simplifying algorithm selection for quantum-ready organizations. Gain insights from experts on navigating PQC complexities.
Comparing Strategies for Quantum-Safe Cryptography Adoption in Organizations
Explore recommendations for transitioning to quantum-safe cryptography, addressing executive engagement, and developing a comprehensive plan for post-quantum cybersecurity preparedness.
Post-Quantum Crypto Integration for Enterprise Applications
Explore quantum-safe cryptography integration in enterprise applications, focusing on TLS for secure communication and hash-based signatures for software package signing.
Building Your PQC Lab - Trust But Verify Your Post-Quantum Crypto Ecosystem
Establish a Post-Quantum Crypto test environment to evaluate ecosystem options and address key challenges in PKI, Code Signing, IoT, and TLS use cases.
How to Sell Post-Quantum Readiness by Combining it with a Zero Trust Journey
Leverage zero trust journey to make a compelling case for post-quantum cryptography. Learn strategies to align PQC with organizational goals and execute a successful transition.
Machine-Checking Post-Quantum Cryptography
Explore machine-checking techniques for post-quantum cryptography, addressing challenges and ongoing projects in EasyCrypt and Jasmine within the Formosa Crypto consortium.
Unlocking the Quantum Resilient Cryptography Strategy for the Dutch Central Government
Explore the Dutch government's quantum-resilient cryptography strategy, including concrete steps and advice for organizations to mitigate quantum technology risks.
Coping with Post-Quantum Signatures in the WebPKI
Explore post-quantum signature algorithms' impact on WebPKI, current solutions, and future proposals for maintaining web security in the quantum era.
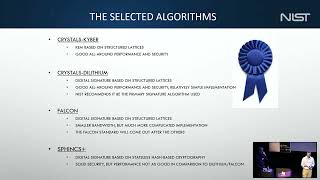
NIST Update on Post-Quantum Cryptography Standardization
Explore NIST's progress in quantum-resistant cryptography standardization, including insights on migration practices and upcoming signature scheme evaluations.
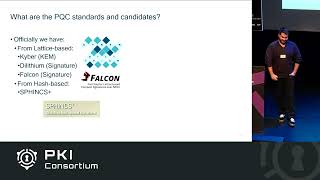
Challenges for the Post-Quantum Transition of Mobile Ecosystems
Explore challenges in integrating post-quantum cryptography into mobile ecosystems, focusing on resource constraints and the urgent need for robust data protection.
Post-Quantum Cryptography: Challenges for Embedded Applications in Automotive and IoT
Explore challenges and solutions for implementing post-quantum crypto standards in embedded devices for automotive and IoT applications.