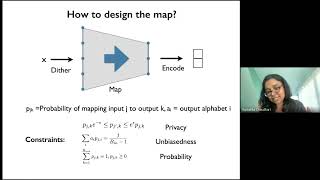
Privacy-Aware Compression for Federated Learning
Explore privacy-aware compression techniques for federated learning, addressing challenges and implementing local differential privacy mechanisms to enhance data protection in collaborative AI.
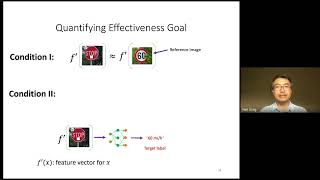
Secure Self-supervised Learning: Challenges and Solutions
Explore secure self-supervised learning techniques, focusing on backdoor attacks, data auditing, and membership inference for pre-trained encoders in machine learning.
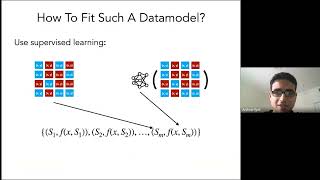
Mapping from Training Data to Predictions with Datamodels - Differential Privacy in Machine Learning
Explore datamodels in machine learning, from training data to predictions. Learn about model brittleness, data counterfactuals, and applications in ML pipelines.
Example Memorization in Learning: Batch and Streaming - Differential Privacy for ML
Explore example memorization in machine learning, covering batch and streaming scenarios, space requirements, and implications for natural models and future research directions.
Privacy-Preserving Machine Learning with Fully Homomorphic Encryption
Explore Fully Homomorphic Encryption for privacy-preserving machine learning, enabling zero-trust interactions and secure model deployment on untrusted servers.
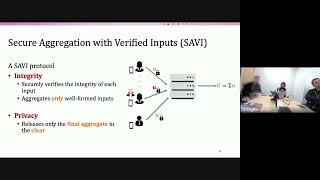
EIFFeL - Ensuring Integrity for Federated Learning
Explore secure federated learning with EIFFeL, a framework ensuring update privacy and integrity while detecting and removing malformed data to prevent model poisoning.
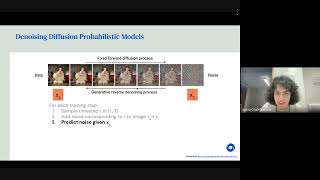
Differentially Private Diffusion Models Generate Useful Synthetic Images
Explore privacy-preserving synthetic image generation using diffusion models. Learn techniques for fine-tuning pre-trained models to achieve state-of-the-art results on CIFAR-10 and Camelyon17 datasets.
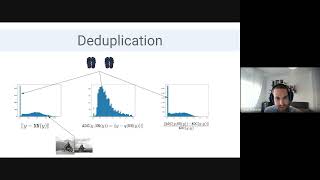
Efficient Training Image Extraction from Diffusion Models
Explore efficient techniques for extracting training images from diffusion models, addressing privacy concerns and copyright issues while uncovering insights into image duplication and template copying.
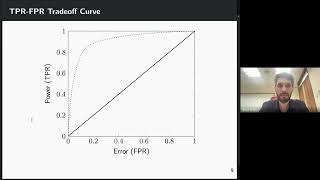
Low Cost High Power Membership Inference Attacks
Explore robust, efficient membership inference attacks for machine learning privacy risk assessment. Learn to differentiate population and training data with minimal computational overhead.
The Data Minimization Principle in Machine Learning
Explore data minimization in machine learning, its challenges, and practical implementations. Examine optimization-based formalization and applications in high-stakes domains, revealing insights on privacy and efficiency.

Privacy Preserving Machine Learning with Fully Homomorphic Encryption
Explore Fully Homomorphic Encryption's role in advancing secure, privacy-preserving machine learning applications, focusing on Concrete ML and its integration with other technologies.
Supply Chain Security with Go
Learn Go-specific supply chain security practices to protect your software from vulnerabilities and attacks.
A Statistical Journey through Trustworthy AI
Explore statistical perspectives on privacy, robustness, and fairness in AI, focusing on machine un-learning, adversarial robustness, and fair Bayes-optimal classifiers.
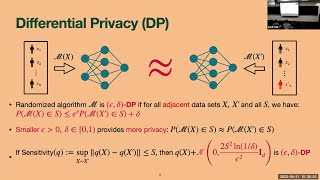
Private Stochastic Optimization with Large Worst-Case Lipschitz Parameter
Explore differentially private stochastic optimization techniques for loss functions with large worst-case Lipschitz parameters, addressing outliers and heavy-tailed data for improved excess risk bounds.
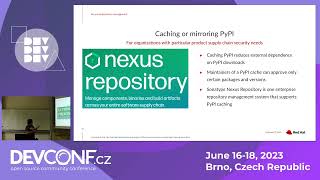
Secure Python Development: Tips, Tricks, and Tools
Explore Python-specific security challenges and solutions, including package management, SAST, and best practices for DevOps environments.
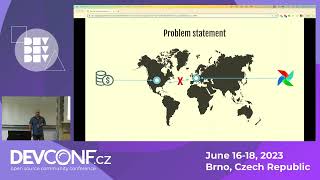
Data Governance with Airflow and ECS Anywhere
Explore data governance compliance using Airflow and AWS ECS Anywhere for EU companies processing US data, ensuring legal adherence while maintaining efficient ETL processes.
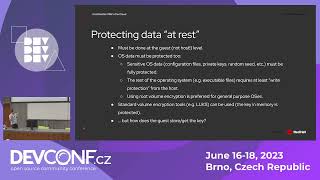
Confidential VMs in the Cloud
Explore confidential instance types in Azure and GCP, focusing on security guarantees, Linux OS requirements, and implementation in Fedora and RHEL distributions.
Powering AI Capabilities with API Management
Explore integrating Apache APISIX API Gateway with OpenAI API for scalable, performant, and secure AI applications. Learn proxy caching and security features.
Confidential Computing: From Host to Workload
Explore confidential computing technologies, from machine setup to running secure containerized workloads, covering architectures, workload preparation, and security considerations.
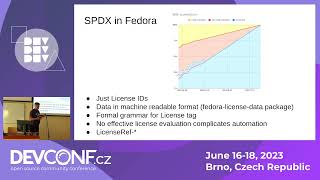
Software Bill of Materials (SBoM) for Dummies
Explore Software Bill of Materials (SBoM), its importance, and implementation in Fedora. Learn about US government mandates, hidden pitfalls, and the SPDX migration.
FIDO2 Authentication for Centrally Managed Users
Explore FIDO2/WebAuthn authentication for centralized identity management in POSIX systems, enhancing security while maintaining strict access control for organizations.