Exploring Web Applications Through Their JavaScript - Uncovering Hidden Information
Descubre cómo analizar el código JavaScript de sitios web para encontrar información valiosa como API Keys, endpoints internos y usuarios, mejorando tus habilidades en seguridad web.
Mi Camino a los 2500 Puntos de Reputación en HackerOne
Experiencia en bug bounty: desde los inicios hasta 2500 puntos en HackerOne. Consejos sobre reportes, cálculo de riesgos y colaboración en la comunidad de cazadores de vulnerabilidades.
Button Combo Crash: Analyzing a POS Device Without Disassembly
Análisis de vulnerabilidades en un posnet sin abrirlo, explorando combinaciones de botones para descubrir fallos de seguridad y posibles explotaciones en dispositivos de pago.
Mobile Hacking 101 - A Cross-Platform Audit Journey
Descubre técnicas y herramientas para auditar la seguridad de aplicaciones móviles multiplataforma, identificando riesgos y vulnerabilidades en prácticas de programación deficientes.

100 Vulnerabilities in 30 Days - Hacking the World's Largest Insurance Company
Descubre cómo un equipo de seguridad identificó 100 vulnerabilidades en 30 días en la mayor aseguradora mundial. Aprende métodos, herramientas y lecciones de este impresionante logro en bug bounty.
Rompiendo los Miedos - Mi Camino Hacia la Crítica y el Bug Bounty
Descubre cómo superar miedos en bug bounty y aprende sobre un reporte público de vulnerabilidad IDOR en Reddit que permitía cambiar enlaces de usuarios sin su conocimiento.

Is What We See Real? - Adapting to Technological Reality
Изследване на въздействието на технологиите върху възприятието на реалността и способността ни да разграничаваме истинското от изкуственото в съвременния свят.
Creating a Password Generator Using Python
Learn to create a secure password generator in Python, enhancing your coding skills while exploring practical applications for everyday cybersecurity needs.
Hosting Tutorial: Deploy NodeJS Apps in Production on Linux VPS - Tutorial 97
Learn to deploy NodeJs applications on a Linux VPS for production environments. Gain practical skills in server setup, configuration, and best practices for hosting web applications securely and efficiently.

Hosting Multiple Websites on One Single Hosting Server - Tutorial 96
Learn to host multiple websites on a single server efficiently. Discover techniques for optimizing server resources, managing domains, and configuring virtual hosts for improved web development workflow.
Implementing Google reCAPTCHA in Python Django
Learn to implement Google reCAPTCHA in Python Django to enhance website security and prevent automated bot submissions, with step-by-step guidance and practical demonstrations.

Saving PHP Website from a Potential XSS Attack - Tutorial 64
Learn to protect your PHP website from XSS attacks. Discover techniques to sanitize user input, validate data, and implement security measures to prevent cross-site scripting vulnerabilities.

Django 3 Blog: Authentication and Authorization Tutorial - Part 85
Aprenda a implementar autenticação e autorização em um blog Django 3. Tutorial em hindi sobre gerenciamento de usuários e permissões em aplicações web Python.
Operation Triangulation: Uncovering a Sophisticated Zero-Click Attack on iPhones - French Translation
Découverte et analyse d'une attaque zero-click sophistiquée ciblant les iPhones, exploitant quatre vulnérabilités zero-day et déployant un logiciel espion avancé. Présentation détaillée de l'opération Triangulation.
Artificial Intelligence - Risks and Challenges
Exploració dels avenços, riscos i desafiaments ètics de la intel·ligència artificial, destacant la importància del compromís ètic per garantir l'equitat en el seu desenvolupament i aplicació.
Der sehende Stein der Polizeibehörden - Palantir Gotham in German Law Enforcement
Kritische Analyse des Einsatzes von Palantir Gotham bei deutschen Polizeibehörden: rechtliche, technische und ethische Aspekte sowie Risiken und Einschränkungen der umstrittenen Datenanalyse-Software.
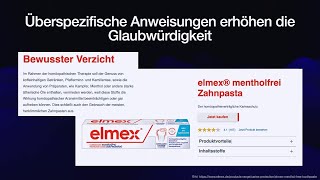
Cyber-Astrology and AI Karma Training
Humorvolle Präsentation über esoterische Digitalisierungsdienstleistungen, die Techniken unseriöser Akteure aufdeckt und kritisch beleuchtet. Vermittelt Medienkompetenz durch satirische "Fortbildung".
Four-Year Review of the Chaos Computer Club (CCC) - 37C3
Umfassender Rückblick auf vier Jahre CCC-Aktivitäten: von digitalen Hausbesuchen über Hacker-Events bis zu Verfassungsgerichtsgutachten. Einblicke in die Entwicklungen der Nautosphäre und Ausblick auf 2024.
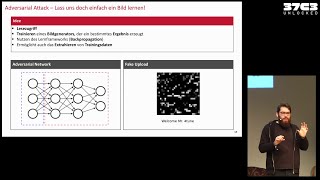
Hacking Neural Networks - Introduction and Current Techniques
Einführung in Angriffsmethoden auf neuronale Netze: Funktionsweise, Schwachstellen und Verteidigungsstrategien. Praxisnahe Beispiele verdeutlichen Risiken und Limitierungen moderner KI-Systeme.
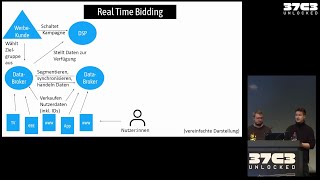
Die Akte Xandr - Ein tiefer Blick in den Abgrund der Datenindustrie
Enthüllung der invasiven Praktiken der Werbeindustrie: Analyse des Xandr-Datenlecks, Einblicke in Zielgruppenkategorisierung und Diskussion ethischer Implikationen sowie möglicher Alternativen zur Datenüberwachung.
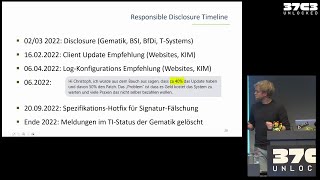
KIM: Chaos in the Medical Telematics Infrastructure - Security Analysis
Analyse der Sicherheit von KIM, dem E-Mail-System im deutschen Gesundheitswesen. Aufdeckung von Schwachstellen in Schlüsselausgabe, Software und Nutzerfreundlichkeit trotz theoretisch sicherer Kryptographie.