Port Knocking and Scanner Detection in MikroTik Firewall - Episode 3
Master essential MikroTik RouterOS security features - implement Port Knocking for controlled access and Scanner Detection to identify potential network threats and vulnerabilities.
DNS over HTTPS (DoH) on MikroTik - Complete Implementation Lab
Master DNS over HTTPS implementation on MikroTik routers with hands-on configuration steps, practical lab exercises, and complete scripts for enhanced browsing privacy and security.
Blocking DNS Flood Attacks on MikroTik - Network Security Guide
Master DNS flood attack protection on MikroTik routers through practical demonstrations and implementation strategies to safeguard networks from DDoS threats and maintain optimal performance.
MACsec on MikroTik - Configuring Hop-by-Hop Layer 2 Encryption
Master Layer 2 network security by implementing MACsec protocol on MikroTik devices, featuring step-by-step configuration and practical demonstrations of hop-by-hop encryption for enhanced data protection.
Risk-Based Vulnerability Management for Cloud Networks - A Proof of Concept on Vulnerability Prioritization Model
Explore an AI-powered vulnerability prioritization model for cloud networks that reduces remediation workload by 3x through intelligent risk assessment and threat analysis.
Making the Edge Tamper-Proof: Security Challenges and Solutions in Edge Computing
Discover essential security practices for edge computing deployments, focusing on firmware protection, supply chain security, and tamper-proofing strategies using EVE-OS in remote environments.
Protect Your Application with Zero Trust Superpowers Using OpenZiti
Discover how to embed zero trust security directly into applications using OpenZiti's SDK, moving beyond traditional network protection to create more secure, powerful software solutions.
ZT&T Intent-Based Networking and Blockchain-Driven Approach for Zero Trust and Touch
Explore Zero Trust Networking through an innovative blockchain-driven approach, focusing on secure service policies, NFT-based access tokens, and practical implementation in network infrastructure.
Efficiently Delivering Open Source Code with OpenSSF Gold-Standard Quality Measurements Using Groovy-Spock
Discover how to achieve OpenSSF Gold Standard certification using Groovy-Spock framework for efficient unit testing and quality assurance in open source software development.
ONAP's Recipe for Managing CVEs and Securing Open Source Software
Discover ONAP's effective strategies for managing CVEs, securing open-source dependencies, and implementing automated vulnerability management processes in software development.
Common Kubernetes Attack Vectors and How to Secure Your Cluster
Discover essential security strategies for Kubernetes deployments, covering authentication, network policies, pod security, and threat detection techniques for robust cluster protection.
Reducing Factory Downtime - Edge Technology in Manufacturing
Discover how to minimize factory downtime using edge computing solutions that enable quick equipment replacement and remote configuration without specialized IT staff on-site.
Zero Trust and Runtime Security for Edge - Implementing Multi-Dimensional Protection
Discover how to implement Zero Trust security across application, network, and data dimensions for edge computing, addressing runtime challenges and automation requirements for effective protection.
How to Use Open Source and Standards to Improve Mutual Trust in the Network Ecosystem
Discover how to build secure and trustworthy network infrastructure using open-source methods and standards, focusing on zero-trust frameworks and software supply chain security.
Realizing ZTNA with Open Source Projects - Building Secure Enterprise Access Solutions
Discover how to implement Zero Trust Network Access using open-source tools like ISTIO, Keycloak, and Kubernetes, with practical insights on automating secure enterprise application access.
Hands-on Edge Orchestration: Techniques for Enterprise-Scale Deployment Using EVE OS
Master edge orchestration techniques for secure, scalable deployments using EVE OS, covering security, network resilience, and real-world applications from wind turbines to smart buildings.
Reelin' in Unwanted Traffic: Analyzing and Addressing IoT Attack Traffic
Explore insights from a global IoT honeyfarm project analyzing malicious traffic patterns, attack behaviors, and potential solutions for reducing unwanted Internet traffic while maintaining open networks.
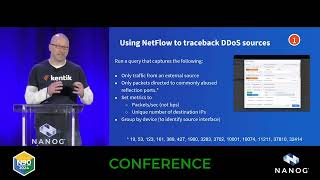
Using NetFlow to Fight DDoS Attacks at the Source
Discover how NetFlow analysis platforms can identify and stop spoofed traffic driving DDoS attacks, ensuring better network security and protection against cyber threats.
Open Source Risk Management - Understanding User Perspectives on Security and Quality
Discover key insights from network administrators on open source security priorities and learn how their perspectives differ from developers' assumptions in quality control.
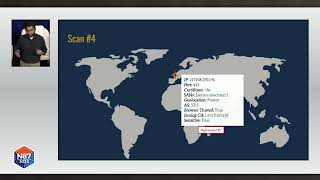
Retroactive Identification of Targeted Domain Hijacks - DNS Infrastructure Security
Explore advanced techniques for identifying and protecting against sophisticated domain hijacks that bypass traditional DNS security measures, with insights into nation-state tactics and infrastructure protection.
Evaluating the Effects of a Global DDoS-for-Hire Service Takedown
Explore the impact of coordinated global DDoS-for-hire service takedowns through statistical analysis and real-world data, examining criminal ecosystems and international enforcement efforts.