Setting Up STM32MP1 as AWS Greengrass V2 Core Device
Master the configuration of STM32MP135 DK for AWS Greengrass V2, including automated IoT setup, IAM roles, PKCS#11 key management, and secure service deployment for IoT solutions.
An Evaluative Case Study of Shadow IT Mindsets Among Corporate Employees
Explore the complex dynamics of shadow IT in corporate environments through research findings on employee mindsets, risk awareness, and behavioral patterns in unofficial technology adoption.
Consistent Diffusion Meets Tweedie - Training Exact Ambient Diffusion Models with Noisy Data
Explore groundbreaking techniques for training diffusion models with corrupted data, using Tweedie's formula to generate high-quality samples while reducing memorization and privacy concerns.
No Requests, No Limits, No Service - How to Bring Kubernetes to a Grinding Halt
Dive into a real-world Kubernetes incident analysis, exploring how thousands of test environment pods caused cluster failure and learn valuable lessons for managing internal build platforms.
Auditing Kubernetes Users: Tracking Security Holes
Discover how to implement effective Kubernetes auditing mechanisms, track user activities, and detect security vulnerabilities through RBAC analysis and audit API implementation.
Defending AI on Kubernetes - A Red Team Security Playbook
Explore offensive security strategies and defense mechanisms for AI systems on Kubernetes, focusing on vulnerability assessment and protective measures from an attacker's viewpoint.
Safely Extending the Kubernetes Scheduler with WebAssembly - A Tale of Two Plugins
Discover how WebAssembly enhances Kubernetes scheduler extensibility, exploring implementation challenges, architectural benefits, and practical applications for custom scheduling solutions.
Watching the Watchers - The Hidden Risks of Container Scanning Tools
Explore critical security risks and mitigation strategies for container vulnerability scanning tools, focusing on system protection, secure configurations, and defense-in-depth approaches.
IBAC for Developers - Automating Istio Authorization Policies Using Envoy Metrics With a Declarative Approach
Master Istio Authorization Policies automation through Envoy metrics, implementing identity-based access control with declarative methods for enhanced cloud security.
5 Essential Ansible Security Features for IT Automation
Discover how to enhance IT infrastructure security through 5 essential Ansible features, including SSH configuration, user management, vault encryption, firewall setup, and package updates.
Secure and Encrypted Boot in Zephyr RTOS Using Hardware Keys and TrustZone
Explore secure booting implementation in Zephyr RTOS using MCUboot, hardware keys, and encryption features like HAB and TF-M for enhanced embedded system security and tamper protection.
Navigating the Quantum Readiness Journey - Open-Source Cryptography, PKI and Signing Tools
Explore post-quantum cryptography standards and their implementation in open-source tools, focusing on IoT, container security, and software supply chain protection through quantum-resistant solutions.
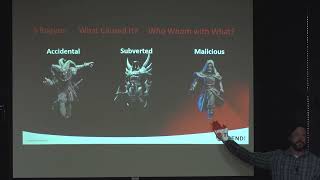
Three Categories of Rogue AI and How to Mitigate Risk
Discover essential strategies for identifying and defending against three types of rogue AI behaviors, including practical implementation of OWASP guidelines and Zero Trust frameworks for secure AI deployment.
Scanning Infrastructure as Code for Security Vulnerabilities with Terraform
Master infrastructure security scanning with Checkov OSS, focusing on Terraform vulnerabilities and exploring policy-as-code solutions like Bridgecrew and Hashicorp Sentinel for enhanced cloud security.
AI Under the Hood: Unmasking Hidden Threats
Explore a comprehensive analysis of AI threat modeling frameworks, examining safety protocols and risk assessment methods for AI/ML applications while learning to identify and address potential vulnerabilities.
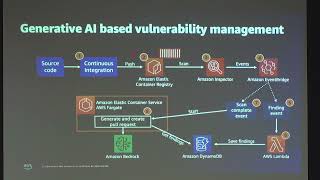
Applying Generative AI to Container CVE Remediation in CI Pipelines
Discover how to leverage generative AI for automating container vulnerability remediation in CI pipelines, with practical demonstrations and implementable solutions for efficient security management.
How to Shift-Left and Find Critical Authorization Vulnerabilities Throughout Your CI/CD Pipeline
Discover effective strategies for detecting and preventing authorization vulnerabilities in DevSecOps pipelines, focusing on early identification and remediation across multiple application roles and APIs.
Safeguarding Machine Learning Systems - A Comprehensive Security Plan
Discover a holistic security framework for ML systems, covering data protection, model fortification, platform security, compliance measures, and human-centric safeguards for robust AI deployment.
Strengthening Defenses Against CI/CD Security Threats - Understanding and Mitigating Pipeline Vulnerabilities
Dive into essential CI/CD pipeline security, exploring OWASP's top risks, attack methodologies, and practical defense strategies to fortify your development infrastructure.

How AI Could Hack Democracy
Explore law professor Lawrence Lessig's critical analysis of AI's current impact on democratic systems and the urgent need for attention to these challenges before reaching AGI.
Cilium, eBPF, and WireGuard: Taming the Network Encryption Performance Gap
Explore network encryption optimization using Cilium, eBPF, and WireGuard, focusing on performance impacts and solutions for secure data transit while minimizing operational overhead.