Developing Secure Software with GitHub - Automated Security Checks and Tools
Learn to leverage GitHub for automated security checks, including static application security testing and software composition analysis, to enhance your application's security posture with minimal effort.
Cyber Threats Facing Small Utilities and the Dragos Community Defense Program
Explore cyber threats to small utilities and learn about Dragos' free resources for enhancing OT cybersecurity. Gain insights on threat landscapes, defense strategies, and community-driven protection initiatives.
Hacker Panel - What Hackers Can Tell You About AI Security
Gain insights from top hackers on AI security vulnerabilities, threats, and best practices to protect AI systems from malicious attacks.
Navigating SEC Rules for Enhanced Cybersecurity in IT and OT Environments
Explore SEC cybersecurity rules' impact on IT and OT environments, addressing unique challenges, materiality concepts, and collaborative approaches for comprehensive risk management and regulatory compliance.
The Art of Bypassing Web Application Firewalls - Live Demos
Explore hands-on techniques for bypassing modern web application firewalls. Learn to customize methods and payloads through practical labs, enhancing your skills in WAF evasion and web security.
.NET in a Box - Containerizing .NET Applications
Explore containerizing .NET applications for scalability and efficiency. Learn core concepts, performance optimization, security measures, and deployment strategies for future-ready microservices and cloud-native solutions.
Securing Video Content with Authentication Using Mux
Learn to implement authenticated video access using Mux. Covers setup, signed URLs, JWT generation, user experience, DRM, and debugging for secure video content delivery.
CompTIA Security+ Exam Practice Questions - Part 2
Comprehensive practice session for CompTIA Security+ exam, covering social engineering, cryptography, authentication, cloud security, and device vulnerabilities with detailed explanations and strategies.
Algorithmic Injustice and the Algorithmic Accountability Act
Explore algorithmic bias in criminal justice and everyday settings, examining the Algorithmic Accountability Act's impact on shopping and social media platforms.
Legal Exposure from Running Your Own Mastodon Server/Instance
Explore legal obligations and risks of running a Mastodon server, comparing decentralized moderation to centralized social media platforms.
Who Wants to Be A Regulator - The IoT Security Game Show
Interactive game show exploring IoT security regulations, featuring expert panelists discussing challenges and potential solutions in a fun, engaging format.
Baby Got Hack Back
Explore legal and ethical aspects of cybersecurity, including international laws, information sharing, and active defense strategies. Gain insights on balancing security with policy considerations.
How Embracing Social Media Helped Me Stop the Hackers, Save the World and Get the Girl
Discover how leveraging social media can enhance cybersecurity efforts, solve global challenges, and improve personal relationships through real-world experiences and practical insights.
How to Survive the Hardware Assisted Control-Flow Integrity Enforcement
Deep dive into Intel CET on Windows 10, exploring control-flow integrity enforcement and potential vulnerabilities. Includes demonstrations of attacks and ways to circumvent CET protection.
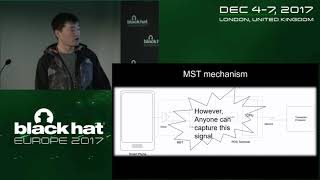
How Samsung Secures Your Wallet and How to Break It
Demystifying SamsungPay's implementation and security mechanisms, with insights on bypassing analysis obstacles. Explore the intricacies of this mobile payment service's architecture and potential vulnerabilities.
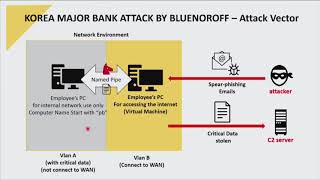
Nation-State Moneymule's Hunting Season – APT Attacks Targeting Financial Institutions
Unveiling recent operations by North Korean APT groups Lazarus, Bluenoroff, and Andariel, focusing on cyber heists and attacks targeting financial institutions.
Diplomacy and Combating Evolving International Cyber Threats
Explore the evolving landscape of international cyber diplomacy, focusing on efforts to counter threats, promote norms, and address challenges in cyberspace from a policy perspective.
Stepping Up Our Game - Re-focusing the Security Community on Defense and Making Security Work for Everyone
Facebook CSO Alex Stamos discusses the evolving role of cybersecurity, emphasizing the need for a renewed focus on defense and making security accessible to all in an era of heightened digital risks and societal impact.
Domo Arigato, Mr. Roboto - Security Robots a la Unit-Testing
Explore security unit testing for custom code, focusing on inoculating applications, identifying endpoints, and addressing common vulnerabilities through automated testing frameworks.

Pre-Stuxnet, Post-Stuxnet - Everything Has Changed, Nothing Has Changed
Explore the impact of Stuxnet on cybersecurity, revealing vulnerabilities in critical infrastructure and the shift in focus from IT networks to operational systems and national security concerns.
RFID Security Research - Early Insights and Implications
Early RFID security research by Adam Laurie, exploring vulnerabilities in RFID passports and predicting the need for RFID-blocking wallets. A pioneering look at RFID technology's security implications.