Improving eBPF Complexity with a Hardware-backed Isolation Environment
Explore hardware-backed isolation for eBPF, enhancing complexity management and security in Linux kernel development.
Snapshot Fuzzing with WTF Fuzzer - Techniques and Implementation
Master snapshot fuzzing with WTF Fuzzer. Configure Hyper-V, use Windbg and Bdump.js for snapshotting, develop harnesses, and fuzz C programs. Enhance your software security skills through hands-on practice.
Under-approximation for Scalable Bug Detection
Explore under-approximation techniques for efficient bug detection in large codebases. Learn about Incorrectness Logic, ISL, and Pulse-X for scalable, compositional program analysis and memory safety error detection.
What is a WebAssembly Component and Why - WAW'24
Explore the WebAssembly Component Model proposal, its motivations, technical design, and upcoming releases for cross-language, portable module development.
WALI: A Thin Linux Kernel Interface for WebAssembly
Explore WALI, a thin layer enabling WebAssembly to interact seamlessly with Linux systems, enhancing application portability and security while leveraging existing compiler backends.
The State of Morello and CHERI
Explore the current status and advancements of Morello and CHERI technologies in computer architecture and security.
Object Capabilities - Principles and Applications
Explore object capabilities in programming languages, focusing on security, encapsulation, and access control mechanisms for robust software design.
Lineage: A Data-Flow Analysis for Erlang
Explore a novel data-flow analysis for Erlang, producing over-approximating dataflow graphs for efficient taint checking in large-scale codebases.
Flux: Refinement Types for Rust
Explore refinement types for Rust with Flux, enhancing code safety and expressiveness in systems programming.
How to Read a PL-Security Paper
Explore techniques for understanding PL-security papers, including threat models, attacker concepts, and contributions to programming languages. Gain insights for PL generalists approaching security topics.
The Mess We're Still In - Navigating Complex Systems and Security Risks
Explore the ongoing challenges in software development, focusing on security risks, system complexity, and innovative solutions for building resilient applications.
Programming for the Planet - Functional Programming for Environmental Analysis
Explore functional programming's role in building resilient systems for climate analysis, addressing global crises through data-driven conservation and policy decisions.
Playing Video Games One Frame at a Time
Explore game automation techniques using C++, from built-in tool support to code injection. Learn to enhance gameplay and overcome challenges through programming.
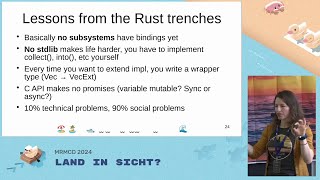
Rust in the Linux Kernel - A Status Check
Explore Rust's integration into the Linux Kernel, examining current capabilities, limitations, and interactions with existing C code. Gain insights into the progress of Rust adoption.
Integrating Cloud Native Security into the SRE Culture
Explore integrating cloud native security into SRE culture, enhancing DevOps practices with robust security measures for modern infrastructure and applications.
Why We Need to Adopt Static Analysis in Dependency Tools
Explore the importance of static analysis in dependency tools for enhanced security and efficiency in software development.
Sustainable Open Source - Ensuring Long-Term Viability
Explore sustainable open source practices and their impact on DevSecOps. Learn strategies for maintaining long-term project viability and community engagement.
Cloud Metadata Abuse - Threat Actors and Security Implications
Explore cloud metadata abuse techniques and learn defensive strategies to protect your cloud infrastructure from potential threats.
Observability: One of the Strongest Muscles for SRE
Explore how observability enhances SRE practices, improving system reliability and performance through effective monitoring and data analysis techniques.
SBB - Secure Building Blocks for IoT Systems in Rust - Conf42 Rustlang 2023
Explore Rust's advantages for embedded systems, IoT security, and functional safety. Learn about digital signatures and RustBoot architecture for secure IoT development.
Leveraging Blockchain for Secure and Immutable Firmware Updates
Explore blockchain-based secure firmware updates for IoT devices. Learn implementation strategies, smart contracts, and resilience against attacks through expert insights and a practical demo.