Empirical Measurement of Security and Privacy in Technology Systems - Conversations with Dr. Damon McCoy
Explore cutting-edge cybersecurity research, focusing on empirical measurement of tech systems' security and privacy, and their societal impact. Gain insights from Dr. McCoy's work in automotive security.
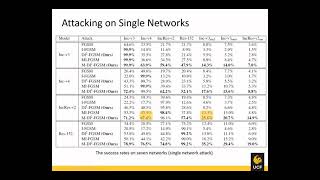
Improving Transferability of Adversarial Examples with Input Diversity - CAP6412 Spring 2021
Explore techniques to enhance adversarial example transferability using input diversity, including FGSM family methods and ensemble network attacks.
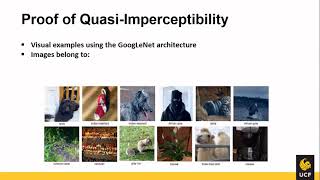
Universal Adversarial Perturbations in Machine Learning - Spring 2021
Explore universal adversarial perturbations in machine learning, covering definitions, contributions, experiments, and cross-model universality.
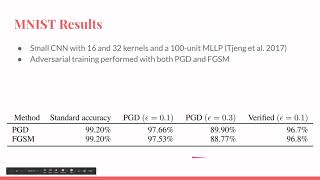
Fast Is Better Than Free: Revisiting Adversarial Training - CAP6412 Spring 2021
Explore adversarial training techniques, comparing PGD with newer methods. Learn about technical contributions, experimental results, and implications for machine learning security.
How Can I Explain This to You? An Empirical Study of Deep Neural Net Explanation Methods - Spring 2021
Empirical study comparing deep neural network explanation methods, examining usability, stability, and privacy risks across various visual explanation frameworks.
Introduction to Convolutional Neural Networks - Part 1 - Lecture 6
Comprehensive introduction to Convolutional Neural Networks, covering history, architecture, key concepts, and applications in image processing and beyond.
Linux for Beginners
Master Linux command line, file management, system administration, and networking essentials. Gain practical skills in text editing, process management, and web server configuration.
Exploiting the Power of WebAssembly on the Server Side with Chicory
Explore the potential of WebAssembly on the server side with Chicory, a pure Java interpreter for Wasm. Discover how this technology enables execution of code written in various languages while providing strong sandboxing and safety guarantees. Learn abo…
Report Writing Explained for Bug Bounty Submissions
Learn essential report writing skills for bug bounty submissions in this 20-minute video featuring Katie Paxton-Fear and Codingo from Bugcrowd. Discover top tips for crafting clear, impactful reports that triagers and customers can easily understand. Exp…
Evaluating Open-Source Local LLMs: A Comparative Analysis with Proprietary Giants for Developer Applications
Explore the world of open-source local large language models (LLMs) in this 40-minute conference talk from Devoxx. Dive into a comparative analysis between these models and proprietary giants, focusing on their performance, flexibility, and applicability…
A Passwordless Future - Passkeys for Java Developers
Explore the revolutionary world of passkeys in this 52-minute conference talk from Devoxx. Dive deep into the Web Authentication standard and discover how passkeys are transforming authentication methods for enhanced security. Learn about the core concep…
Securing LLM-Powered Applications - Overcoming Security and Privacy Challenges
Explore the security and privacy challenges of LLM-powered applications in this 51-minute conference talk from Devoxx. Delve into common issues like prompt injection, key leakage, and misuse of private customer data for model training. Gain insights on l…
HTTP/3 and QUIC: Who, What, Where, When, and Why - Understanding the New Protocols
Explore the revolutionary HTTP/3 and QUIC protocols in this informative conference talk. Delve into the historical context and understand the driving forces behind these new technologies that now account for over 25% of global Internet traffic. Examine t…
Words as Weapons - The Dark Arts of Prompt Engineering
Explore the dark arts of Prompt Engineering in this eye-opening 43-minute conference talk from Devoxx. Delve into the evolving landscape of AI integration in organizations, focusing on the risks associated with Large Language Models (LLMs) and their appl…
Privacy in Practice with Smart Pseudonymization - Lessons from the Belgian Public Sector
Explore the evolution and implementation of privacy protection technologies in this 50-minute conference talk from Devoxx. Trace the history of identity concealment from ancient physical masks to modern digital pseudonymization techniques. Discover how t…
Introduction to Quarkus Security
Explore Quarkus and its Security Architecture in this 52-minute conference talk from Devoxx. Discover how Quarkus solves real-world security challenges while prioritizing Developer Joy. Learn to develop and test OpenID Connect-secured services in Dev mod…
Angular Route Guards - Enhancing User Experience and Security
Explore Angular Route Guards to control access, enhance user experience, and bolster security. Uncover differences between guard types, learn about 'canMatch', and optimize your Angular applications.
Demystifying Proxy Execution
Explore proxy execution in Linux systems, understanding its mechanisms, challenges, and potential solutions for improved performance and security.
Mastering OSS Security Development with Linux Foundation Education
Develop secure open source software skills, from foundational to advanced, with expert-led training and certifications. Gain hands-on experience for real-world OSS security.
Security Updates in Gradio 5
Explore key security enhancements in Gradio 5, addressing issues identified in an independent audit to strengthen the platform's integrity and user protection.
World-leaders in Cryptography - Kurt Rohloff
Explore homomorphic encryption with Kurt Rohloff, co-founder of PALISADE and OpenFHE libraries, and CTO of Duality Technologies. Gain insights into cutting-edge cryptographic advancements.