Live Bug Bounty Recon Session on Yahoo - Censys, Altdns, Amass
Live bug bounty recon session exploring Yahoo using tools like censys, altdns, and amass. Learn techniques for subdomain discovery, directory brute forcing, and more with guest @infosec_au.
Live Bug Bounty Recon Session on Yahoo - Amass, crt.sh, and Dirsearch
Live bug bounty recon session demonstrating advanced techniques for discovering vulnerabilities on Yahoo, featuring tools like Amass, crt.sh, and dirsearch, with guest expert @TheDawgyg.
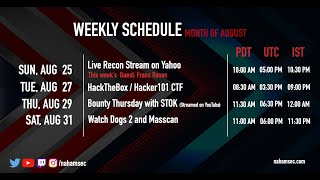
Live Bug Bounty Recon Session - August 18, 2019
Live bug bounty recon session covering techniques like JSParser, directory brute forcing, crt.sh, and API fuzzing. Expert guests share insights on effective reconnaissance strategies for ethical hacking.

What is Server-Side Request Forgery - SSRF?
Explore Server-Side Request Forgery (SSRF): its definition, potential impacts, and importance in web security. Learn to identify and mitigate this critical vulnerability.
Cloud Hacking- Web3.0 Approach
Explore innovative cloud hacking techniques using a Web3.0 approach. Learn cutting-edge strategies for offensive security, red teaming, and bug bounty hunting in modern cloud environments.
Learn Cybersecurity and Hacking Through CTF
Explore cybersecurity and hacking skills through hands-on Capture The Flag challenges. Gain practical experience in offensive security techniques and ethical hacking practices.
Does Cybersecurity Require Programming?
Explore the role of programming in cybersecurity with insights from industry experts. Gain clarity on essential skills for success in hacking and information security.
The 3 Tools You Need - How To Bug Bounty
Discover essential tools for bug bounty hunting: asset discovery, content discovery, and proxy tools. Learn about brute force techniques and Burp Suite for effective vulnerability detection.
What Should You Do After Recon?
Strategies for effective bug hunting after reconnaissance: prioritizing targets, analyzing attack surfaces, and tailoring your approach for maximum impact in bug bounty programs.
Live Recon on Rockstar Games - Vulnerability Testing Methodology
zseano demonstrates vulnerability testing methodologies on Rockstar Games, showcasing tools like Burp Suite and techniques for identifying XSS and open redirects in this live recon session.
Recon Methodology Using SecurityTrails, FDNS, Whoxy, and More
Explore codingo_'s unique recon methodology for ethical hacking, featuring tools like SecurityTrails, FDNS, and Whoxy to enhance your cybersecurity skills and bug bounty hunting techniques.
Live Recon and Distributed Recon Automation Using Axiom
Explore live recon and distributed recon automation using Axiom with @pry0cc. Learn advanced techniques for efficient and effective bug bounty hunting and cybersecurity research.

Live Recon and Automation on Shopify's Bug Bounty Program - TomNomNom
Explore live recon and automation techniques for Shopify's bug bounty program with expert insights, enhancing your skills in identifying vulnerabilities and maximizing bounty rewards.
Live Recon and Google Dorking on the Department of Defense Vulnerability Disclosure Program
Explore live reconnaissance and Google dorking techniques on the Department of Defense's Vulnerability Disclosure Program, featuring insights from @thedawgyg.
Live Recon on Snapchat - Demonstration of Amass, FFUF, and SecurityTrails
Explore live reconnaissance techniques on Snapchat using tools like amass, FFUF, and SecurityTrails in this hands-on demonstration with @ITSecurityGuard.
Bug Bounty Seminar with Verizon Media's Paranoids
Explore bug bounty hunting with Verizon Media's Paranoids team. Learn strategies, techniques, and insights to enhance your cybersecurity skills and potentially earn rewards.
Getting Into Bug Bounty - Recon, Automation, and Triage
Explore bug bounty hunting with insights on reconnaissance, automation, and triage from @ITSecurityguard. Learn key strategies for success in this cybersecurity field.
Bug Bounties, Pulse Secure Research, and Hacking the US Department of Defense - Interview with Alyssa Herrera
Insightful discussion on bug bounties, cybersecurity research, and ethical hacking experiences, featuring expert insights from Alyssa Herrera on various high-profile targets.
Learning JavaScript for Hacking - Interview with Filedescriptor
Explore JavaScript for hacking, reconless techniques, and Twitter vulnerabilities with expert insights on enhancing cybersecurity skills and ethical hacking practices.
Security Training at the Harbor - Running CTFs with Docker
Learn to run Capture The Flag (CTF) competitions using Docker, enhancing cybersecurity skills through hands-on challenges and containerized environments.
Popping a Shell with SMB Relay and Empire
Learn to exploit SMB Relay attacks and gain remote access using Empire, enhancing your penetration testing skills and understanding of network security vulnerabilities.