
The Bang! - When Bad Things Happen to Your Data - Preventing and Remediating Data Security Breaches
探索数据安全策略:通过90年代风格游戏场景,学习使用Kanister、OPA和Prometheus来预防和应对数据安全事件,构建更强大的基础设施。
Complex Bank Card Smishing Attack Exploiting Posta Romana's Image - DefCamp Cluj-Napoca 2024
Análisis detallado de un sofisticado ataque de smishing bancario que aprovecha la imagen de Posta Romana, revelando técnicas y contramedidas para mejorar la seguridad cibernética.
Terraform Enterprise 활용 전략 - 폐쇄망 환경에서의 성공 사례
폐쇄망 환경에서 Terraform Enterprise를 활용한 성공 사례와 전략을 소개하는 웨비나. 보안 규제와 네트워크 제한 하에서 인프라 자동화를 구현하는 방법을 다룹니다.
Vault Authentication and Auth Methods: Kubernetes, LDAP, and OKTA - Part 11
Vaultの認証システムにおけるKubernetes、LDAP、OKTAの統合方法を解説。セキュアなアクセス管理と認証プロセスの効率化について学べる。
Deepfake - Threats and Potential Actions
Explore deepfake technology's threats and potential countermeasures in this cybersecurity presentation, highlighting risks and strategies for detection and mitigation.
Log4JMX - The Vulnerability that Never Existed
Explore the intriguing case of Log4JMX, a supposed vulnerability that turned out to be non-existent, in this cybersecurity presentation at DefCamp Cluj-Napoca 2024.
Nix zu verstecken! Erstellung und Veröffentlichung von CVEs für Open Source Software
Erfahrungsbericht zur Erstellung und Veröffentlichung von CVEs für Open-Source-Software. Praktische Einblicke in den Prozess, Vorteile und Herausforderungen als CVE Numbering Authority.
Eine kleine Geschichte über Sicherheitslücken - Erfahrungen mit dem Melden von Sicherheitslücken
Erfahrungsbericht über unbeabsichtigte Entdeckung einer Sicherheitslücke, Umgang mit Behörden und Unternehmen, sowie Tipps für ähnliche Situationen.
La genèse de HADOPI - French Anti-Piracy Law Origins and Impact
Analyse de la loi Hadopi : origines, fonctionnement, efficacité et impact sur la lutte contre le piratage en France. Regard critique sur cette politique controversée.
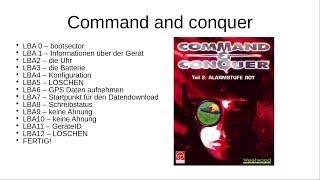
Digital eWaste - Anatomy and Revival of a GPS Device
Anatomie und Wiederbelebung eines GPS-Empfängers: Technische Erkundung zur Reaktivierung obsoleter Geräte durch Reverse-Engineering und Neuentwicklung von Backend-Systemen.
La lucha contra el auge de la inteligencia artificial - BOT-Apocalypse Now
Estrategias para combatir ataques BOT en la era de la IA, enfocándose en amenazas móviles, reducción de costos WAF y protección contra fraudes, DDoS y abusos de API.
Estado de Amenazas y Fraude en América Latina
Análisis experto sobre amenazas cibernéticas y fraudes financieros en América Latina, incluyendo panorama de ataques y grupos delictivos involucrados, presentado por especialista de Kaspersky.
Security Threat Model Analysis and Protection Practice in Edge Computing Scenarios
Analyze security threats in edge computing, explore KubeEdge's audit process, and learn protection practices for cloud-native environments. Gain insights on improving security in multi-cloud and hybrid scenarios.
Como Criar uma ZK-Rollup para Privacidade em Ambiente de CBDC com Besu
Explore a implementação de ZK-rollups para privacidade em CBDCs usando Hyperledger Besu. Aprenda desafios, soluções e aplicações práticas com um especialista em tecnologia financeira.
Überwachung in Sachsen - Wenn die Polizei 1984 als Rechtsgrundlage nutzt
Erfahre mehr über verfassungswidrige Aspekte des sächsischen Polizeigesetzes und deren Auswirkungen auf Überwachungsmaßnahmen. Kritische Analyse der aktuellen Situation und Ausblick.
Der STF und die Tragödie der Digitalen Allmende
Entdecke die Herausforderungen und Lösungsansätze für Open-Source-Nachhaltigkeit und digitale Selbstbestimmung. Erfahre mehr über den Sovereign Tech Fund und seine Initiativen zur Stärkung des Ökosystems.
Staatliche Überwachung: Erfahrungen und Beispiele aus der Praxis
Erfahre, wie staatliche Überwachung funktioniert und wie du dich als Aktivist*in schützen kannst. Lerne über Rechtsgrundlagen, technische Umsetzung und Gegenmaßnahmen.
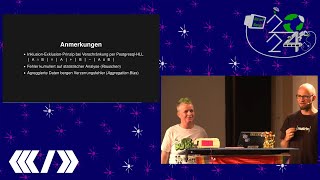
Privatsphäreschonende Gesundheitsdatenverarbeitung
Erfahre, wie Gesundheitsdaten für Forschungszwecke genutzt werden können, ohne die Privatsphäre zu verletzen. Entdecke innovative Ansätze zum Schutz sensibler Informationen im europäischen Gesundheitsdatenraum.
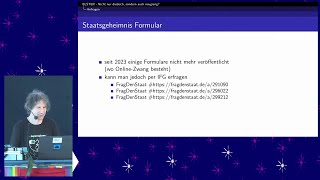
ELSTER - Nicht nur diebisch, sondern auch neugierig? - Datenschutz und DSGVO-Konformität des Steuererklärungssystems
Untersuche die DSGVO-Konformität des Steuererklärungssystems ELSTER und erfahre mehr über Datenschutzbedenken, behördliche Interaktionen und Informationsfreiheitsanfragen.
Give Data Back - Soll ichs wirklich machen oder lass ichs lieber sein?
Erkunde die ethischen Fragen zur Freigabe persönlicher Daten für KI-Training und die Kontrolle über eigene Informationen in großen Sprachmodellen.
Implementando Aplicativos em um Ambiente Seguro com Terraform, Trivy e Postee
Aprenda a implementar aplicativos de forma segura usando Terraform para automação de infraestrutura e ferramentas como Trivy e Postee para identificar e corrigir vulnerabilidades em contêineres.