Securing the DOM from the Bottom Up
Explore techniques for securing the Document Object Model (DOM) from the ground up, enhancing web application security and preventing common vulnerabilities.
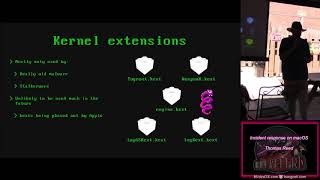
Incident Response on macOS
Learn essential techniques for incident response on macOS, covering forensic collection, login items, kernel extensions, startup items, and more. Gain practical insights for effective Mac security management.
Securing the DOM from the Bottom Up
Explore techniques for securing web applications by fortifying the Document Object Model (DOM) against common vulnerabilities and attacks.
REST in Peace - Abusing GraphQL to Attack Underlying Infrastructure
Explore GraphQL vulnerabilities and attack methodologies, including object reference attacks, mutations, and query cost analysis, to enhance API security awareness.
Stable 19 Swagger Defense
Explore defensive strategies for Swagger-based APIs, focusing on security measures and best practices to protect against common vulnerabilities and attacks.
I Got 99 Problems but a WAF Ain't One
Explore web application firewall (WAF) challenges and solutions in this talk by Micah Brown, covering common issues and effective strategies for implementation and management.
Securing Single Page Applications with Token Based Authentication
Explore token-based authentication for Single Page Applications, including storage methods, revocation strategies, and security considerations for JSON Web Tokens.
SEVEN Things About API Security
Discover essential API security practices, covering authentication, authorization, data protection, and threat mitigation strategies for robust and secure API development.
Securing RESTful Services with Spring HATEOAS and HDIV
Innovative approach to automate protection of Spring HATEOAS services against OWASP Top 10 security risks, integrating Spring HATEOAS with Hdiv security framework for RESTful service security.
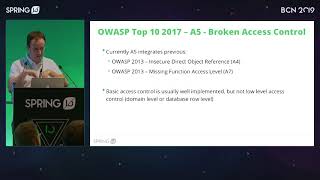
From OWASP Top 10 to Secure Applications
Comprehensive overview of OWASP standards and practical security implementations for Spring applications, covering injection, access control, and various protection tools.
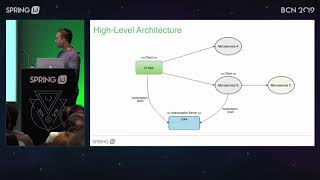
Implementing Microservices Security Patterns & Protocols with Spring Security
Explore industry-standard protocols and Spring Security to build secure microservices. Learn patterns like Web SSO, OAuth2 resource servers, and token exchange for robust, scalable security implementations.
Securing SPAs with Spring
Learn best practices for securing Single Page Applications using Spring Security, covering authentication, authorization, CORS, CSRF, and common attack prevention techniques.
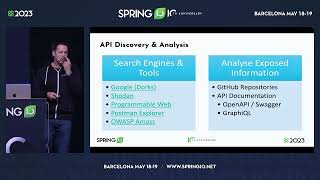
All Your APIs Are Mine - Secure Them Now
Learn to secure Spring APIs against common attacks through live demos, exploring authentication, authorization, and data protection strategies for REST, GraphQL, and gRPC.

Enterprise Security with Spring Authorization Server 1.0
Explore building a customizable OAuth Authorization Server using Spring Authorization Server. Learn best practices, extension points, and enterprise-ready features for secure authentication and authorization.
Securing the Service to Service Call Chain - Patterns and Protocols
Explore key patterns and technologies for securing service-to-service communication, including API Gateways, Service Mesh, SPIFFE, mTLS, JWT, and OpenID Connect, with Spring-based demos and practical implementations.
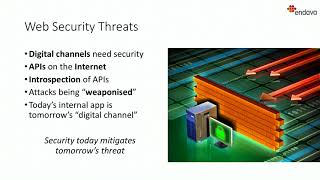
Common Webapp Vulnerabilities and What to Do About Them
Explore common web app vulnerabilities and practical mitigations based on the OWASP Top 10 List, focusing on injection attacks, authentication issues, and data exposure risks.
API Vulnerabilities and What to Do About Them
Explore top API security vulnerabilities and practical mitigations. Learn about OWASP's API Security Top 10, current threat landscape, and essential strategies to protect your APIs from common attacks.

Web Security
Explore 20 years of web cryptography evolution, current transitions in TLS, cipher suites, HTTP security headers, and the move towards encrypted-by-default web.
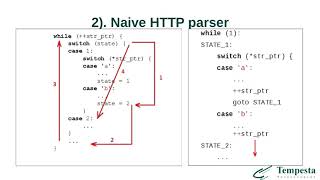
The Linux Network Stack Extension for DDoS Mitigation and Web Security
Explore Tempesta FW, an open-source Linux kernel module for efficient HTTPS traffic filtering and DDoS mitigation. Learn about its integration with the TCP/IP stack and advanced security features.
Securing the DOM from the Bottom Up
Comprehensive approach to mitigating XSS vulnerabilities, integrating tools and techniques for easier secure coding. Insights from Google's security team on achieving high-level safety in web applications.
From Code to Scale! Build a Static Web App in Minutes
Build and deploy static web apps with Azure, featuring CI/CD, custom domains, SSL, APIs, global scaling, and authentication. Learn to go from GitHub repo to worldwide deployment rapidly.