Secure Your Apps with NGINX and the ModSecurity WAF
Learn to protect web applications using NGINX with ModSecurity WAF. Covers WAF basics, ModSecurity features, rule types, OWASP Top 10, custom rules, configurations, and includes a demo.
Bug Bounty - Web Application Penetration Testing Tutorials
Comprehensive tutorials on web application penetration testing, covering tools like Burpsuite, vulnerabilities such as XSS and SQL injection, and practical lab setups for hands-on learning.
Introduction to Web Hacking - OWASP Juice Shop
Comprehensive introduction to web hacking using OWASP Juice Shop, covering essential techniques and vulnerabilities for aspiring ethical hackers and security enthusiasts.
2019 OWASP Top 10 - Part 1
Comprehensive exploration of the first half of OWASP Top 10, covering critical web application security risks and effective mitigation strategies for developers and security professionals.
OWASP Top 10 Training - Part 3
Comprehensive exploration of OWASP Top 10 security vulnerabilities, focusing on prevention strategies and best practices for web application security.
OWASP Top 10 Training - Part 1
Comprehensive overview of OWASP Top 10 security vulnerabilities, focusing on identification, prevention, and mitigation strategies for web application developers and security professionals.
OWASP Top 10 Security Risks - Part 5
Explore the latest OWASP Top 10 security vulnerabilities, their impact, and effective mitigation strategies to enhance web application security and protect against common threats.
OWASP Top 10 Security Risks for Low-Code/No-Code
Explore security vulnerabilities in low-code/no-code apps, learn about the OWASP Top 10 list, and gain insights from real-world examples to enhance application security in modern development environments.
Taking on the King: Killing Injection Vulnerabilities - APPSEC Cali 2018
Explore strategies to combat injection vulnerabilities, including cross-site scripting, with insights on secure coding practices, framework design, and static analysis tools for improved application security.
OWASP Top 10 - Application Security Risks
Explore the latest OWASP Top 10 web application security risks with expert Andrew van der Stock. Learn about critical vulnerabilities and effective mitigation strategies for safer software development.
The Path of Secure Software Development - AppSec EU 2017
Explore proactive security controls for developers to build safer applications. Learn techniques to address common vulnerabilities and integrate security throughout the development lifecycle.
The Gift of Feedback - Enhancing Application Security
Discover how to implement next-generation security by leveraging feedback, pushing security left, and making it consumable. Learn strategies to engage developers and address the challenges of securing complex software workloads.
OWASP Distinguished Lifetime Member Award - Jeff Williams' Contributions
Explore Jeff Williams' contributions to OWASP, including foundational projects, non-profit creation, and innovative security concepts, in this insightful 20th anniversary recognition.
OWASP Top 10 - The Making of the OWASP Top 10 and Beyond
Explore the creation process and principles behind the OWASP Top 10, a crucial resource for web application security, including data analysis, likelihood management, and scoring methodologies.
OWASP Serverless Top 10 - Security Risks and Protections
Explore serverless security risks, challenges, and protective measures. Learn about OWASP Serverless Top 10 and DVSA tool for understanding serverless security implications and processes.
OWASP Top 10 Maturity Categories for Security Champions
Learn to become an effective Security Champion using OWASP's Top 10 Maturity Categories. Explore key responsibilities, maturity models, and strategies for improving organizational security posture.
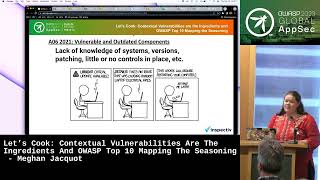
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
How Security, Development, and Testing Can Work Together to Stop Recurring Vulnerabilities - OWASP Top 10
Explore strategies for integrating security, development, and testing to prevent recurring vulnerabilities in the OWASP Top 10, fostering collaboration and cultural change for secure software development.
Post-DevOps: What Should We Shift-Left in Application Security?
Exploring post-DevOps challenges in AppSec, focusing on risk profiles, threat response architecture, and operational aspects to enhance security and quality in fast-paced development environments.
Skillful, Scalable Full-Stack Security in a State of Constant Flux
Approaches to maintaining secure full-stack posture at scale in changing environments. Discusses automation vs. human testing, analytics in continuous security, and scaling with human validation and intelligence.
Introduction to the Newest Addition to the OWASP Top 10 - A9 Guidelines
Experts discuss the new OWASP A9 guideline on insecure open source libraries, offering insights on component usage, best practices, and real-world challenges in mitigating risks in agile development.