OWASP ModSecurity: Web Application Firewall Overview
Explore OWASP ModSecurity's features and implementation for enhancing web application security through this concise presentation by Ervin Hegedüs.
La lucha contra el auge de la inteligencia artificial - BOT-Apocalypse Now
Estrategias para combatir ataques BOT en la era de la IA, enfocándose en amenazas móviles, reducción de costos WAF y protección contra fraudes, DDoS y abusos de API.
Bug Bounty Techniques: Recon, JavaScript Analysis, and Web Security Tools
Insightful discussion on bug bounty techniques, covering recon, JavaScript analysis, WAF bypassing, and utilizing the Wayback Machine for effective vulnerability discovery.
Core Rule Set for the Masses: Lessons from Taming ModSecurity Rules at Massive Scale - 2017
Insights on fine-tuning ModSecurity Core Rule Set at scale, reducing false positives, and optimizing web application firewall performance for large-scale deployments.
Building an AppSec Program with a Budget of $0 - Beyond the OWASP Top 10
Explore OWASP projects to build a comprehensive AppSec program without spending money. Learn how to implement open-source tools for training, development, testing, and defense to create a robust security framework.
Lessons in Securing Internal Apps - AppSecCali 2019
Lessons and strategies for securing internal applications, including authentication, TLS, Content Security Policy, and leveraging WAFs. Insights on scalable approaches and using internal apps to train security engineers.
Innovation Fair for Application and Software Security Startups - OWASP Global AppSec Tel Aviv 2019
Explore innovative startups in application and software security at OWASP's first Innovation Fair. Early-stage companies pitch cutting-edge solutions, offering insights into emerging technologies and market trends.
OWASP Coraza: The Way to WAF in 2023
Explore OWASP Coraza, a cutting-edge Web Application Firewall (WAF) solution, and learn how it enhances web security in 2023 through advanced features and implementation strategies.
Big Data Intelligence - Harnessing Petabytes of WAF Statistics for Web Protection
Explore big data analysis of web application security trends, focusing on WAF statistics, attack patterns, and OWASP ModSecurity Core Rule Set accuracy. Learn to navigate and improve cloud-based web protection.
WAF Bypass Techniques Using HTTP Standard and Web Servers' Behavior
Explore creative techniques to bypass web application firewalls using HTTP standards and server behaviors. Learn to smuggle and reshape requests for penetration testing and bug bounty hunting.
Framework Security: Hugging Developers Through Self-Defending Systems - AppSecEU 2016
Explore framework security strategies, self-defending frameworks, and developer-friendly approaches to enhance application security without code changes or performance impact.
Naxsi: A Web Application Firewall for NGINX
Explore Naxsi, an open-source web application firewall for NGINX, and learn about its features, implementation, and benefits for enhancing web application security.
Getting New Actionable Insights by Analyzing Web Application Firewall Triggers
Explore advanced techniques for analyzing WAF triggers to generate actionable defenses, improve security controls, and gain insights into attacker techniques using real-world case studies.
Malware and Defense Techniques - OWASP AppSec Europe 2014
Explore cutting-edge malware detection, web security, and network defense techniques from industry experts at OWASP AppSec Europe 2014. Gain insights on cloud-based solutions, botnet detection, and advanced web application protection.
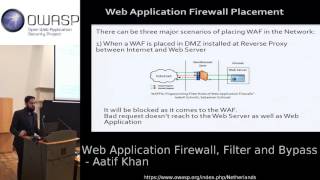
Web Application Firewall - Functionality and Bypass Techniques
Explore web application firewalls, their functionality, and techniques to bypass them in this insightful presentation by security expert Aatif Khan.
Securing Modern Apps with Zero Trust and Next-Gen Web Application Firewall
Explore Zero Trust principles and next-gen Web Application Firewall technology for securing modern cloud applications against sophisticated cyber attacks, featuring Coraza and OWASP CoreRuleSet.
Sucuri Web Application Firewall Review
Comprehensive review of Sucuri's web application firewall, exploring its features, effectiveness, and benefits for website security and protection against online threats.

Nginx ModSecurity Tutorial - Nginx WAF
Learn to secure Nginx with ModSecurity, an open-source web application firewall. Explore real-time request inspection, protection against XSS and SQL injection attacks, and active monitoring for enhanced web server security.

Apache2 ModSecurity Tutorial - Apache2 WAF
Learn to secure Apache2 with ModSecurity, an open-source web application firewall. Explore real-time request inspection, prevention of common attacks, and active monitoring for enhanced web server protection.
Towards Intelligent Application Security
Exploring the evolution of application security and proposing an automated approach integrating security into development and operations, aided by learning techniques and threat intelligence.
Will Machine Learning Replace the WAF?
Explore the potential of machine learning to revolutionize web application firewalls, examining its capabilities, limitations, and impact on cybersecurity.