Tiny Tests, Large Results
Learn to create fast, focused, and reliable atomic e2e tests using Cypress.io for authentication via cookies and JSON Web Tokens, resulting in efficient and impactful testing strategies.
The State of Passwordless Auth on the Web
Explore WebAuthn's potential for passwordless authentication, current user experience, and strategies for building secure, user-friendly auth systems in the evolving landscape of web security.
Authentication from Scratch - Vue.js Amsterdam
Learn to implement authentication from scratch in Vue.js, covering JWT, token-based auth, registration, login, and logout. Gain practical skills for secure user management in Vue applications.
Look Mom, No Passwords! A Developers Guide to WebAuthn
Explore WebAuthn for passwordless authentication, enhancing user experience and security. Learn about the future of web identity and tools for creating user-friendly login systems.
Securing Code with the Python Type System
Explore how Python's type system can enhance code security, from simple annotations to advanced tools, preventing vulnerabilities and enabling incremental improvements in project safety.
MAX - Realtime Messaging and Activity Stream Engine
Explore MAX, an open-source real-time messaging API built on Pyramid, powering a social intranet for 30,000+ users at BarcelonaTech University with high scalability and performance.
Overcoming Access Control in Web APIs
Explore strategies for securing web APIs, including JWT implementation, browser storage best practices, and structured scopes for access control. Learn to overcome security challenges in modern web development.
Let's Talk About JWT
Explore JWT's history, structure, and security implications. Learn to create and validate tokens using PyJWT, understand access vs. ID tokens, and discover best practices for safe implementation.
New Wine in an Old Bottle - Attacking Chrome WebSQL
Explore Chrome WebSQL vulnerabilities and a mutation-based fuzzer for discovering SQLite bugs, enhancing web application security against remote attacks.
Using WebAssembly to Build Fast & Secure Web Apps
Explore WebAssembly's potential for high-performance, secure web apps. Learn how WASM transforms browsers into powerful development environments for building and debugging advanced applications.
Eliminating XSS in Angular Applications by Adopting Trusted Types
Learn to enhance Angular app security using Trusted Types. Discover implementation strategies, vulnerability fixes, and deployment techniques to strengthen your application against XSS attacks and data breaches.
There's Safety in Angular
Explore Angular's built-in security features protecting against common web vulnerabilities, including access control and injection exploits, ensuring safer web development and reduced breach risks.
Staying Safe and Secure with Angular
Learn Angular's built-in security features and best practices to protect your web applications from common vulnerabilities, following OWASP guidelines and implementing authentication safeguards.
OpenID Connect as SSO Solution - Strengths and Weaknesses
Explore OpenID Connect for SSO: its workings, comparisons to SAML, integration examples, common issues, and solutions for non-OIDC applications using Nginx proxy authentication delegation.
Community Integrations and Other Works in Progress
Explore community-driven integrations and initiatives in cloud-native computing, including authentication extensions, user privacy, certificate transparency, and SPIFFE integration with Parsec.
Secure, Efficient API Plane Traversal for Compute Resources on Exascale Super Computers Using SPIRE
Explore SPIRE's role in securing machine-to-machine communication on Cray Shasta exascale supercomputers. Learn about critical communication requirements and why SPIRE is an ideal solution for this high-performance computing environment.
Helping Redistrict California with Ruby
Explore California's unique Ruby-based redistricting system, featuring advanced security measures and a citizen-driven approach to ensure fair electoral districts.
Go Passwordless with WebAuthn in Ruby
Explore WebAuthn for passwordless authentication in Ruby apps. Learn its benefits, implementation, and how it enhances security and user experience using biometrics and public-key cryptography.
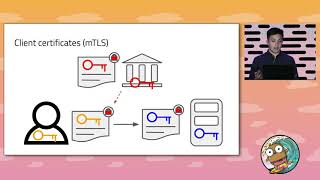
PKI for Gophers
Explore Go primitives for PKI, including certificate hierarchies, mTLS, hardware-backed keys, and public infrastructure. Dive into automated issuance, revocation, and custom PKI implementation.
Secure Coding in Go - Avoiding Common Vulnerabilities
Learn secure coding practices in Go, focusing on common vulnerabilities like injections and XSS. Discover best practices, encryption basics, and proactive security measures for robust application development.
Writing an Insecure Webapp
Explore common web app vulnerabilities and learn effective security practices to protect against threats like cross-site scripting and ensure robust application safety.