
JWT - JSON Web Token Crash Course - NodeJS & Postgres
Comprehensive guide to JWT authentication, covering session-based and JWT-based methods, refresh tokens, asymmetric JWT, and practical implementation with Node.js and Postgres.
Introduction to Quarkus Security
Explore Quarkus and its Security Architecture in this 52-minute conference talk from Devoxx. Discover how Quarkus solves real-world security challenges while prioritizing Developer Joy. Learn to develop and test OpenID Connect-secured services in Dev mod…

Cookies
Learn about HTTP cookies, JWT, SameSite attributes, and third-party cookies. Explore implementation examples, browser behaviors, and real-world applications in web security and user tracking.

Spring Boot and Spring Security with JWT Including Access and Refresh Tokens
Learn to secure backend applications using JWT, Spring Boot, and Spring Security. Implement access and refresh tokens for robust authentication and authorization.

Cookies, Sessions, JSON Web Tokens -JWT- and More
Explore web security essentials: cookies, CSRF protection, sessions, JWT, and localStorage. Learn how servers authenticate and remember users for secure web development.
Building Modern Access-Control for Cloud Applications with Or Weis - SnykLIVE Recording
Explore modern access control for cloud apps using policy-as-code, best practices, and open-source tools like OPA and OPAL. Learn to tackle complexity in microservices architectures.
Building Data Breach and Subpoena Resistant Applications - Philly ETE 2017
Explore cryptographic techniques and messaging systems to build applications resistant to data breaches and subpoenas, setting new standards for user data security.
Attacking JWT - Header Injection Techniques
Learn techniques for attacking JSON Web Tokens through header injections, including algorithm and JWK header attacks. Gain practical insights into exploiting JWT vulnerabilities.

Cracking JSON Web Tokens - Understanding Security Vulnerabilities
Learn to understand, test, and crack JSON Web Tokens (JWTs) for enhanced web application security. Explore JWT structure, vulnerabilities, and best practices for implementation and protection.
JWTs - Patterns and Anti-patterns in Authentication
Explore JWT use cases, patterns, and anti-patterns for secure authentication. Learn best practices and alternatives for implementing stateless tokens in web applications.
API Security Best Practices and Guidelines - 2016
Explore industry-leading best practices for designing secure APIs, navigating standards, and protecting both public and private APIs to maximize benefits while keeping threats at bay.
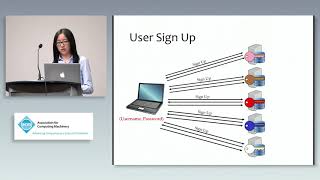
PASTA - Password-Based Threshold Authentication
Explore password-based threshold authentication with PASTA, a novel framework distributing identity verification among servers for enhanced security against token forgery and offline attacks.
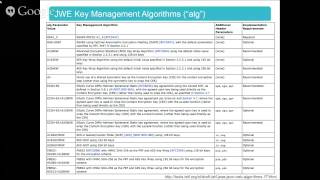
Introduction to Emerging JSON-Based ID and Security Protocols
Explore emerging JSON-based identity and security protocols with Brian Campbell, focusing on JOSE and its applications in modern authentication and authorization systems.
Implementing a User-Centric Datastore with Privacy-Aware Access Control for Cloud-Based Data Platforms
Explore user-centric data storage with privacy-aware access control for cloud platforms. Learn about implementation, components, and challenges in this informative talk on secure data management.
How Web Authentication Works: TLS, Password Hashing, OpenID Connect, OAuth 2, and JSON Web Tokens
Explore the inner workings of web authentication, covering TLS, password hashing, OpenID Connect, OAuth 2, and JSON Web Tokens in this comprehensive overview.
JWTs for CSRF and Microservices - Secure Implementation Examples
Learn to implement JWT-based CSRF protection and establish trust between microservices using JWTs, with practical code examples and insights into secure microservice architecture.
Adding Authentication to Apps with Okta - Learn With Jason
Implement user authentication in Gatsby apps using Okta. Learn to set up secure user accounts, integrate sign-in widgets, and manage JSON Web Tokens for enhanced app functionality.

Opening Doors with JSON Web Tokens - Securing IoT Access
Explore secure IoT door access using JSON Web Tokens, NFC, and mobile apps. Learn innovative techniques for remote authorization without direct internet connection, balancing convenience and safety.

Authenticating Single Page Apps Using JSON Web Tokens
Learn to implement secure authentication in single page apps using OpenID Connect and JSON Web Tokens, enhancing user experience and application security.

Secure CI/CD Using JSON Web Token (JWT)
Explore how GitLab leverages JWT for secure access to secret management solutions, enhancing DevSecOps practices and addressing challenges in retrieving sensitive data across cloud providers.
Handling JWTs: Understanding Common Pitfalls
Explore JWT authentication, common pitfalls, and security best practices. Learn about JWT structure, verification, and protection against attacks like algorithm confusion and secret brute-forcing.