OWASP CSRFGuard: Understanding and Preventing Cross-Site Request Forgery
Learn to prevent Cross-Site Request Forgery attacks with OWASP CSRFGuard. Explore real-world examples, detection techniques, and implementation strategies for robust web application security.
The Timing Attacks They Are A-Changin' - Web-based and Browser-based Timing Attack Techniques
Explore evolving timing attacks in web security, from classic cross-site techniques to browser-based methods, and learn effective mitigation strategies.
Security Implications of Cross-Origin Resource Sharing - HTML5 and CORS Analysis
Explore security implications of Cross-Origin Resource Sharing in HTML5, including its impact on same-origin policy, potential vulnerabilities, and mitigation strategies for web application developers.
Warning Ahead: Security Storms Brewing in JavaScript
Explore JavaScript vulnerabilities, including unique issues, third-party platform exploits, and HTML5 risks. Learn about emerging security threats and their impact on enterprise data and user safety.
Client-Side Protection Against DOM-Based XSS Done Right
Comprehensive overview of client-side protection against DOM-based XSS attacks, covering vulnerabilities, prevention techniques, and practical solutions for web security professionals.
CSP Pitfalls and Gotchas
Explore common pitfalls and gotchas in Content Security Policy implementation, focusing on whitelist issues, SameOrigin policy, and unsafe inline practices. Learn strategies for building a robust security framework.
The "Web/Local" Boundary Is Fuzzy - A Security Study of Chrome's Process-based Sandboxing
Explore Chrome's process-based sandboxing, its security implications, and potential vulnerabilities in web browser architecture. Learn about attacks exploiting the fuzzy web/local boundary.
Same Origin Method Execution - Exploiting a Callback for Same Origin Policy Bypass
Explore a powerful web attack technique that exploits JSONP to bypass Same Origin Policy, potentially compromising entire domains without user interaction or typical browser protections.
Session Identifier are for Now, Passwords are Forever - XSS-Based Abuse of Browser Password Managers
Explore XSS-based attacks on browser password managers, their vulnerabilities, and potential solutions. Learn about password field usage on popular websites and get recommendations for protection.
Bypassing Browser Security Policies for Fun and Profit
Explore mobile browser vulnerabilities and security policy bypasses, including Same Origin Policy and Content Security Policy. Learn testing methodologies and see real-world examples of Android browser exploits.
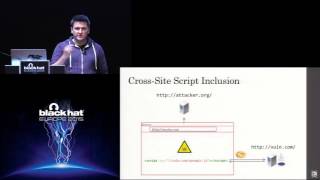
Your Scripts In My Page - What Could Possibly Go Wrong?
Explore the security risks of cross-domain script inclusion, including potential data leaks and account compromises. Learn detection methods and defensive measures to protect against these vulnerabilities.
Browsers Gone Wild
Unveiling creative browser vulnerabilities and attacks, including confidentiality breaches, login detection, and exploiting HTML5 features, with live demonstrations challenging Same Origin Policy understanding.
The Deputies Are Still Confused
Exploring misunderstandings and vulnerabilities in same-origin policy, with practical examples of attacks bypassing common content-isolation mechanisms for CSRF, clickjacking, and NTLM protection.
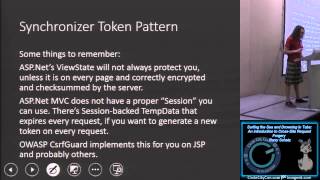
Surfing the Sea and Drowning in Tabs - An Introduction to Cross Site Request Forgery
Explore Cross Site Request Forgery: its mechanisms, prevention strategies, and real-world implications. Learn about same-origin policy, viewstate, headers, and encrypted token patterns.

Black Hat USA 2025
Black Hat USA 2025

Black Hat Europe 2023
Black Hat Europe 2023

Black Hat Europe 2024
Black Hat Europe 2024