WAF Bypass Techniques Using HTTP Standard and Web Servers' Behavior
Explore creative techniques to bypass web application firewalls using HTTP standards and server behaviors. Learn to smuggle and reshape requests for penetration testing and bug bounty hunting.

HTTP Request Smuggling - Web Application Hacking Techniques
Explore HTTP Request Smuggling techniques for web application security, uncovering vulnerabilities and enhancing your hacking skills.
Request Smuggling 101
Explore HTTP Request Smuggling attacks, risks, and payloads. Learn to detect and mitigate vulnerabilities in load balancers and proxies. Includes live demonstration and practical mitigation strategies.
Ekoparty #UniTalks Colombia - HTTP Request Smuggling
Explicación detallada sobre la vulnerabilidad HTTP Request Smuggling, sus implicaciones en la seguridad web y cómo los atacantes pueden explotarla para ejecutar diversos ataques en aplicaciones con arquitecturas de múltiples servidores.
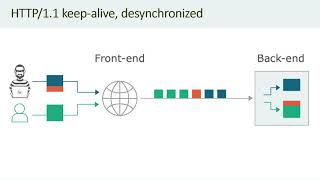
HTTP Desync Attacks - Request Smuggling Reborn
Explore HTTP request smuggling techniques to bypass security, manipulate web infrastructure, and exploit vulnerabilities. Learn detection, confirmation, and exploitation methods for various attack scenarios.
HTTP Request Smuggling in 2020 - New Variants, New Defenses and New Challenges
Explore new variants, defenses, and challenges of HTTP Request Smuggling, an attack technique exploiting interpretations of non-standard HTTP requests between client and server.
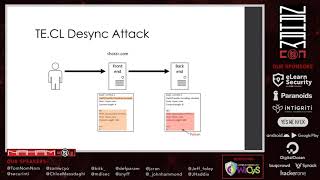
Practical Attacks Using HTTP Request Smuggling
Explore practical HTTP request smuggling attacks, including CL.TE/TE.CL desync techniques, testing methods, and real-world examples. Learn to exploit vulnerabilities for session stealing and response queue poisoning.
Modern Web Vulnerabilities 2020
Explore modern web vulnerabilities, including insecure deserialization, SSRF, ESI injection, prototype pollution, and HTTP request smuggling, with demos and prevention strategies.
Leveraging HTTP Request Smuggling for Authentication Bypass and Remote Code Execution
Delve into HTTP Request Smuggling vulnerabilities, exploring real-world cases of authentication bypass and remote code execution in enterprise applications, with practical detection and mitigation strategies.
The Art of Bypassing Web Application Firewalls - Live Demos
Explore hands-on techniques for bypassing modern web application firewalls. Learn to customize methods and payloads through practical labs, enhancing your skills in WAF evasion and web security.

Black Hat USA 2025
Black Hat USA 2025

Black Hat Europe 2023
Black Hat Europe 2023

Black Hat Asia 2025
Black Hat Asia 2025