OPSEC and Personal Security Guide - Cybertalk Episode 7
Comprehensive guide on personal security and OPSEC, covering tools, techniques, and best practices to enhance digital safety and protect against cyber threats.
Detecting and Controlling Rogue Third-Party Scripts in Web Applications
Explore web supply chain attacks, their impact on sensitive data, and strategies to detect and prevent rogue third-party scripts from compromising web application security.
Mind the CSP Gap: Challenges Developing a Meaningful Content-Security-Policy
Strategies for implementing Content Security Policy (CSP) effectively, addressing challenges and phasing in a meaningful policy without disrupting engineering teams.
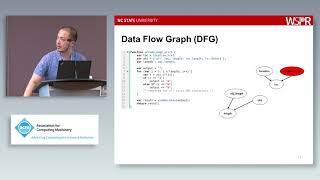
Mystique - Uncovering Information Leakage from Browser Extensions
Explore privacy risks of browser extensions, uncovering information leakage through taint tracking and data flow analysis techniques.
Browser Exploitation - Max Zinkus
Explore JavaScript-based browser exploitation techniques, including XSS, JIT compilation vulnerabilities, and shellcode execution. Learn about browser security measures and how to find and chain exploits.
Security for the People: End-User Authentication on the Internet - Mark Stanislav
Learn about end-user authentication security on the internet, covering two-factor deployments, browser security features, SSL/TLS implementations, and more. Gain insights into research methodology and lessons learned.
Practical Side Channel Attacks on Modern Browsers - Lecture 6
Explore practical side channel attacks on modern browsers, covering XSS filters, timing attacks, clipboard vulnerabilities, and more. Learn about login history exploits and data URI schemes.
Out of Character Use of Punycode and Homoglyph Attacks to Obfuscate URLs for Phishing
Explore techniques for URL obfuscation in phishing attacks, including punycode and homoglyphs. Learn about browser protections, registrar defenses, and strategies to mitigate these threats.
Edgeguard: Client-side DOM Security Framework for Detecting Malicious Content - APPSEC Cali 2018
Introducing Edgeguard: an open framework for detecting malicious content in browsers that steals sensitive user data. Learn about this zero-footprint library's approach to enhancing client-side DOM security.

Beyond End-to-End Encryption: Threat Models for Secure Messaging
Explore evolving threat models for secure messaging, covering advanced attacker capabilities, real-world vulnerabilities, and emerging challenges in cybersecurity and privacy protection.
Exploiting CORS Misconfigurations for Bitcoins and Bounties - AppSec EU 2017
Explore CORS misconfigurations and their security implications, including real-world attacks on bitcoin exchanges and Google. Learn about subtle vulnerabilities and exploit techniques for web security professionals.
Trusted Types: End-to-End Injection Safety at Scale
Learn about Google's approach to achieving high-level XSS safety through integrated tools and developer-friendly practices, with insights on implementing similar security in open-source stacks.
Trusted Types: A World Without XSS
Explore cutting-edge web security with Trusted Types, a powerful defense against XSS attacks. Learn implementation strategies and best practices from industry experts.
HTTPS Everywhere: Improving Web Security and Usability
Exploring Chrome's efforts to enhance HTTPS adoption: tools for debugging, reporting mechanisms for safe rollout, and strategies to improve web security.
New Methods in Automated XSS Detection - Dynamic Testing Without Static Payloads
Explore innovative dynamic methods for automated XSS detection without static payloads, including techniques for Stored XSS and custom exploit generation. Learn to overcome limitations of traditional approaches.
OCSP Stapling in the Wild - Lecture
Explore OCSP stapling in the wild with experts Devdatta Akhawe and Emily Stark. Learn about TLS security, browser implementations, and real-world challenges in HTTPS ecosystems.
Dissecting Browser Privacy
Explore browser privacy with a senior security engineer from Brave, covering key issues and advancements in protecting user data while browsing the web.
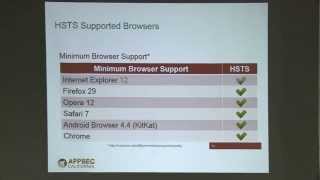
Proactively Defending Your Business Against Security Protocol Attacks - OWASP AppSec California 2015
Explore strategies to proactively defend against security protocol attacks and implementation flaws in HTTPS/SSL/TLS. Learn about recent vulnerabilities, mitigations, and best practices for secure communications.

Making Content Security Policy Work For You
Learn about Content Security Policy (CSP), its importance in web application defense, and practical tips for implementation from Mozilla's application security expert.
Libinjection: From SQLi to XSS Detection - New Algorithm Introduction
Explore advanced techniques for detecting SQLi and XSS attacks using libinjection, a fast and accurate algorithm. Learn about its implementation, benefits, and future developments in web security.
The Perilous Future of Browser Security
Explore browser security challenges, tradeoffs, and solutions. Learn about critical vulnerabilities, secure browser design, and balancing security with user experience in the face of evolving threats.